Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Fortinet Warns of New FortiWeb CVE-2025-58034 Vulnerability Exploited in the Wild

Fortinet Warns of New FortiWeb CVE-2025-58034 Vulnerability Exploited in the Wild

Posted on November 19, 2025November 19, 2025 By CWS

Nov 19, 2025Ravie LakshmananVulnerability / Community Safety
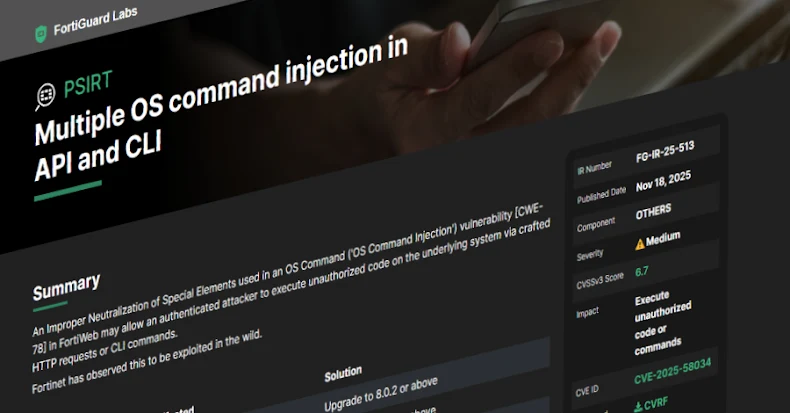
Fortinet has warned of a brand new safety flaw in FortiWeb that it mentioned has been exploited within the wild.
The medium-severity vulnerability, tracked as CVE-2025-58034, carries a CVSS rating of 6.7 out of a most of 10.0.
“An Improper Neutralization of Particular Components utilized in an OS Command (‘OS Command Injection’) vulnerability [CWE-78] in FortiWeb could enable an authenticated attacker to execute unauthorized code on the underlying system by way of crafted HTTP requests or CLI instructions,” the corporate mentioned in a Tuesday advisory.
In different phrases, profitable assaults require an attacker to first authenticate themselves via another means and chain it with CVE-2025-58034 to execute arbitrary working system instructions.

It has been addressed within the following variations –

FortiWeb 8.0.0 via 8.0.1 (Improve to eight.0.2 or above)
FortiWeb 7.6.0 via 7.6.5 (Improve to 7.6.6 or above)
FortiWeb 7.4.0 via 7.4.10 (Improve to 7.4.11 or above)
FortiWeb 7.2.0 via 7.2.11 (Improve to 7.2.12 or above)
FortiWeb 7.0.0 via 7.0.11 (Improve to 7.0.12 or above)

The corporate credited Development Micro researcher Jason McFadyen for reporting the flaw below its accountable disclosure coverage.
Apparently, the event comes days after Fortinet confirmed that it silently patched one other vital FortiWeb vulnerability (CVE-2025-64446, CVSS rating: 9.1) in model 8.0.2.
“We activated our PSIRT response and remediation efforts as quickly as we discovered of this matter, and people efforts stay ongoing,” a Fortinet spokesperson informed The Hacker Information. “Fortinet diligently balances our dedication to the safety of our clients and our tradition of accountable transparency.”
It is at the moment not clear why Fortinet opted to patch the failings with out releasing an advisory. However the transfer has left defenders at an obstacle, successfully stopping them from mounting an enough response.
“When in style know-how distributors fail to speak new safety points, they’re issuing an invite to attackers whereas selecting to maintain that very same info from defenders,” VulnCheck famous final week.
The Hacker News Tags:CVE202558034, Exploited, Fortinet, FortiWeb, Vulnerability, Warns, Wild

Post navigation

Previous Post: Cloudflare Discloses Technical Details Behind Massive Outage that Breaks the Internet
Next Post: New FortiWeb 0-Day Code Execution Vulnerability Exploited in the Wild

Related Posts

Chinese Hackers Weaponize Open-Source Nezha Tool in New Attack Wave Chinese Hackers Weaponize Open-Source Nezha Tool in New Attack Wave The Hacker News
CISA Flags SolarWinds Vulnerability in Security Alert CISA Flags SolarWinds Vulnerability in Security Alert The Hacker News
AI Enhances Security Testing in Dynamic Environments AI Enhances Security Testing in Dynamic Environments The Hacker News
INTERPOL Arrests 1,209 Cybercriminals Across 18 African Nations in Global Crackdown INTERPOL Arrests 1,209 Cybercriminals Across 18 African Nations in Global Crackdown The Hacker News
FBI Warns FSB-Linked Hackers Exploiting Unpatched Cisco Devices for Cyber Espionage FBI Warns FSB-Linked Hackers Exploiting Unpatched Cisco Devices for Cyber Espionage The Hacker News
Amazon Disrupts APT29 Watering Hole Campaign Abusing Microsoft Device Code Authentication Amazon Disrupts APT29 Watering Hole Campaign Abusing Microsoft Device Code Authentication The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark