Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Ransomware Targets Synology NAS, Urgent Updates Needed

Ransomware Targets Synology NAS, Urgent Updates Needed

Posted on November 3, 2026 By CWS

In a recent security alert, Synology has urged its customers to update the DiskStation Manager (DSM) software on their Network Attached Storage (NAS) devices. This comes in response to ransomware attacks that have exploited a previously addressed vulnerability.

Exploitation of Known Vulnerabilities

The Taiwanese tech company reported that cybercriminals are targeting DSM systems using a flaw that was patched in December 2024. The primary goal of these attacks is to encrypt users’ data and demand a ransom for decryption.

Although Synology did not specify the exact vulnerability being exploited, it referenced a security advisory from November 2024. This advisory detailed three vulnerabilities: CVE-2024-10441, CVE-2024-50629, and CVE-2024-10445, each with different levels of severity and potential impacts on the DSM system.

Security Patches and Updates

Synology highlighted that these vulnerabilities have been mitigated in recent DSM updates. Users are advised to upgrade to the following DSM versions or newer: 7.2.2-72806-1 for DSM 7.2.2, 7.2.1-69057-6 for DSM 7.2.1, 7.2-64570-4 for DSM 7.2, 7.1.1-42962-7 for DSM 7.1, and 6.2.4-25556-8 for DSM 6.2.

Recent reports indicate that C3RB3R ransomware has been encrypting files on Synology devices, appending a “.L0CK3D” extension to compromised files. This highlights the urgent need for users to update their systems.

Historical Context and Recommendations

Synology NAS devices have previously been targeted by various ransomware attacks. In 2019, QNAP Systems’ NAS devices were affected by the QNAPCrypt ransomware. A similar threat emerged in August 2021 when Synology devices faced brute-force attacks from the StealthWorker malware family, leading to additional ransomware incidents.

To safeguard against these threats, Synology strongly advises users to update their DSM to the latest versions and enable automatic updates. This proactive measure is crucial to ensure the security of their data and the integrity of their systems.

In conclusion, maintaining updated DSM software is vital for protecting Synology NAS devices from ransomware threats. Users should remain vigilant and implement recommended security practices to prevent unauthorized access and potential data loss.

The Hacker News Tags:automatic updates, C3RB3R ransomware, CVE vulnerabilities, cyber attack, Cybersecurity, data encryption, data protection, DSM update, NAS, network security, Ransomware, security advisory, software patch, Synology, tech news

Post navigation

Previous Post: OpenAI Boosts Security with New Vulnerability Sprint
Next Post: NATO’s Cyber Defense Exercise Integrates AI Innovations

Related Posts

OpenAI Investigates AI Agents Exploiting Vulnerabilities OpenAI Investigates AI Agents Exploiting Vulnerabilities The Hacker News
SolarWinds WHD Exploited in Complex Multi-Stage Cyber Attacks SolarWinds WHD Exploited in Complex Multi-Stage Cyber Attacks The Hacker News
Five New Exploited Bugs Land in CISA’s Catalog — Oracle and Microsoft Among Targets Five New Exploited Bugs Land in CISA’s Catalog — Oracle and Microsoft Among Targets The Hacker News
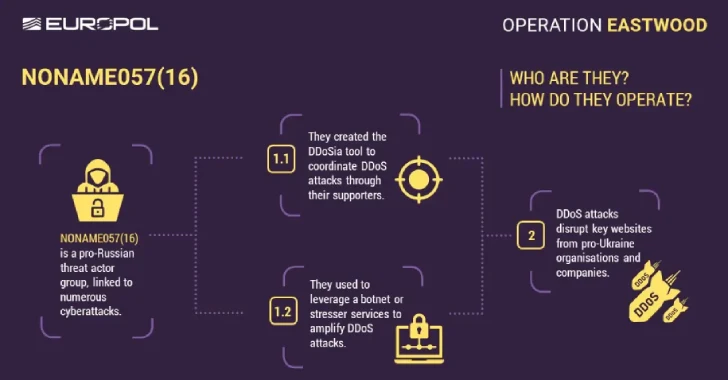
Europol Disrupts NoName057(16) Hacktivist Group Linked to DDoS Attacks Against Ukraine Europol Disrupts NoName057(16) Hacktivist Group Linked to DDoS Attacks Against Ukraine The Hacker News
Cryptojacking Campaign Exploits DevOps APIs Using Off-the-Shelf Tools from GitHub Cryptojacking Campaign Exploits DevOps APIs Using Off-the-Shelf Tools from GitHub The Hacker News
Secure AI at Scale and Speed — Learn the Framework in this Free Webinar Secure AI at Scale and Speed — Learn the Framework in this Free Webinar The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • UK Faces AI Cyber Threats on Infrastructure by 2028
  • Security Flaw in BTCPay Server Risks Bitcoin and Litecoin Theft
  • NATO’s Cyber Defense Exercise Integrates AI Innovations
  • Ransomware Targets Synology NAS, Urgent Updates Needed
  • OpenAI Boosts Security with New Vulnerability Sprint

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • UK Faces AI Cyber Threats on Infrastructure by 2028
  • Security Flaw in BTCPay Server Risks Bitcoin and Litecoin Theft
  • NATO’s Cyber Defense Exercise Integrates AI Innovations
  • Ransomware Targets Synology NAS, Urgent Updates Needed
  • OpenAI Boosts Security with New Vulnerability Sprint

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark