Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
UNC2891 Breaches ATM Network via 4G Raspberry Pi, Tries CAKETAP Rootkit for Fraud

UNC2891 Breaches ATM Network via 4G Raspberry Pi, Tries CAKETAP Rootkit for Fraud

Posted on July 31, 2025July 31, 2025 By CWS

Jul 31, 2025Ravie Lakshmanan
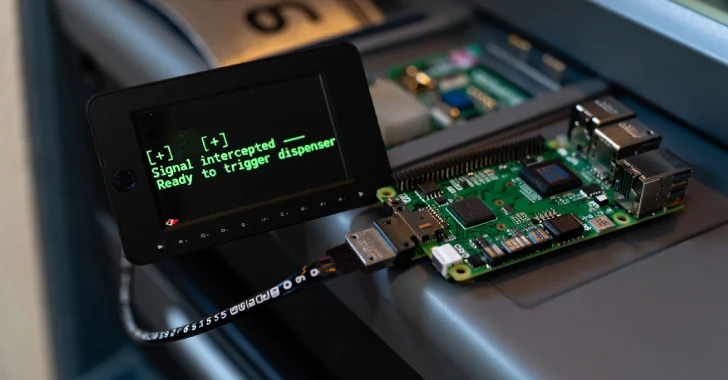
The financially motivated menace actor referred to as UNC2891 has been noticed focusing on Computerized Teller Machine (ATM) infrastructure utilizing a 4G-equipped Raspberry Pi as a part of a covert assault.
The cyber-physical assault concerned the adversary leveraging their bodily entry to put in the Raspberry Pi gadget and have it related on to the identical community swap because the ATM, successfully putting it inside the goal financial institution’s community, Group-IB mentioned. It is at the moment not identified how this entry was obtained.
“The Raspberry Pi was outfitted with a 4G modem, permitting distant entry over cellular knowledge,” safety researcher Nam Le Phuong mentioned in a Wednesday report.

“Utilizing the TINYSHELL backdoor, the attacker established an outbound command-and-control (C2) channel by way of a Dynamic DNS area. This setup enabled steady exterior entry to the ATM community, utterly bypassing perimeter firewalls and conventional community defenses.”
UNC2891 was first documented by Google-owned Mandiant in March 2022, linking the group to assaults focusing on ATM switching networks to hold out unauthorized money withdrawals at completely different banks utilizing fraudulent playing cards.
Central to the operation was a kernel module rootkit dubbed CAKETAP that is designed to cover community connections, processes, and recordsdata, in addition to intercept and spoof card and PIN verification messages from {hardware} safety modules (HSMs) to allow monetary fraud.

The hacking crew is assessed to share tactical overlaps with one other menace actor UNC1945 (aka LightBasin), which was beforehand recognized compromising managed service suppliers and putting targets inside the monetary {and professional} consulting industries.
Describing the menace actor as possessing intensive data of Linux and Unix-based techniques, Group-IB mentioned its evaluation uncovered backdoors named “lightdm” on the sufferer’s community monitoring server which might be designed to determine energetic connections to the Raspberry Pi and the inner Mail Server.

The assault is critical for the abuse of bind mounts to cover the presence of the backdoor from course of listings and evade detection.
The top purpose of the an infection, as seen up to now, is to deploy the CAKETAP rootkit on the ATM switching server and facilitate fraudulent ATM money withdrawals. Nonetheless, the Singaporean firm mentioned the marketing campaign was disrupted earlier than the menace actor might inflict any severe harm.
“Even after the Raspberry Pi was found and eliminated, the attacker maintained inner entry by way of a backdoor on the mail server,” Group-IB mentioned. “The menace actor leveraged a Dynamic DNS area for command-and-control.”
The Hacker News Tags:ATM, Breaches, CAKETAP, Fraud, Network, Raspberry, Rootkit, UNC2891

Post navigation

Previous Post: Alert Fatigue, Data Overload, and the Fall of Traditional SIEMs
Next Post: 20 Best Kubernetes Monitoring Tools in 2025

Related Posts

Breaches Hidden, Attack Surfaces Growing, and AI Misperceptions Rising Breaches Hidden, Attack Surfaces Growing, and AI Misperceptions Rising The Hacker News
Top Cyber Threats for US Businesses in October 2026 Top Cyber Threats for US Businesses in October 2026 The Hacker News
Red Heron Uses Gitea Exploit to Breach Global Firms Red Heron Uses Gitea Exploit to Breach Global Firms The Hacker News
n8n Warns of CVSS 10.0 RCE Vulnerability Affecting Self-Hosted and Cloud Versions n8n Warns of CVSS 10.0 RCE Vulnerability Affecting Self-Hosted and Cloud Versions The Hacker News
New MacSync macOS Stealer Uses Signed App to Bypass Apple Gatekeeper New MacSync macOS Stealer Uses Signed App to Bypass Apple Gatekeeper The Hacker News
New UEFI Flaw Enables Early-Boot DMA Attacks on ASRock, ASUS, GIGABYTE, MSI Motherboards New UEFI Flaw Enables Early-Boot DMA Attacks on ASRock, ASUS, GIGABYTE, MSI Motherboards The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark