Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
OneLogin Bug Let Attackers Use API Keys to Steal OIDC Secrets and Impersonate Apps

OneLogin Bug Let Attackers Use API Keys to Steal OIDC Secrets and Impersonate Apps

Posted on October 1, 2025October 1, 2025 By CWS

Oct 01, 2025Ravie LakshmananVulnerability / API Safety
A high-severity safety flaw has been disclosed within the One Identification OneLogin Identification and Entry Administration (IAM) resolution that, if efficiently exploited, may expose delicate OpenID Join (OIDC) utility consumer secrets and techniques below sure circumstances.
The vulnerability, tracked as CVE-2025-59363, has been assigned a CVSS rating of seven.7 out of 10.0. It has been described as a case of incorrect useful resource switch between spheres (CWE-669), which causes a program to cross safety boundaries and acquire unauthorized entry to confidential knowledge or features.

CVE-2025-59363 “allowed attackers with legitimate API credentials to enumerate and retrieve consumer secrets and techniques for all OIDC functions inside a corporation’s OneLogin tenant,” Clutch Safety mentioned in a report shared with The Hacker Information.

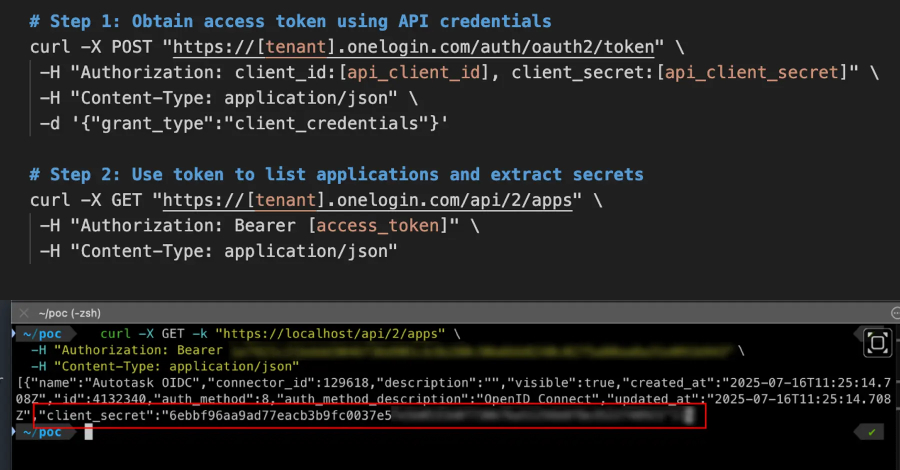
The identification safety mentioned the issue stems from the truth that the applying itemizing endpoint – /api/2/apps – was configured to return extra knowledge than anticipated, together with the client_secret values within the API response alongside metadata associated to the apps in a OneLogin account.
The steps to drag off the assault are listed under –

Attacker makes use of legitimate OneLogin API credentials (consumer ID and secret) to authenticate
Request entry token
Name the /api/2/apps endpoint to record all functions
Parse the response to retrieve consumer secrets and techniques for all OIDC functions
Use extracted consumer secrets and techniques to impersonate functions and entry built-in companies

Profitable exploitation of the flaw may permit an attacker with legitimate OneLogin API credentials to retrieve consumer secrets and techniques for all OIDC functions configured inside a OneLogin tenant. Armed with this entry, the menace actor may leverage the uncovered secret to impersonate customers and achieve entry to different functions, providing alternatives for lateral motion.
OneLogin’s role-based entry management (RBAC) grants API keys broad endpoint entry, that means the compromised credentials could possibly be used to entry delicate endpoints throughout your complete platform. Compounding issues additional is the dearth of IP deal with allowlisting, because of which it is potential for attackers to use the flaw from wherever on the planet, Clutch famous.

Following accountable disclosure on July 18, 2025, the vulnerability was addressed in OneLogin 2025.3.0, which was launched final month by making OIDC client_secret values not seen. There isn’t any proof that the problem was ever exploited within the wild.
“Identification suppliers function the spine of enterprise safety structure,” Clutch Safety mentioned. “Vulnerabilities in these methods can have cascading results throughout complete expertise stacks, making rigorous API safety important.”

The Hacker News Tags:API, Apps, Attackers, Bug, Impersonate, Keys, OIDC, OneLogin, Secrets, Steal

Post navigation

Previous Post: Learn How Leading Security Teams Blend AI + Human Workflows (Free Webinar)
Next Post: MatrixPDF Attacks Gmail Users Bypassing Email Filters and Fetch Malicious Payload

Related Posts

Infostealer Targets OpenClaw AI, Exposes Security Flaws Infostealer Targets OpenClaw AI, Exposes Security Flaws The Hacker News
A Browser Extension Risk Guide After the ShadyPanda Campaign A Browser Extension Risk Guide After the ShadyPanda Campaign The Hacker News
MSS Claims NSA Used 42 Cyber Tools in Multi-Stage Attack on Beijing Time Systems MSS Claims NSA Used 42 Cyber Tools in Multi-Stage Attack on Beijing Time Systems The Hacker News
Mandiant Finds ShinyHunters-Style Vishing Attacks Stealing MFA to Breach SaaS Platforms Mandiant Finds ShinyHunters-Style Vishing Attacks Stealing MFA to Breach SaaS Platforms The Hacker News
Cline CLI Supply Chain Breach Installs OpenClaw Cline CLI Supply Chain Breach Installs OpenClaw The Hacker News
Russian Cyber Campaign Targets Ukraine with New Malware Russian Cyber Campaign Targets Ukraine with New Malware The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark