Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft Links Storm-1175 to GoAnywhere Exploit Deploying Medusa Ransomware

Microsoft Links Storm-1175 to GoAnywhere Exploit Deploying Medusa Ransomware

Posted on October 7, 2025October 7, 2025 By CWS

Oct 07, 2025Ravie LakshmananVulnerability / Cloud Safety
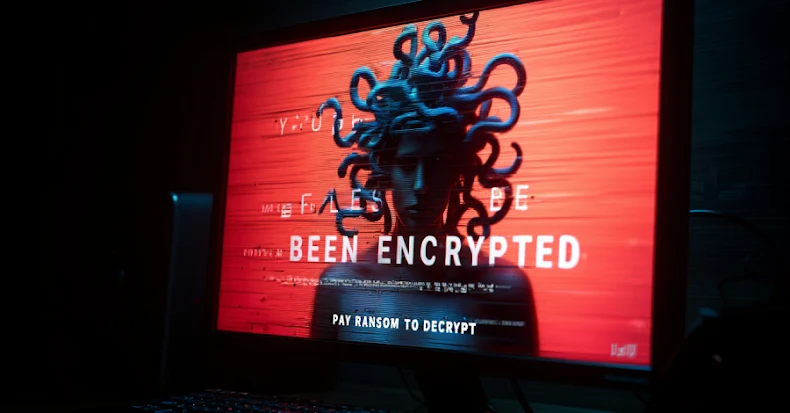
Microsoft on Monday attributed a risk actor it tracks as Storm-1175 to the exploitation of a vital safety flaw in Fortra GoAnywhere software program to facilitate the deployment of Medusa ransomware.
The vulnerability is CVE-2025-10035 (CVSS rating: 10.0), a vital deserialization bug that might end in command injection with out authentication. It was addressed in model 7.8.4, or the Maintain Launch 7.6.3.
“The vulnerability may permit a risk actor with a validly solid license response signature to deserialize an arbitrary actor-controlled object, presumably resulting in command injection and potential distant code execution (RCE),” the Microsoft Menace Intelligence group mentioned.
Based on the tech big, Storm-1175 is a cybercriminal group identified for deploying Medusa ransomware and exploiting public-facing purposes for preliminary entry since September 11, 2025. It is price noting that watchTowr revealed final week that there have been indications of lively exploitation of the flaw since no less than September 10.

Moreover, profitable exploitation of CVE-2025-10035 may permit attackers to carry out system and person discovery, keep long-term entry, and deploy extra instruments for lateral motion and malware.
The assault chain following preliminary entry entails dropping distant monitoring and administration (RMM) instruments, resembling SimpleHelp and MeshAgent, to keep up persistence. The risk actors have additionally been noticed creating .jsp information throughout the GoAnywhere MFT directories, typically similtaneously the dropped RMM instruments.
Within the subsequent section, instructions for person, community, and system discovery are executed, adopted by leveraging mstsc.exe (i.e., Home windows Distant Desktop Connection) for lateral motion throughout the community.
The downloaded RMM instruments are used for command-and-control (C2) utilizing a Cloudflare tunnel, with Microsoft observing using Rclone in no less than one sufferer surroundings for knowledge exfiltration. The assault finally paves the best way for the Medusa ransomware deployment.
“Organizations working GoAnywhere MFT have successfully been beneath silent assault since no less than September 11, with little readability from Fortra,” watchTowr CEO and Founder, Benjamin Harris, mentioned. “Microsoft’s affirmation now paints a fairly disagreeable image — exploitation, attribution, and a month-long head begin for the attackers.
“What’s nonetheless lacking are the solutions solely Fortra can present. How did risk actors get the non-public keys wanted to use this? Why had been organizations left at nighttime for thus lengthy? Clients deserve transparency, not silence. We hope they may share within the very close to future so affected or doubtlessly affected organizations can perceive their publicity to a vulnerability that’s being actively exploited within the wild.”

The Hacker News Tags:Deploying, Exploit, GoAnywhere, Links, Medusa, Microsoft, Ransomware, Storm1175

Post navigation

Previous Post: CISA Warns of Windows Privilege Escalation Vulnerability Exploited in Attacks
Next Post: Critical Vulnerability Puts 60,000 Redis Servers at Risk of Exploitation

Related Posts

North Korean Hackers Launch PolinRider Campaign North Korean Hackers Launch PolinRider Campaign The Hacker News
Why Offensive Security Training Benefits Your Entire Security Team Why Offensive Security Training Benefits Your Entire Security Team The Hacker News
Lazarus Exploits Windows Flaw to Deploy New Backdoor Lazarus Exploits Windows Flaw to Deploy New Backdoor The Hacker News
Massive 7.3 Tbps DDoS Attack Delivers 37.4 TB in 45 Seconds, Targeting Hosting Provider Massive 7.3 Tbps DDoS Attack Delivers 37.4 TB in 45 Seconds, Targeting Hosting Provider The Hacker News
REVSTEALER Modules Disable Security to Run Crypto Miner REVSTEALER Modules Disable Security to Run Crypto Miner The Hacker News
How to Address the Expanding Security Risk How to Address the Expanding Security Risk The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • 2026’s Leading Audit Management Software Platforms
  • Exploited Flaws in Openwave and Cisco BroadWorks Uncovered
  • Microsoft Releases Patches for Over 1,200 Security Flaws
  • Top Security Policy Management Tools for 2026
  • Exploited Barracuda Flaws Demand Urgent Security Updates

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • 2026’s Leading Audit Management Software Platforms
  • Exploited Flaws in Openwave and Cisco BroadWorks Uncovered
  • Microsoft Releases Patches for Over 1,200 Security Flaws
  • Top Security Policy Management Tools for 2026
  • Exploited Barracuda Flaws Demand Urgent Security Updates

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark