Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Citrix Faces Critical NetScaler RCE Vulnerabilities

Citrix Faces Critical NetScaler RCE Vulnerabilities

Posted on September 27, 2026 By CWS

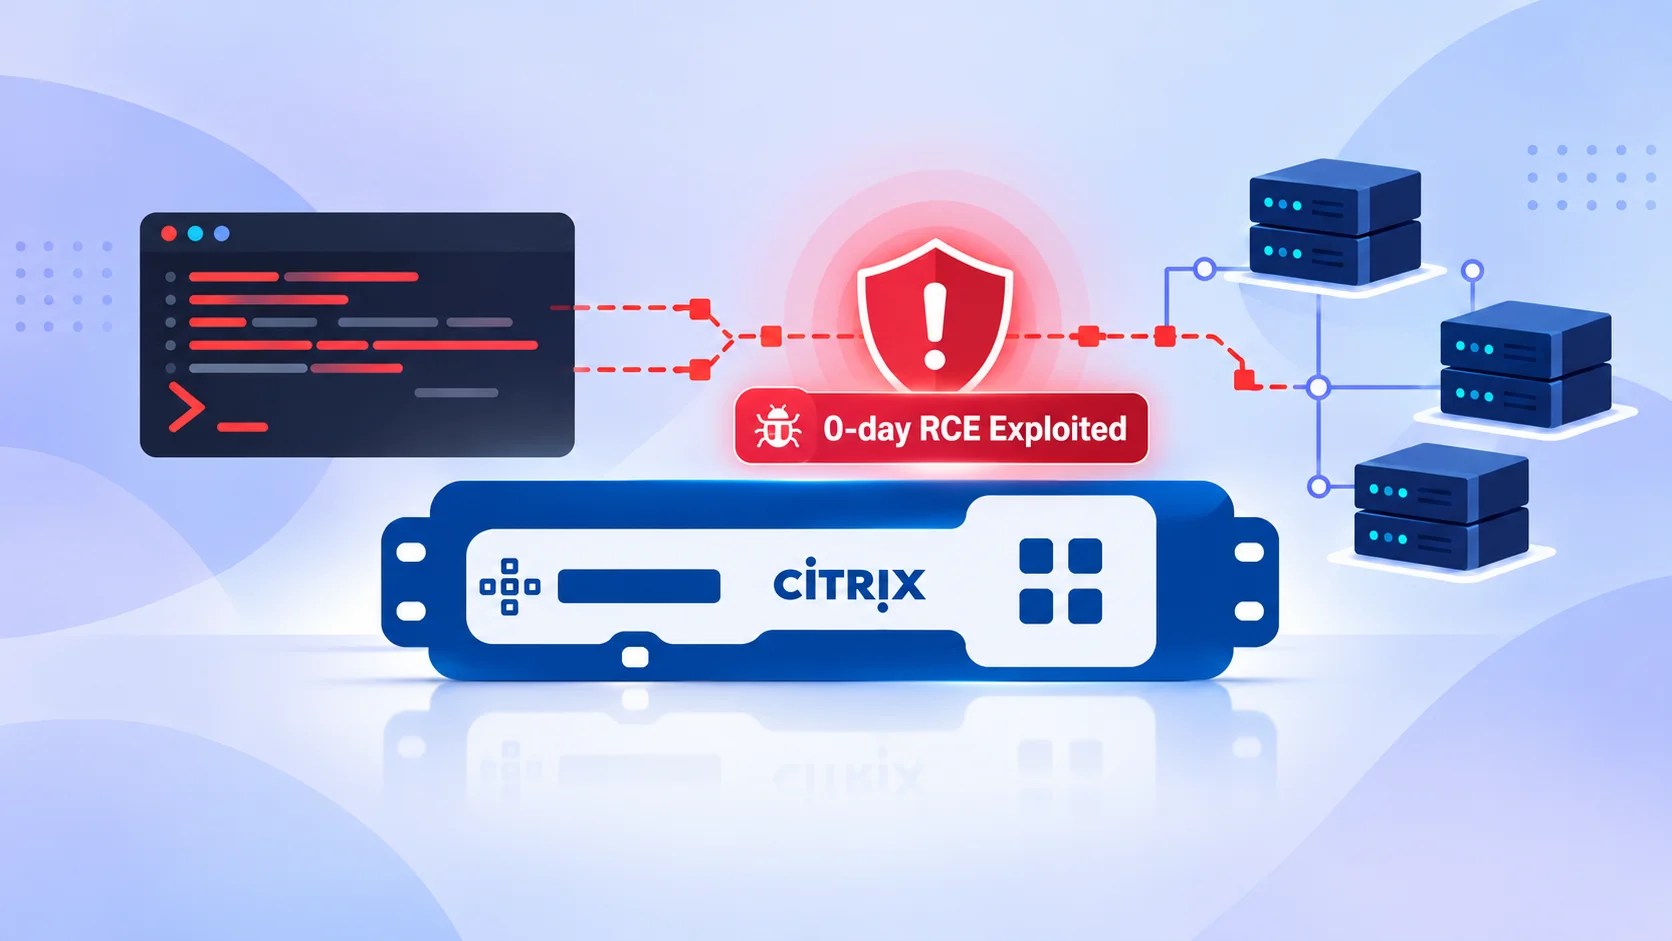
Citrix NetScaler users are currently grappling with reports of two remote code execution (RCE) vulnerabilities that are being actively exploited in attacks. These vulnerabilities, described as zero-day flaws, have yet to be patched, causing significant concern among cybersecurity experts.

Unpatched Vulnerabilities Raise Concerns

According to watchTowr, these vulnerabilities were discovered during forensic investigations and are yet to receive official communication or fixes from Citrix. As of now, Citrix has not provided technical specifics, CVE identifiers, or details regarding the affected builds, leaving security teams with limited information to act upon.

Initial warnings suggested multiple unpatched RCE vulnerabilities were in circulation. watchTowr confirmed that two distinct vulnerabilities could allow remote code execution, although the specifics of exploitation paths and prerequisites remain undisclosed. This lack of detailed information has made independent verification challenging.

Impact on Organizations

In response to these reports, some organizations have opted to shut down internet-exposed NetScaler appliances. While this move can disrupt critical services like VPN access and application delivery, it is seen as a necessary precaution for sensitive environments where patching is not immediately possible.

The current alert should not be confused with Citrix’s previous advisory issued on August 19, which addressed two other vulnerabilities. These earlier vulnerabilities, CVE-2026-19490 and CVE-2026-19489, had their own set of implications and required specific action from administrators.

Advice for Security Teams

Until Citrix provides more information on the new RCE vulnerabilities, security teams are advised to assess all NetScaler instances, confirm their builds, and restrict management access. It’s crucial to implement compensating controls to safeguard public interfaces.

Organizations should preserve logs, review authentication events, and monitor for any unusual activity. In cases where the risk cannot be managed, isolating affected devices may be necessary. Keeping abreast of updates from Citrix’s security bulletin channel is also recommended.

This situation underscores the need for rapid asset discovery and emergency patching protocols for internet-facing infrastructure. Organizations must be prepared to act swiftly, even before full technical disclosures are available, to protect their systems against potential threats.

Cyber Security News Tags:Citrix, CVE, Cybersecurity, forensic investigation, IT infrastructure, NetScaler, network security, patch management, RCE vulnerabilities, remote code execution, security alerts, system protection, zero-day

Post navigation

Previous Post: F-Droid 2.0 Debuts with Major Redesign for App Discovery

Related Posts

Malicious AI Extension Hijacks Search Data Malicious AI Extension Hijacks Search Data Cyber Security News
Mitigating Malware Threats on Unmanaged Endpoint Devices Mitigating Malware Threats on Unmanaged Endpoint Devices Cyber Security News
AI Model Identifies Significant Firefox Vulnerabilities AI Model Identifies Significant Firefox Vulnerabilities Cyber Security News
131 Malicious Extensions Targeting WhatsApp Used Found in Chrome Web Store 131 Malicious Extensions Targeting WhatsApp Used Found in Chrome Web Store Cyber Security News
Cisco IOS and XE Vulnerability Let Remote Attacker Bypass Authentication and Access Sensitive Data Cisco IOS and XE Vulnerability Let Remote Attacker Bypass Authentication and Access Sensitive Data Cyber Security News
New Android Spyware Platform Enables Rebranding and Resale New Android Spyware Platform Enables Rebranding and Resale Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark