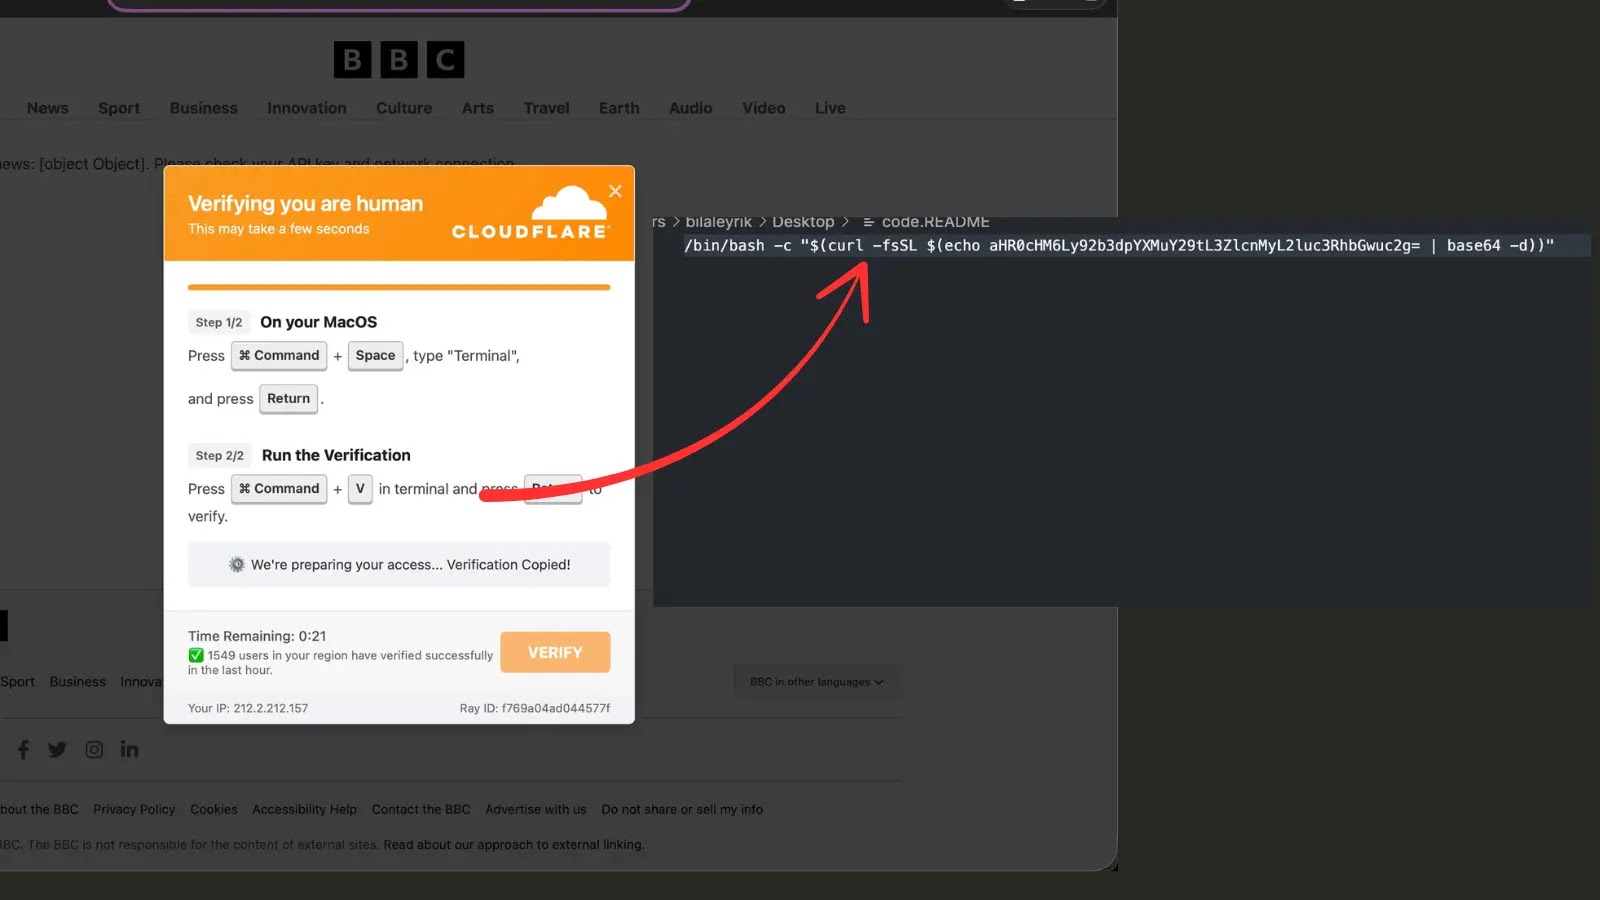
The WARMCOOKIE backdoor first surfaced in mid-2024, delivered primarily through recruiting-themed phishing campaigns that coaxed victims into executing malicious paperwork.
Initially designed as a light-weight implant for distant command execution, its modular codebase enabled speedy adaptation to new goals.
Over the previous yr, targets have included enterprise networks throughout a number of areas, with operators exploiting malvertising and spam campaigns to seed infections.
These intrusions have allowed risk actors to take care of persistent footholds, steal credentials, and deploy secondary payloads.
Elastic Safety Labs analysts recognized ongoing updates to WARMCOOKIE’s infrastructure and code household shortly after the preliminary disclosure.
By mid-2025, the backdoor was implicated in Europol’s Operation Endgame, but infections persevered by way of revamped supply mechanisms.
Whereas earlier variants relied on hardcoded folder paths and static mutex names, current builds leverage dynamic string banks and twin GUID-style mutexes for improved stealth.
Past easy command handlers, the malware now incorporates new capabilities to launch executables, DLLs, and PowerShell scripts on demand.
Every command kind is routed by way of a unified operate that writes the payload into a short lived listing earlier than execution, both by invoking rundll32.exe for DLLs or PowerShell.exe for scripts.
This growth broadens WARMCOOKIE’s utility as a versatile loader, accommodating customized modules with out altering the core binary.
An infection Mechanism
WARMCOOKIE’s an infection mechanism has developed to evade static detection and complicate incident response.
Upon execution, the backdoor parses a configuration blob embedded inside its useful resource part, decrypting fields such because the Distant Command and Management (C2) URL, RC4 key, and a marketing campaign identifier.
The decryption routine resembles the next pseudocode:-
DWORD seed = GetTickCount();
srand(seed);
int index = rand() % STRING_BANK_SIZE;
char *path = string_bank[index];
desStringDecrypt(dword14001B620, buffer, bufferSize);
This snippet illustrates how WARMCOOKIE seeds its random quantity generator with the system uptime, selects a legitimate-looking folder title from a dynamic listing, and decrypts marketing campaign parameters at runtime.
The marketing campaign ID discipline, launched in later variations, allows operators to tag infections with distribution context—equivalent to “traffic2”—facilitating granular monitoring of sufferer units.
After decryption, the malware establishes persistence by making a scheduled activity whose title and executable path mirror acknowledged software program distributors drawn from the identical string financial institution.
This exhibits a pattern scheduled activity entry the place the duty title and folder path reference a reputable IT providers firm title.
Scheduled activity utilizing string financial institution (Supply – Elastic)
By randomizing folder names and activity identifiers, WARMCOOKIE avoids repeating recognized artifacts throughout samples, complicating signature-based detection.
In parallel, twin GUID-style mutexes regulate initialization sequences, guaranteeing solely a single occasion runs and mitigating race circumstances throughout startup.
Collectively, these enhancements underscore the attackers’ emphasis on resilience and evasion, reinforcing WARMCOOKIE’s place as a persistent risk to enterprise environments.
Comply with us on Google Information, LinkedIn, and X to Get Extra Prompt Updates, Set CSN as a Most well-liked Supply in Google.