Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Phishing Campaign Uses Maduro Arrest Story to Deliver Backdoor Payloads

Phishing Campaign Uses Maduro Arrest Story to Deliver Backdoor Payloads

Posted on January 10, 2026January 10, 2026 By CWS

Cybercriminals are leveraging the latest arrest of Venezuelan President Nicolás Maduro to distribute subtle backdoor malware.

The risk actors exploited information surrounding Maduro’s arrest on January 3, 2025, demonstrating how geopolitical occasions proceed to function efficient lures for malicious campaigns.

The assault doubtless begins with a spear-phishing e mail containing a zipper archive named “US now deciding what’s subsequent for Venezuela.zip”.

Inside, victims discover an executable file titled “Maduro to be taken to New York.exe” alongside a malicious dynamic-link library known as “kugou.dll”.

 DLL known as with LoadLibraryW

The executable is a legit KuGou binary, however has been weaponized by way of DLL hijacking to load the malicious library, in response to Darktrace safety researchers.

Malware Conduct

As soon as executed, the malware creates a listing at C:ProgramDataTechnology360NB and copies itself, renaming the information.

 Folder “Technology360NB” created

It establishes persistence by including a registry key at “HKCUSoftwareMicrosoftWindowsCurrentVersionRunLite360” that runs routinely at system startup.

The malware then shows a dialog field prompting customers to restart their laptop, which triggers the malicious payload.

Message field prompting consumer to restart

After the system restarts, the malware initiates common encrypted connections to a command-and-control server at 172.81.60[.]97 on port 443.

These periodic connections allow the malware to obtain directions and configurations from the attackers.

The marketing campaign shares similarities with earlier operations by Mustang Panda, a Chinese language risk group identified for exploiting present occasions such because the Ukraine battle, Tibet-related conventions, and Taiwan-related matters.

Nonetheless, researchers observe that there’s inadequate proof to attribute this exercise to any particular group definitively.

This incident highlights the continued risk of geopolitical-themed phishing campaigns.

Organizations and people ought to train excessive warning when opening e mail attachments, particularly these referencing breaking information or world occasions.

Indicators of Compromise (IoCs)

172.81.60[.]97

8f81ce8ca6cdbc7d7eb10f4da5f470c6 – US now deciding what’s subsequent for Venezuela.zip

722bcd4b14aac3395f8a073050b9a578 – Maduro to be taken to New York.exe

aea6f6edbbbb0ab0f22568dcb503d731  – kugou.dll

Comply with us on Google Information, LinkedIn, and X to Get Extra Prompt Updates, Set CSN as a Most well-liked Supply in Google.
Cyber Security News Tags:Arrest, Backdoor, Campaign, Deliver, Maduro, Payloads, Phishing, Story

Post navigation

Previous Post: Hackers Expose All User Records from Popular Dark Web Forum
Next Post: Europol‑Backed Operation Leads to 34 Arrests in Black Axe Crime Network Bust

Related Posts

DarkSpectre Hackers Infected 8.8 Million Chrome, Edge, and Firefox Users with Malware DarkSpectre Hackers Infected 8.8 Million Chrome, Edge, and Firefox Users with Malware Cyber Security News
StegaBin Campaign Exploits npm with Credential Stealer StegaBin Campaign Exploits npm with Credential Stealer Cyber Security News
OpenSSL Vulnerabilities Let Attackers Execute Malicious Code and Recover Private Key Remotely OpenSSL Vulnerabilities Let Attackers Execute Malicious Code and Recover Private Key Remotely Cyber Security News
CSS Vulnerability Turns Emails into Keyloggers CSS Vulnerability Turns Emails into Keyloggers Cyber Security News
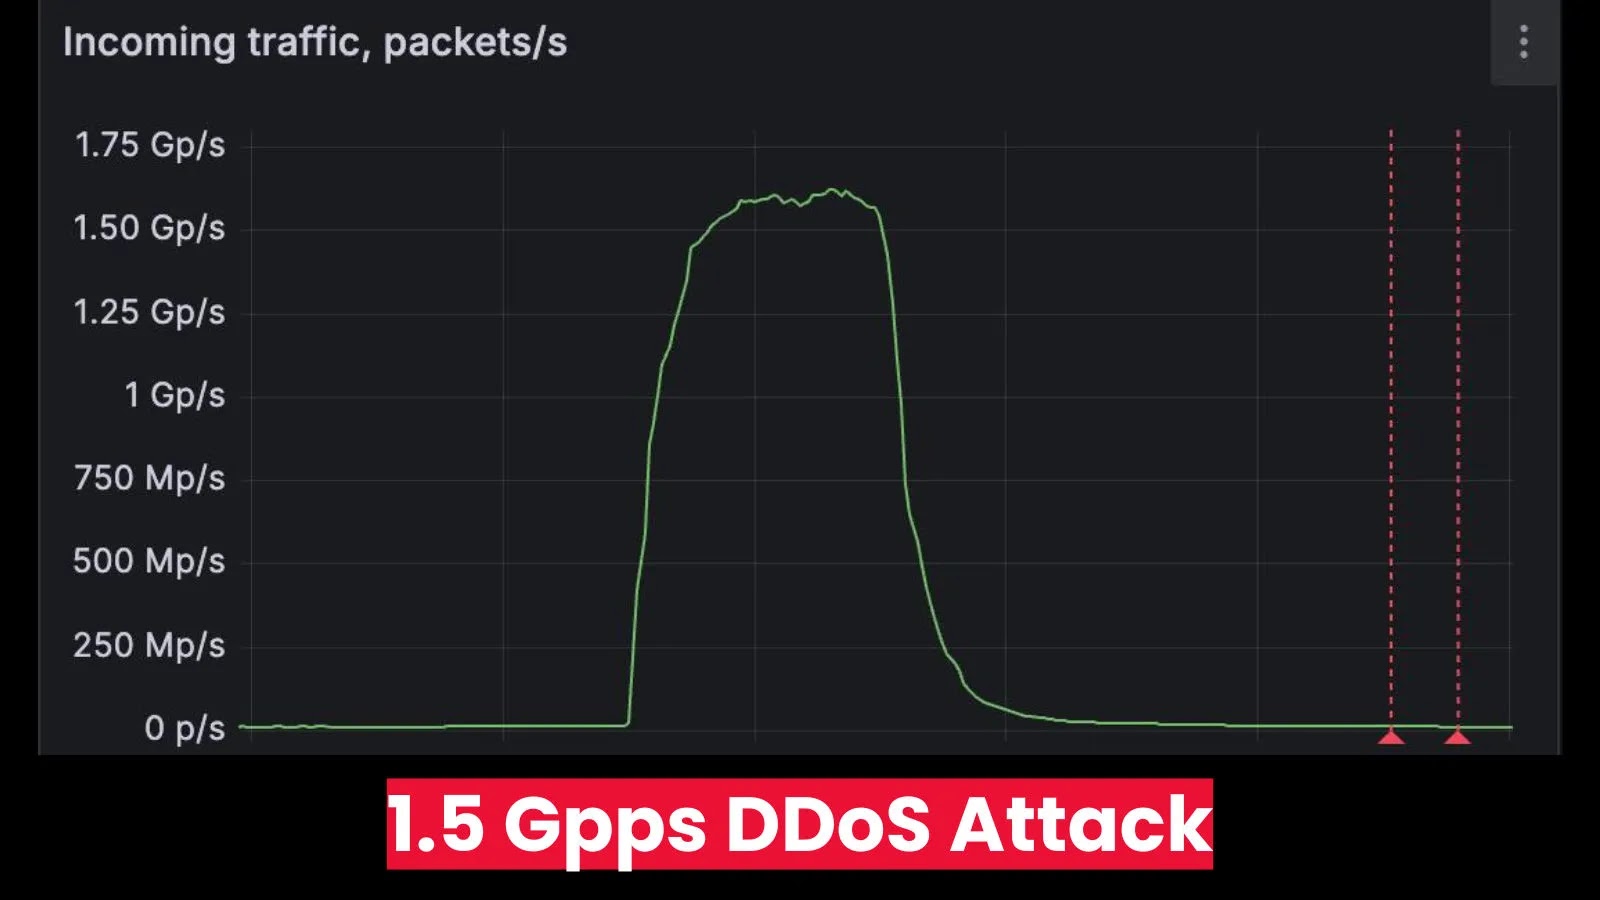
DDoS Mitigation Provider targeted In 1.5 Gpps 1.5 Billion Packets per Second DDoS Attack DDoS Mitigation Provider targeted In 1.5 Gpps 1.5 Billion Packets per Second DDoS Attack Cyber Security News
Cisco AnyConnect VPN Server Vulnerability Let Attackers Trigger DoS Attack Cisco AnyConnect VPN Server Vulnerability Let Attackers Trigger DoS Attack Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hackers Exploit Outlook Flaw to Steal Authentication Data
  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM
  • CISA Alerts on Exploited Vulnerabilities in Key Software

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hackers Exploit Outlook Flaw to Steal Authentication Data
  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM
  • CISA Alerts on Exploited Vulnerabilities in Key Software

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark