Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Exploit Outlook Flaw to Steal Authentication Data

Hackers Exploit Outlook Flaw to Steal Authentication Data

Posted on November 11, 2026 By CWS

Microsoft has announced that a zero-day vulnerability in Outlook is currently being exploited by hackers to steal Windows authentication data when users open malicious files. This vulnerability, identified as CVE-2026-124194, was patched on November 10, 2026. It was not publicly known before the update was released, and Microsoft has categorized it as ‘Exploitation Detected’.

Details of the CVE-2026-124194 Vulnerability

The flaw, which has a CVSS score of 6.5 and is rated as moderately severe, has become a priority for patching due to confirmed exploitation. According to Microsoft’s Exploitability Index, the ‘Exploitation Detected’ status indicates that the company is aware of real-world exploitation, not merely theoretical attacks.

Hackers can exploit this vulnerability without needing an account or prior access to the user’s system. By sending a specially crafted message file, they can trick recipients into opening it with a vulnerable version of Outlook. Successful exploitation requires user interaction and network connectivity, potentially exposing the user’s NTLMv2 hash and allowing attackers to impersonate them.

Impact and Mitigation Strategies

Microsoft clarifies that the Preview Pane does not serve as an attack vector, distinguishing this flaw from other known vulnerabilities. This vulnerability doesn’t directly execute malicious code but poses significant risks of authentication-data theft. The flaw impacts confidentiality, allowing attackers to misuse the user’s authentication data depending on the receiving service’s security measures.

Past incidents, such as those involving compromised Ubiquiti routers, highlight how attackers have used similar vulnerabilities to steal credentials. While these examples suggest potential attack methods, they do not directly link to the current exploitation of the Outlook flaw.

Versions and Security Updates

The affected products include Microsoft 365 Apps for Enterprise and Office LTSC 2021 and 2024 editions. Microsoft has released fixed builds 16.0.14334.21048 for LTSC 2021 and 16.0.17932.21140 for LTSC 2024. Administrators are advised to apply the necessary Office security updates immediately.

To bolster security, Microsoft also suggests blocking unnecessary outbound SMB traffic on TCP port 445 to the internet to curb external SMB exposure. However, this measure should complement rather than replace the installation of the Outlook security fix.

Organizations are encouraged to stay vigilant and integrate threat intelligence into their operations to mitigate the risk of exploitation. Prompt updates and informed security practices are crucial in safeguarding systems against such vulnerabilities.

Cyber Security News Tags:Authentication, CVE-2026-124194, Cybersecurity, Hackers, Microsoft, network security, NTLMv2, Outlook, Patch, Security, SMB, Vulnerability, zero-day

Post navigation

Previous Post: Identity Manager 10.0 LTS Enhances User Experience with AI

Related Posts

Microsoft Edge’s Password Storage Vulnerability Revealed Microsoft Edge’s Password Storage Vulnerability Revealed Cyber Security News
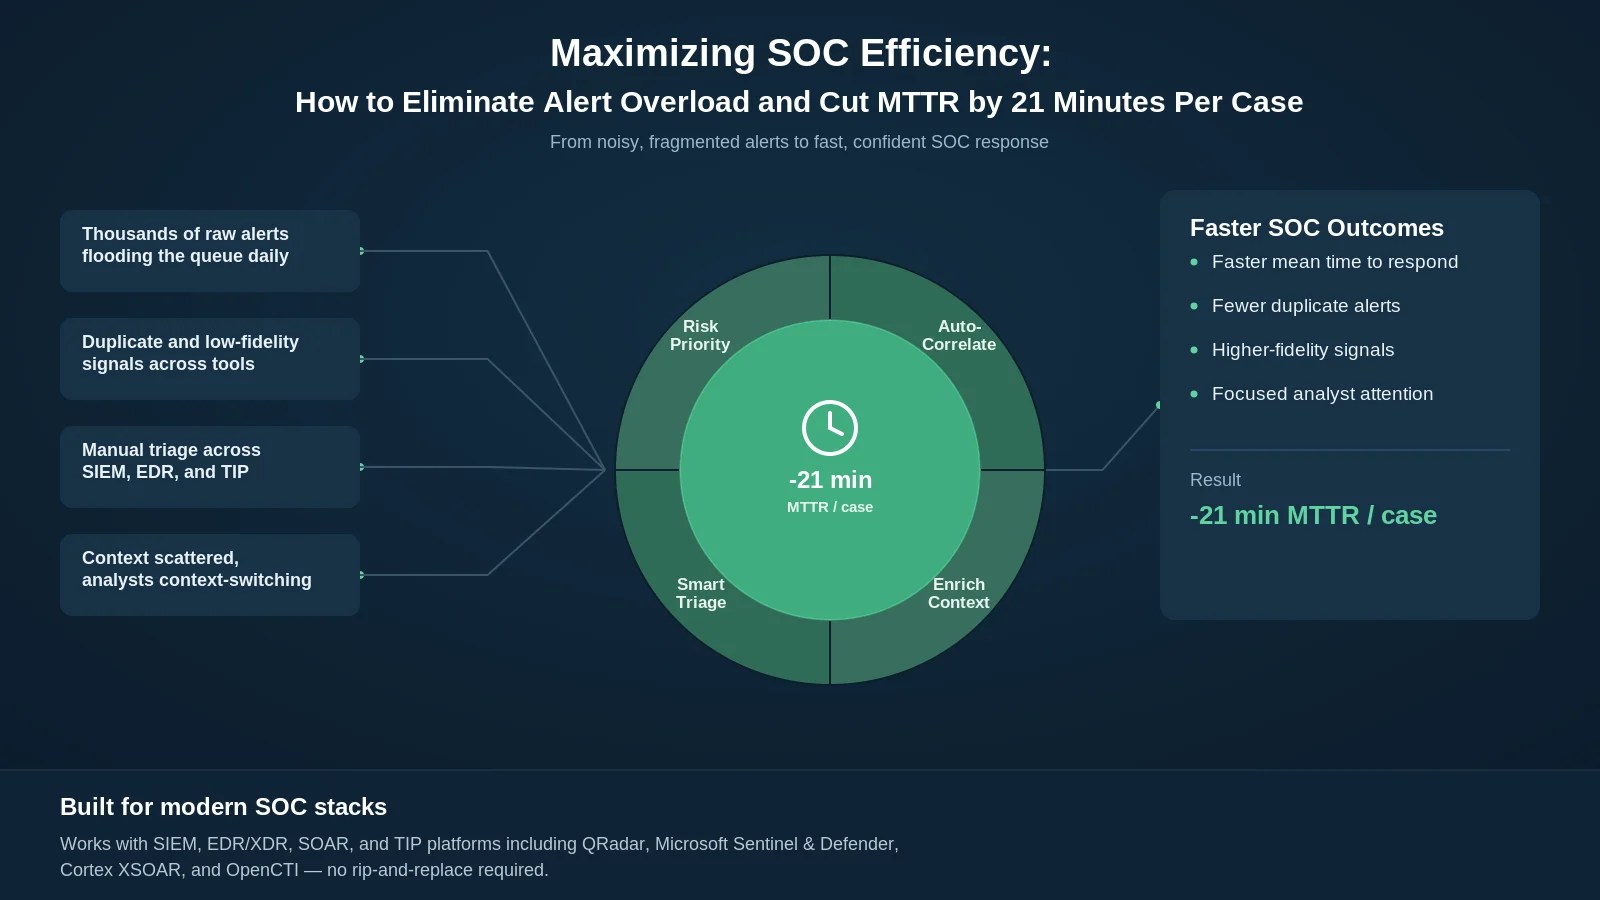
Enhancing SOC Efficiency: Cut Alert Overload & MTTR Enhancing SOC Efficiency: Cut Alert Overload & MTTR Cyber Security News
Critical XSS Flaw in Angular i18n Risks Malicious Attacks Critical XSS Flaw in Angular i18n Risks Malicious Attacks Cyber Security News
Ivanti DSM Vulnerability: Critical Security Update Released Ivanti DSM Vulnerability: Critical Security Update Released Cyber Security News
28,000 Microsoft Exchange Servers Vulnerable to CVE-2025-53786 Exposed Online 28,000 Microsoft Exchange Servers Vulnerable to CVE-2025-53786 Exposed Online Cyber Security News
Hackers Exploit Fake CAPTCHA for Corporate Network Breaches Hackers Exploit Fake CAPTCHA for Corporate Network Breaches Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hackers Exploit Outlook Flaw to Steal Authentication Data
  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM
  • CISA Alerts on Exploited Vulnerabilities in Key Software

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hackers Exploit Outlook Flaw to Steal Authentication Data
  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM
  • CISA Alerts on Exploited Vulnerabilities in Key Software

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark