Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical OpenSSH Vulnerability Exposes Moxa Ethernet Switches to Remote Code Execution

Critical OpenSSH Vulnerability Exposes Moxa Ethernet Switches to Remote Code Execution

Posted on January 13, 2026January 13, 2026 By CWS

Moxa has issued a important safety advisory relating to CVE-2023-38408, a extreme vulnerability in OpenSSH affecting a number of Ethernet change fashions.

The flaw, with a CVSS 3.1 rating of 9.8, permits unauthenticated distant attackers to execute arbitrary code on weak gadgets with out requiring person interplay.

CVE-2023-38408 stems from an unreliable search path within the PKCS#11 characteristic of OpenSSH’s ssh-agent earlier than 9.3p2.

CVE IDSeverityCVSSVulnerabilityImpactCVE-2023-38408Critical9.8SSH agent forwarding flawRemote code execution

The vulnerability (CWE-428) is classed as an unquoted search path concern, enabling distant code execution when an SSH agent is forwarded to an attacker-controlled system.

This safety flaw represents an incomplete repair for the sooner CVE-2016-10009 vulnerability.

Attackers can exploit this weak spot to realize full system compromise, together with breaches of confidentiality, integrity, and availability.

Affected Merchandise

This vulnerability impacts a number of Moxa change sequence.

Product SeriesModelsVulnerable / Affected Firmware VersionsAction RequiredEDS SeriesEDS-G4000, EDS-4008, EDS-4009, EDS-4012, EDS-4014, EDS-G4008, EDS-G4012, EDS-G4014Firmware v4.1 or earlierUpgrade firmwareRKS SeriesRKS-G4000, RKS-G4028, RKS-G4028-L3Firmware v5.0 or earlierImmediate consideration/patch required

Moxa recommends customers instantly contact Moxa Technical Help to acquire the newest safety patches.

Organizations utilizing affected EDS-series gadgets ought to improve to firmware model 4.1.58, whereas RKS-series customers ought to improve to model 5.0.4.

Till patches may be deployed, Moxa advises implementing restrictive community entry controls, similar to firewalls and ACLs, to restrict communication to trusted networks solely.

Organizations ought to segregate operational networks from enterprise networks utilizing VLANs or bodily separation, flip off pointless community companies, and keep away from exposing gadgets on to the Web.

Implementing multi-factor authentication, role-based entry management, and steady community site visitors monitoring for anomalous exercise provides a further layer of safety.

Common vulnerability assessments and firmware replace schedules are important elements of a complete protection technique.

Comply with us on Google Information, LinkedIn, and X for every day cybersecurity updates. Contact us to characteristic your tales.
Cyber Security News Tags:Code, Critical, Ethernet, Execution, Exposes, Moxa, OpenSSH, Remote, Switches, Vulnerability

Post navigation

Previous Post: Android Banking Malware deVixor Actively Targeting Users with Ransomware Capabilities
Next Post: Anthropic Unveils “Claude for Healthcare” to Help Users Understand Medical Records

Related Posts

Adobe ColdFusion Flaws Allow Code Execution Attacks Adobe ColdFusion Flaws Allow Code Execution Attacks Cyber Security News
Namastex npm Packages Compromised with CanisterWorm Malware Namastex npm Packages Compromised with CanisterWorm Malware Cyber Security News
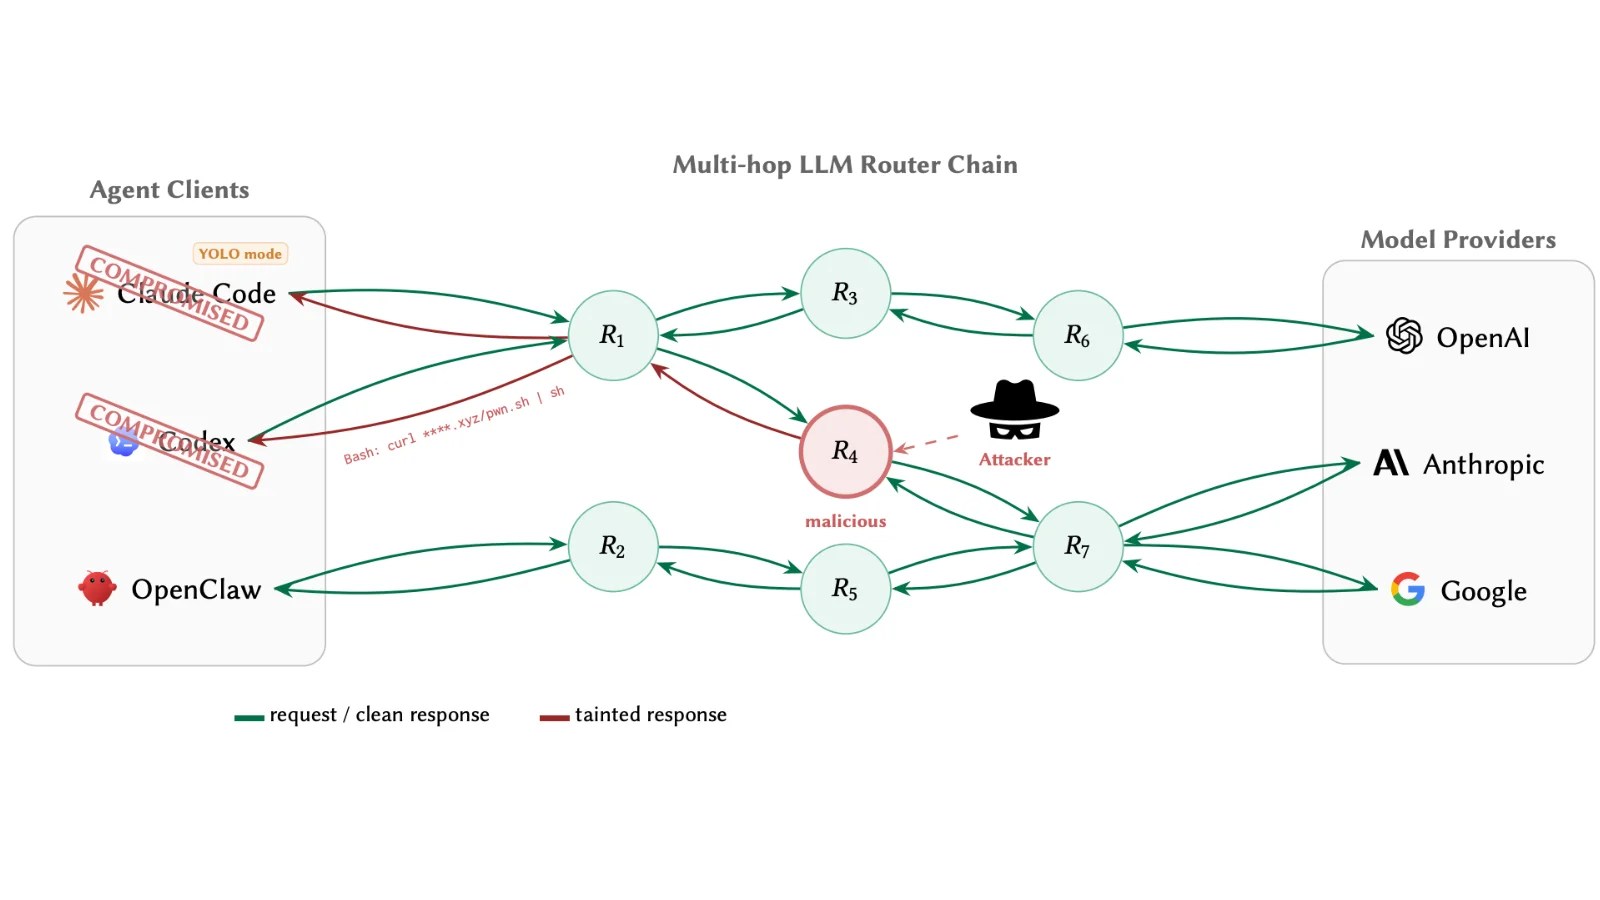
AI API Routers: Security Risks and Data Theft Concerns AI API Routers: Security Risks and Data Theft Concerns Cyber Security News
Fake Google Meet Pages Targeting User Credentials Fake Google Meet Pages Targeting User Credentials Cyber Security News
New Windows Notepad and Paint Update Brings More Useful AI Features New Windows Notepad and Paint Update Brings More Useful AI Features Cyber Security News
Wireshark 4.6.4 Update Enhances Security and Stability Wireshark 4.6.4 Update Enhances Security and Stability Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity
  • SGLang Exploit Breach Exposes NEAR AI User Data
  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity
  • SGLang Exploit Breach Exposes NEAR AI User Data
  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark