Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft’s Plan to Phase Out NTLM for Enhanced Security

Microsoft’s Plan to Phase Out NTLM for Enhanced Security

Posted on February 3, 2026 By CWS

Key Points

  • Microsoft is planning to gradually disable NTLM authentication.
  • A phased roadmap will guide the transition to more secure protocols.
  • Organizations are encouraged to adopt Kerberos and prepare for changes.

Microsoft’s Transition from NTLM Authentication

In a significant move towards enhancing authentication security, Microsoft has announced its intention to phase out the NTLM (New Technology LAN Manager) protocol. This legacy system has been a staple in Windows environments for over 30 years but is now being replaced by more secure alternatives.

The decision to disable NTLM by default in future Windows releases is part of a larger strategy to bolster security against contemporary threats. This change comes as NTLM’s weaknesses expose systems to various attack vectors, such as replay and pass-the-hash attacks.

Three-Phase Roadmap for Transition

Microsoft’s roadmap to eliminate NTLM involves a carefully structured three-phase plan to minimize disruptions. The first phase, which is already available, focuses on visibility and auditing, allowing organizations to identify where NTLM is used in their systems.

The second phase, expected to roll out in the latter half of 2026, aims to reduce NTLM usage by enabling Kerberos as a fallback. Finally, a future Windows release will disable NTLM by default, although legacy support will remain for specific scenarios.

To assist organizations during this transition, Microsoft will maintain backward compatibility. NTLM can still be re-enabled through policy adjustments, ensuring that businesses with legacy systems can adapt without major interruptions.

Preparing for a Secure Future

As Microsoft moves towards a passwordless future, enterprises are advised to start preparing now. This includes deploying enhanced NTLM auditing, mapping application dependencies, and migrating systems to Kerberos. Testing configurations in non-production environments is also recommended to ensure seamless transitions.

Businesses facing unique challenges with NTLM dependencies are encouraged to reach out to Microsoft through their dedicated support channel at ntlm@microsoft[.]com. This collaborative approach aims to support organizations in navigating these changes effectively.

Conclusion

Microsoft’s phased approach to phasing out NTLM underscores the company’s commitment to strengthening security protocols. By transitioning to Kerberos and other robust authentication systems, organizations can protect against evolving cyber threats while maintaining operational continuity.
Cyber Security News Tags:Authentication, Cybersecurity, digital transformation, enterprise security, IT management, Kerberos, legacy systems, Microsoft, network security, NTLM, password security, security protocols, Windows security

Post navigation

Previous Post: Growing Infostealer Threat Targets macOS Using Python
Next Post: Hackers Target React Server Components for Cyber Attacks

Related Posts

Apache Tomcat Coyote Vulnerability Let Attackers Trigger DoS Attack Apache Tomcat Coyote Vulnerability Let Attackers Trigger DoS Attack Cyber Security News
NCSC Warns of Oracle E-Business Suite 0-Day Vulnerability Actively Exploited in Attacks NCSC Warns of Oracle E-Business Suite 0-Day Vulnerability Actively Exploited in Attacks Cyber Security News
Metasploit Module Released For Actively Exploited SharePoint 0-Day Vulnerabilities Metasploit Module Released For Actively Exploited SharePoint 0-Day Vulnerabilities Cyber Security News
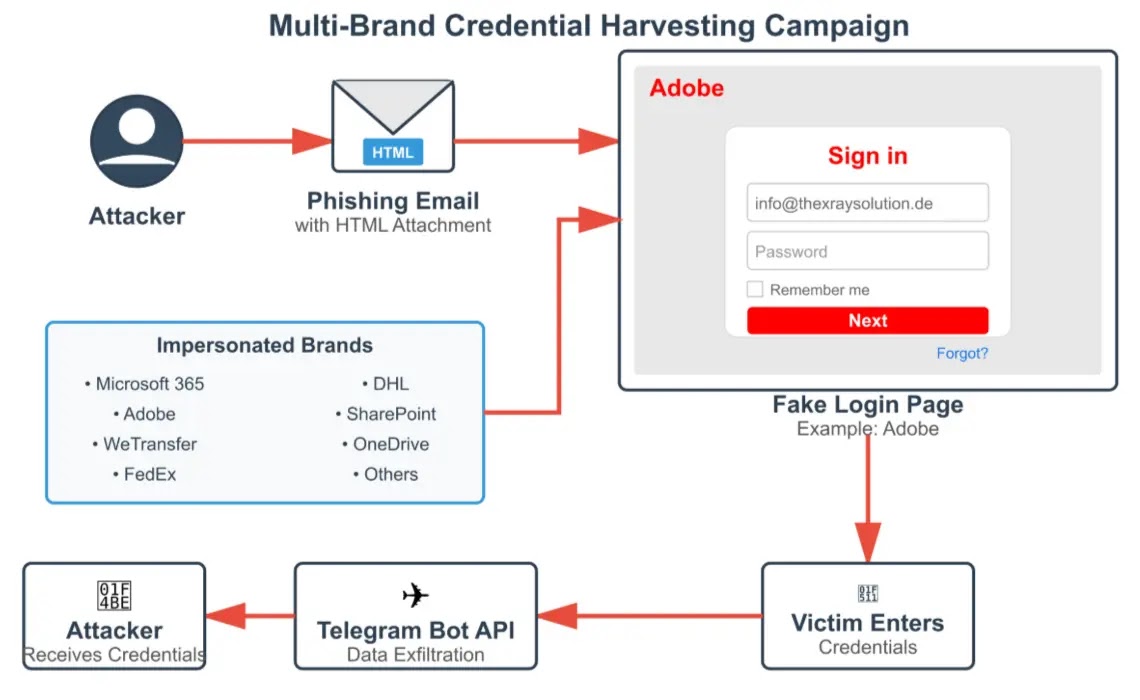
New Phishing Attack Leverages Popular Brands to Harvest Login Credentials New Phishing Attack Leverages Popular Brands to Harvest Login Credentials Cyber Security News
GTFire Phishing Attacks Exploit Google Services for Data Theft GTFire Phishing Attacks Exploit Google Services for Data Theft Cyber Security News
Research Finds 64% of Third-Party Apps Access Sensitive Data Research Finds 64% of Third-Party Apps Access Sensitive Data Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark