Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Windows Shell Vulnerability Threatens User Security

Critical Windows Shell Vulnerability Threatens User Security

Posted on February 11, 2026 By CWS

Microsoft has issued essential updates to address a significant zero-day vulnerability in the Windows Shell, identified as CVE-2026-21510. This security flaw, which is actively being exploited, allows remote attackers to bypass key authentication protocols, posing a risk to millions of Windows users.

Understanding the Security Flaw

The vulnerability is classified under ‘Security Feature Bypass’ and holds a CVSS score of 8.8, indicating its importance. It is related to the manner in which Windows Shell processes specific file types. Typically, Windows employs mechanisms like SmartScreen and user prompts to caution users about potentially hazardous files from the internet, known as the ‘Mark of the Web.’

However, attackers leveraging CVE-2026-21510 can create specially crafted files, such as malicious shortcuts, to circumvent these security checks. Consequently, if a user interacts with such a file, the malicious code can execute without any alerts or prompts, effectively bypassing the user-approval process for untrusted software.

Impact on Windows Products

This vulnerability impacts a wide range of Microsoft products, affecting both recent and older systems. Vulnerable versions include Windows 10 (1607, 1809, 21H2, 22H2), Windows 11 (23H2, 24H2, 25H2, 26H1), and Windows Server editions from 2012 through 2025. Microsoft has verified that this flaw allows unauthorized code to be executed as if it were trusted content.

Given the active exploitation of this zero-day vulnerability, it is crucial for administrators and users to apply the necessary patches without delay. The security updates were released as part of Microsoft’s Patch Tuesday on February 10, 2026.

Immediate Actions for Users

Users are strongly advised to navigate to Settings > Windows Update to install the latest updates. In addition, caution should be exercised when dealing with links or shortcut files from unfamiliar sources until the updates are implemented. This proactive approach is necessary to mitigate potential security breaches.

This vulnerability was identified by researchers from the Microsoft Threat Intelligence Center (MSTIC) and the Google Threat Intelligence Group, underscoring the critical nature of this issue and the collaborative effort to address it.

Stay informed on the latest cybersecurity developments by following us on Google News, LinkedIn, and X. For more detailed insights and to share your stories, feel free to contact us.

Cyber Security News Tags:0-day vulnerability, authentication bypass, CVE-2026-21510, Cybersecurity, Google Threat Intelligence, Malware, Microsoft, Microsoft Threat Intelligence, Patch Tuesday, security patch, SmartScreen, Windows Shell, Windows Update

Post navigation

Previous Post: Critical Vulnerabilities Found in Intel’s TDX by Google
Next Post: Fortinet Addresses Critical Security Flaws in Latest Update

Related Posts

Microsoft Domain Faces Trust Issues Due to Expired Certificate Microsoft Domain Faces Trust Issues Due to Expired Certificate Cyber Security News
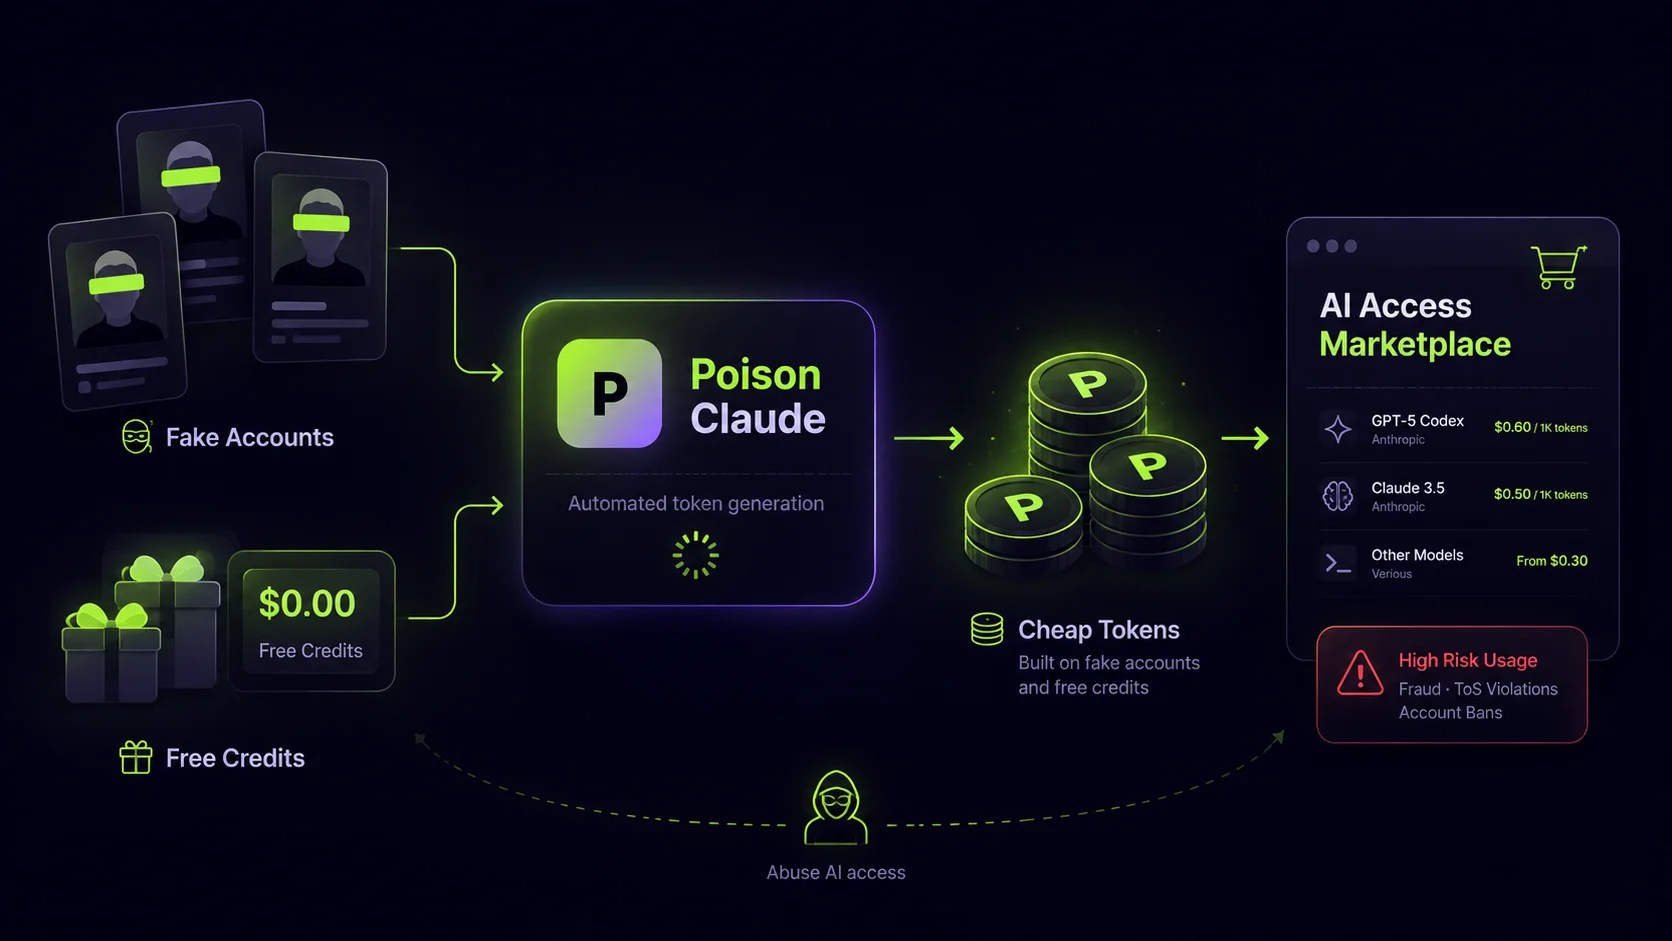
Fraudulent AI Token Sales Exploit Free Cloud Accounts Fraudulent AI Token Sales Exploit Free Cloud Accounts Cyber Security News
New Malware Via WhatsApp Exfiltrate Contacts to Attack Server and Deploys Malware New Malware Via WhatsApp Exfiltrate Contacts to Attack Server and Deploys Malware Cyber Security News
5 Best IT Infrastructure Modernisation Services In 2025 5 Best IT Infrastructure Modernisation Services In 2025 Cyber Security News
Enhancing Nmap Efficiency with nmapUnleashed Enhancing Nmap Efficiency with nmapUnleashed Cyber Security News
New GhostSocks Malware-as-a-Service Enables Threat Actors to Convert Compromised Devices into Proxies New GhostSocks Malware-as-a-Service Enables Threat Actors to Convert Compromised Devices into Proxies Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark