Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Fraudulent AI Token Sales Exploit Free Cloud Accounts

Fraudulent AI Token Sales Exploit Free Cloud Accounts

Posted on August 5, 2026 By CWS

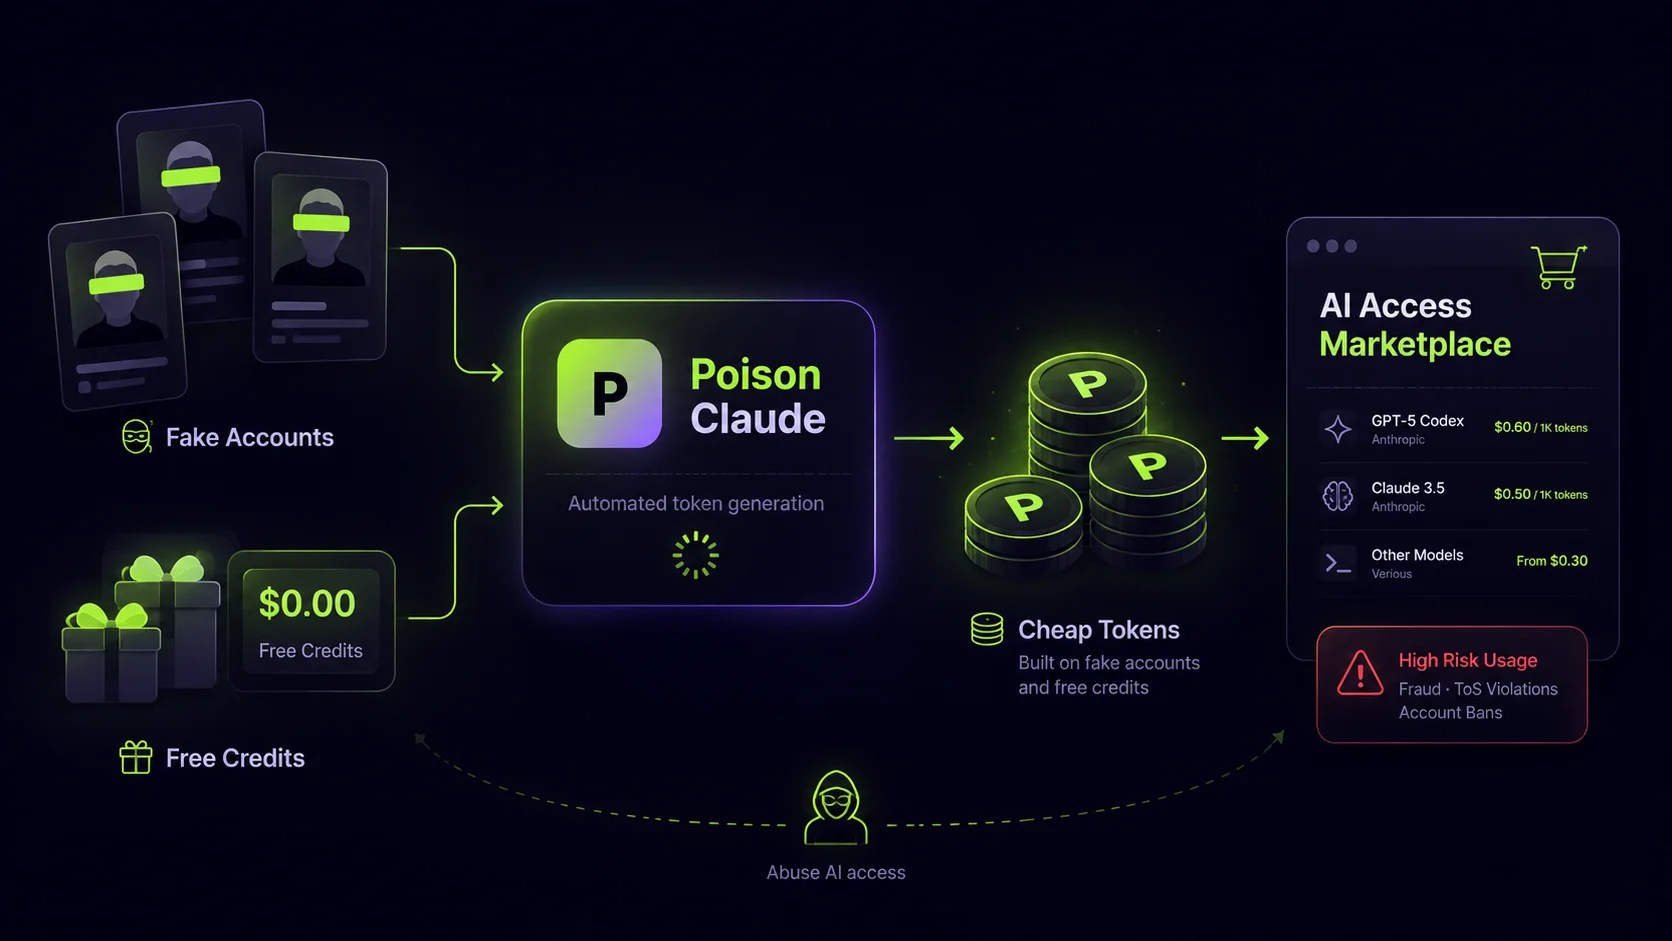
In a concerning development, an elusive online service known as Poison Claude has been reported to offer access to Anthropic’s advanced AI models at significantly reduced prices. Investigations reveal that these discounts are primarily sourced from cloud accounts fraudulently created and stocked with complimentary credits.

The Rise of Gray Market AI Tools

As AI tools become indispensable for various technological tasks such as coding and research, a gray market has surfaced to provide budget-friendly access to these tools. This market particularly caters to users who are either unable to pay for official services or are restricted by regional barriers, including numerous users from China who face governmental limitations on U.S. AI models.

Okta Threat Intelligence has identified that Poison Claude, operated from the domain poison-claude[.]bitsender[.]top, openly markets “unlimited” AI tokens through plans that meter prompts and offer bundled token packages. Their service charges a mere 5 to 15 percent of Anthropic’s standard token rate due to the essentially free operational costs.

Cryptocurrency Payments and Account Fraud

To bypass identity verification, Poison Claude exclusively accepts cryptocurrency payments, including Tether, Bitcoin, and Ethereum. The service facilitates access to AI models such as Opus 4.8 and Sonnet 4.6 by pooling AI provider accounts. These accounts are often established using sign-up incentives like Amazon’s $100 AWS Bedrock credit, and customer requests are channeled through whichever account still has credits available.

Upon payment, users are provided with an API key and instructions to alter their Claude Code environment variables, redirecting them to Poison Claude’s servers instead of Anthropic’s official endpoints.

Implications and Industry Response

An error in configuration highlighted the operation’s scale, revealing 881 total users, with 872 being active at the time. Although the primary domain is safeguarded by Cloudflare’s CDN, a related endpoint was traced to a Hostinger server in Mumbai.

Poison Claude is not isolated in these activities. A similar service, Ecomagent[.]in, offers reduced-rate access to AI models by misusing Google Cloud’s startup credit program. This program can provide substantial credits to AI startups, which are then fraudulently utilized.

Okta Threat Intelligence has observed a broader trend of automated account fraud within the AI industry, tracking over 105,000 fraudulent account creation attempts from various global locations. This is in response to companies like Anthropic implementing stricter identity verification processes, which include government ID checks and selfie verification to curb abuse.

Efforts to counter these fraudulent practices continue as Okta Threat Intelligence informs major cloud providers, including Cloudflare and AWS, about the ongoing abuse, aiming to disrupt the evolving gray market for AI model access.
Cyber Security News Tags:account fraud, AI access restrictions, AI market, AI tokens, Anthropic models, cloud credits, cloud fraud, cryptocurrency payments, Okta Threat Intelligence, Poison Claude

Post navigation

Previous Post: Researchers Uncover $50K Exploit Chain in Samsung Phones
Next Post: Exposed n8n API Tokens Risk Credential Theft

Related Posts

Urgent Update for Notepad++ Fixes Critical Security Flaws Urgent Update for Notepad++ Fixes Critical Security Flaws Cyber Security News
Microsoft Teams Vishing Attack Exploits Quick Assist Microsoft Teams Vishing Attack Exploits Quick Assist Cyber Security News
MacSync Stealer Threatens Mac Users with Password Theft MacSync Stealer Threatens Mac Users with Password Theft Cyber Security News
New Malware Targets MacOS to Steal Cryptocurrency New Malware Targets MacOS to Steal Cryptocurrency Cyber Security News
RainyDay, Turian and Naikon Malwares Abuse DLL Search Order to Execute Malicious Loaders RainyDay, Turian and Naikon Malwares Abuse DLL Search Order to Execute Malicious Loaders Cyber Security News
XWorm Malware Targets Latin American Businesses XWorm Malware Targets Latin American Businesses Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CISA Alerts on Linux Kernel Flaws Under Active Attack
  • TigerByte Cyber Launches with $3M Funding to Enhance Security
  • Identity Visibility: Key to Secure IAM by 2026
  • SolarWinds Fixes Critical ARM Security Flaw
  • Hackers Exploit TanStack to Steal GitHub Repositories

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CISA Alerts on Linux Kernel Flaws Under Active Attack
  • TigerByte Cyber Launches with $3M Funding to Enhance Security
  • Identity Visibility: Key to Secure IAM by 2026
  • SolarWinds Fixes Critical ARM Security Flaw
  • Hackers Exploit TanStack to Steal GitHub Repositories

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark