Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hotel Booking Scam Targets Guests with Fake Payment Requests

Hotel Booking Scam Targets Guests with Fake Payment Requests

Posted on April 1, 2026 By CWS

Travelers worldwide are falling victim to a rapidly spreading scam that manipulates their legitimate hotel bookings to issue fraudulent payment requests. Cybercriminals have devised a strategy to infiltrate established hotel reservation systems, deceiving guests with false pre-payment verifications.

Deceptive Messaging Tactics

The operation typically begins with a seemingly innocuous message on platforms like WhatsApp, purportedly from a hotel’s Guest Relations team. These messages, which include genuine booking details such as the hotel’s name and stay dates, add an air of credibility that many unsuspecting travelers accept as standard procedure.

The effectiveness of this scam lies in its ability to exploit familiar contexts. Unlike traditional phishing schemes, these messages do not rely on sophisticated writing styles or elaborate structures. Instead, they are grounded in authentic booking information, making them appear as legitimate customer service interactions.

Identifying the Scam

Experts Martin Chlumecký and Luis Corrons from Gen Digital have documented this threat, labeling it the ‘Reservation Hijack Scam.’ Their research highlights that the attack is not merely a travel-themed phishing attempt, but a comprehensive exploitation of authentic booking workflows.

The scam has been most prevalent in regions such as the United Kingdom, France, Germany, the United States, Brazil, and Australia. It operates on two fronts: firstly, through fake booking-platform messages guiding victims to fraudulent payment sites, and secondly, through the direct compromise of hotel management software.

Breaching Hotel Systems

The more dangerous aspect of this scam involves breaching hotel software systems like Cloudbeds. By phishing hotel employees for their login credentials, attackers gain access to real reservation data, enabling them to send fraudulent messages that are indistinguishable from genuine communications.

Once inside the system, hackers employ tactics such as the ‘Scam-Yourself Attack,’ where malicious commands are disguised as security updates, installing remote access trojans for ongoing system access. This allows attackers to send professional-looking payment requests, convincing victims to submit financial information through typo-squatted domains.

Precautionary Measures

To protect against this threat, guests are advised to avoid clicking on links requesting payment verification from unfamiliar sources. Instead, they should directly contact hotels via official websites or original booking platforms. If payment details have already been compromised, immediate action is necessary, including contacting banks and monitoring for further fraudulent activities.

For hospitality businesses, enhancing the security of guest communication channels is crucial. Implementing phishing-resistant authentication, restricting access to reservation data, and establishing robust incident response plans are essential measures to prevent credential theft and safeguard guest information.

Smaller establishments, in particular, should prioritize multi-factor authentication to mitigate the risk of staff credential compromises. By doing so, the hospitality industry can better protect its clientele from evolving cyber threats.
Cyber Security News Tags:cyber attack, Cybercrime, Cybersecurity, data breach, fake payment requests, guest safety, hacker tactics, hotel booking, hotel security, online fraud, Phishing, reservation hijack, Scam, travel fraud, travel security

Post navigation

Previous Post: CrystalX Malware-as-a-Service on Telegram Exposed
Next Post: ShinyHunters Allegedly Breaches Cisco Data

Related Posts

CISA Warns of Cisco Firewall 0-Day Vulnerabilities Actively Exploited in the Wild CISA Warns of Cisco Firewall 0-Day Vulnerabilities Actively Exploited in the Wild Cyber Security News
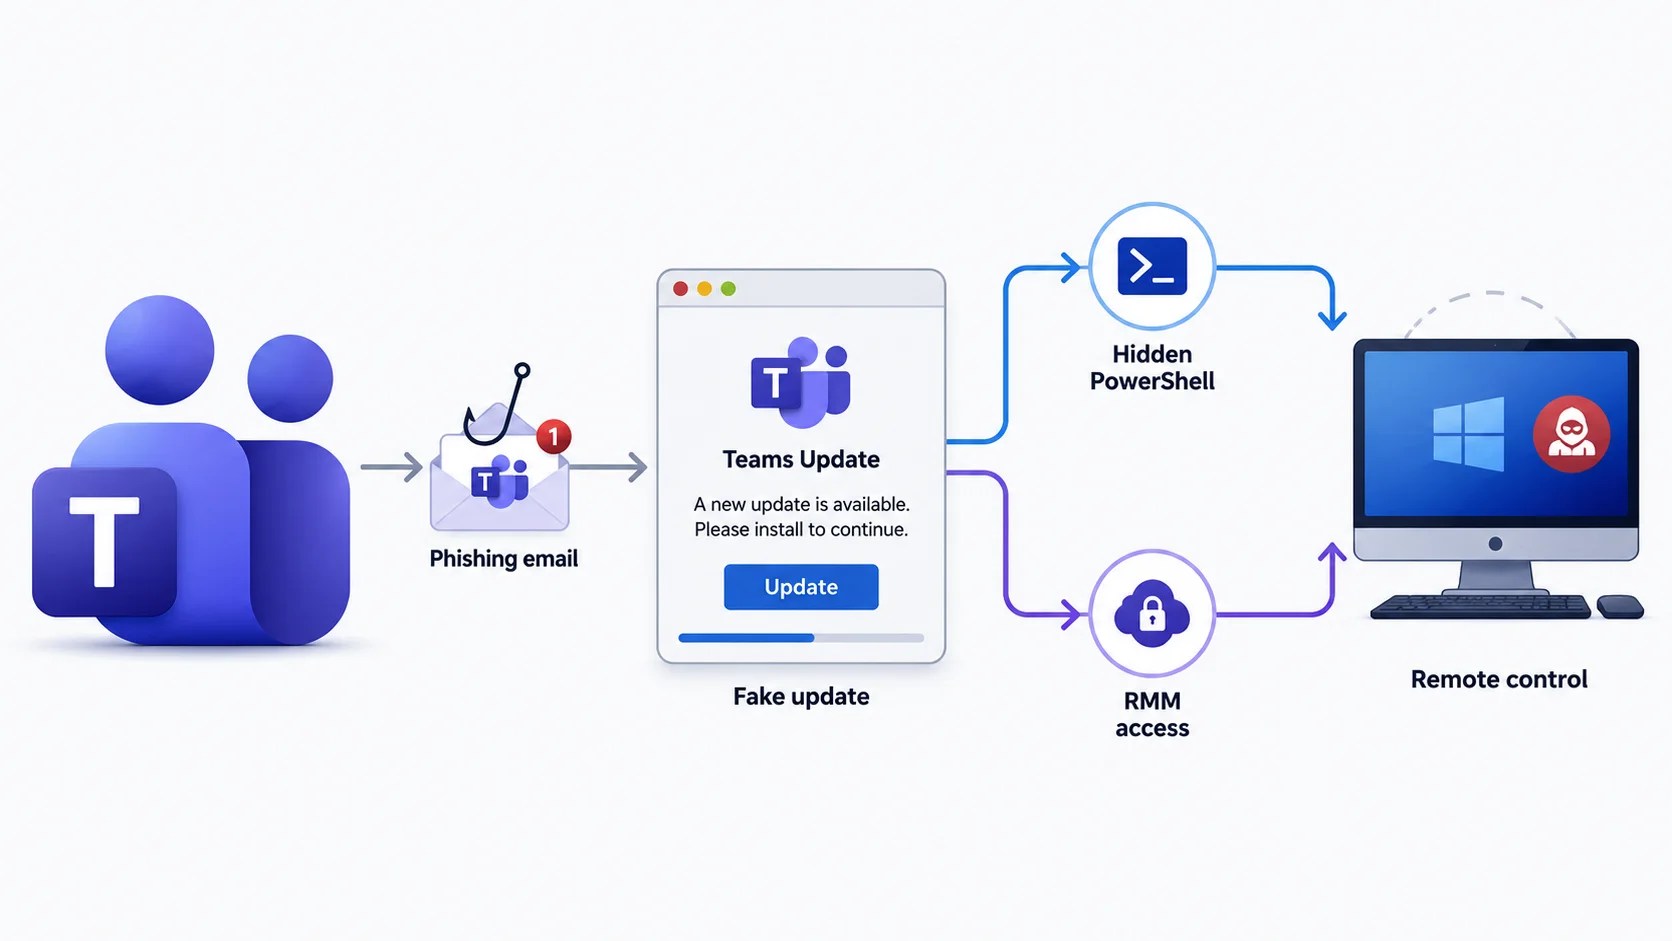
Fake Teams Update Grants Hackers Dual PC Control Fake Teams Update Grants Hackers Dual PC Control Cyber Security News
New Phishing Attack Impersonates as DWP Attacking Users to Steal Credit Card Data New Phishing Attack Impersonates as DWP Attacking Users to Steal Credit Card Data Cyber Security News
ESPHome Web Server Authentication Bypass Vulnerability Exposes Smart Devices ESPHome Web Server Authentication Bypass Vulnerability Exposes Smart Devices Cyber Security News
Mozilla High Severity Vulnerabilities Enables Remote Code Execution Mozilla High Severity Vulnerabilities Enables Remote Code Execution Cyber Security News
AI-Powered Zero-Day Exploits Raise Cybersecurity Concerns AI-Powered Zero-Day Exploits Raise Cybersecurity Concerns Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • TeamViewer Urges Update Due to Critical Security Flaws
  • Armadin Secures $255 Million, Now Valued at $2.5 Billion
  • OpenAI Thwarts AI Model Data Extraction by Moonshot
  • Over 543,000 GitHub Credentials Remain Vulnerable
  • US Treasury Targets ATM Malware Network in Sanctions

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • TeamViewer Urges Update Due to Critical Security Flaws
  • Armadin Secures $255 Million, Now Valued at $2.5 Billion
  • OpenAI Thwarts AI Model Data Extraction by Moonshot
  • Over 543,000 GitHub Credentials Remain Vulnerable
  • US Treasury Targets ATM Malware Network in Sanctions

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark