Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Weaver E-cology Flaw Exploited via Debug API

Critical Weaver E-cology Flaw Exploited via Debug API

Posted on May 5, 2026 By CWS

A significant security flaw in Weaver’s E-cology platform, known for enabling office automation and team collaboration, is currently being actively leveraged by cyber attackers. This vulnerability, identified as CVE-2026-22679 with a CVSS score of 9.8, permits unauthenticated remote code execution in versions of Weaver E-cology 10.0 released before March 12, 2026. The flaw is linked to the “/papi/esearch/data/devops/dubboApi/debug/method” endpoint, which attackers exploit to run arbitrary commands by manipulating debug functionalities.

Understanding the Exploitation

According to the National Vulnerability Database (NVD), attackers can send specially crafted POST requests with tailored interfaceName and methodName parameters to trigger command execution helpers, leading to arbitrary command execution on targeted systems. The Shadowserver Foundation first detected active exploitation on March 31, 2026. Meanwhile, QiAnXin, a security firm in China, confirmed the vulnerability’s exploitability through successful reproduction in their report dated March 17, 2026.

Timeline of the Threat

New insights from the Vega Research Team have uncovered that exploitation of CVE-2026-22679 was underway as early as March 17, 2026, shortly after patches were issued. The attack sequence involved a week of intensive operator activities, including verification of remote code execution, multiple failed attempts to drop payloads, an unsuccessful transition to an MSI implant, and attempts to retrieve PowerShell scripts from attacker-controlled servers. Security expert Daniel Messing outlined these activities in a recent analysis.

Indicators of Compromise and Mitigation

The malicious campaign involved using an MSI installer named “fanwei0324.msi,” suggesting an attempt to disguise the payload using a romanized version of Weaver’s name. The threat actor was also seen executing system discovery commands like whoami, ipconfig, and tasklist to gather information. To aid in detection, security researcher Kerem Oruc developed a Python script to identify vulnerable Weaver E-cology systems by checking the accessibility of the susceptible API endpoint. Users are strongly urged to implement the latest updates to fortify their defenses against this ongoing threat.

As cyber threats evolve, staying informed and proactive in applying security patches is crucial to safeguarding enterprise systems. The ongoing exploitation of the Weaver E-cology vulnerability underscores the importance of timely updates and vigilant monitoring of enterprise security landscapes.

The Hacker News Tags:CVE-2026-22679, Cybersecurity, debug API, E-cology, Exploit, network security, NIST, Patch, Protection, QiAnXin, remote code execution, Security, Shadowserver Foundation, Vulnerability, Weaver

Post navigation

Previous Post: Critical Android Flaw Allows Remote Access Without User Action
Next Post: Microsoft Unveils Phishing Scheme Affecting Thousands Globally

Related Posts

Coruna Exploit Kit Targets iOS 13-17.2.1 with 23 Exploits Coruna Exploit Kit Targets iOS 13-17.2.1 with 23 Exploits The Hacker News
U.S. Arrests Key Facilitator in North Korean IT Worker Scheme, Seizes .74 Million U.S. Arrests Key Facilitator in North Korean IT Worker Scheme, Seizes $7.74 Million The Hacker News
 Google Sues China-Based Hackers Behind  Billion Lighthouse Phishing Platform  Google Sues China-Based Hackers Behind $1 Billion Lighthouse Phishing Platform The Hacker News
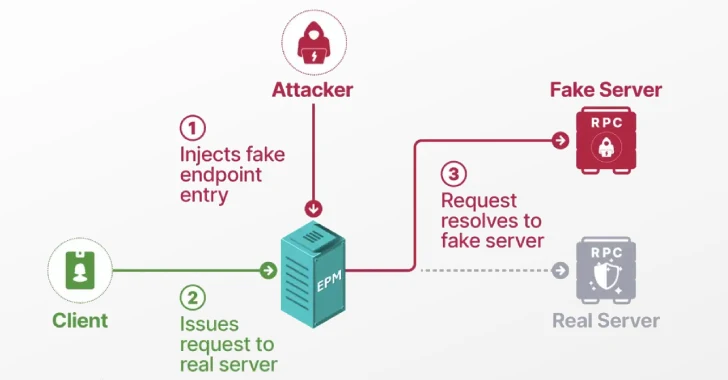
Researchers Detail Windows EPM Poisoning Exploit Chain Leading to Domain Privilege Escalation Researchers Detail Windows EPM Poisoning Exploit Chain Leading to Domain Privilege Escalation The Hacker News
AI Is Already the #1 Data Exfiltration Channel in the Enterprise AI Is Already the #1 Data Exfiltration Channel in the Enterprise The Hacker News
China-Linked DKnife Framework Exploits Routers for Attacks China-Linked DKnife Framework Exploits Routers for Attacks The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Top Container Registry Security Tools in 2026
  • Ransomware Developer Sentenced Amid Cybersecurity Alerts
  • Microsoft Resolves Critical Azure AI Foundry Security Issue
  • AI Malware Evolves Hourly to Evade Detection
  • Microsoft Updates Address AI and Cloud Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Top Container Registry Security Tools in 2026
  • Ransomware Developer Sentenced Amid Cybersecurity Alerts
  • Microsoft Resolves Critical Azure AI Foundry Security Issue
  • AI Malware Evolves Hourly to Evade Detection
  • Microsoft Updates Address AI and Cloud Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark