Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Fake Tax Pages Deliver Malware to Windows Systems

Fake Tax Pages Deliver Malware to Windows Systems

Posted on May 20, 2026 By CWS

Cybersecurity researchers have identified a new threat campaign targeting Windows users in India, utilizing fake income tax documents to distribute malware. The campaign, known as TAX#TRIDENT, has been tracked for its ability to employ multiple delivery methods while maintaining a convincing tax-related disguise.

How the Attack Operates

The campaign’s success does not rely on technical vulnerabilities but rather on tricking victims into accepting the authenticity of the malicious files. Fake Indian Income Tax assessment pages are used to coax users into downloading what appears to be genuine government documents. Once a user attempts to download the fake document, they unknowingly introduce a malicious file into their system.

Researchers from Securonix revealed that the campaign runs three distinct infection chains, all beginning with the same tax-related theme but diverging in execution. This flexibility allows attackers to adapt their methods if one avenue faces obstruction.

Details of the Attack Chains

The first infection path directs users to a counterfeit Indian Income Tax site, convincing them to download a ZIP file named ‘Assessment Letter.zip.’ This file contains a signed Windows executable, which installs a remote management client, allowing persistent access to the compromised system.

The second path involves a VBScript file named ‘Assessment_Order.vbs,’ served through various fake tax domains. This script silently installs the same remote management client while displaying a decoy tax image. Despite variations in domains and server addresses, the core malicious payload remains unchanged, as confirmed by identical SHA256 hashes.

Mitigation and Defense Strategies

Security experts recommend a focus on behavioral detection over domain or filename blocklists. Indicators such as unusual filenames, hidden directories, and abnormal network traffic should be prioritized. Monitoring script execution and changes to UAC policies is crucial for early detection.

The campaign’s third chain deviates by downloading a ManageEngine UEMS agent, which is then configured to connect to an attacker-controlled server. This method leverages legitimate software to create a covert remote access channel, complicating detection efforts.

Conclusion and Recommendations

The ongoing adaptability of the TAX#TRIDENT campaign poses significant challenges to cybersecurity defenses. By constantly evolving its delivery methods and maintaining core tactics, it remains a persistent threat. Users are advised to avoid downloading unsolicited tax-related files and to remain vigilant against unexpected prompts for downloads.

Security teams should enhance monitoring capabilities to detect and respond to suspicious activities effectively. A focus on behavioral signals rather than static indicators will be key in combating such sophisticated threats.
Cyber Security News Tags:cyber threats, Cybersecurity, data breach, Malware, Phishing, remote access, Securonix, tax scam, TAX#TRIDENT, Windows

Post navigation

Previous Post: Massive Android Ad Fraud Uncovered with 455 Apps
Next Post: Void Botnet Leverages Ethereum for Secure Command Control

Related Posts

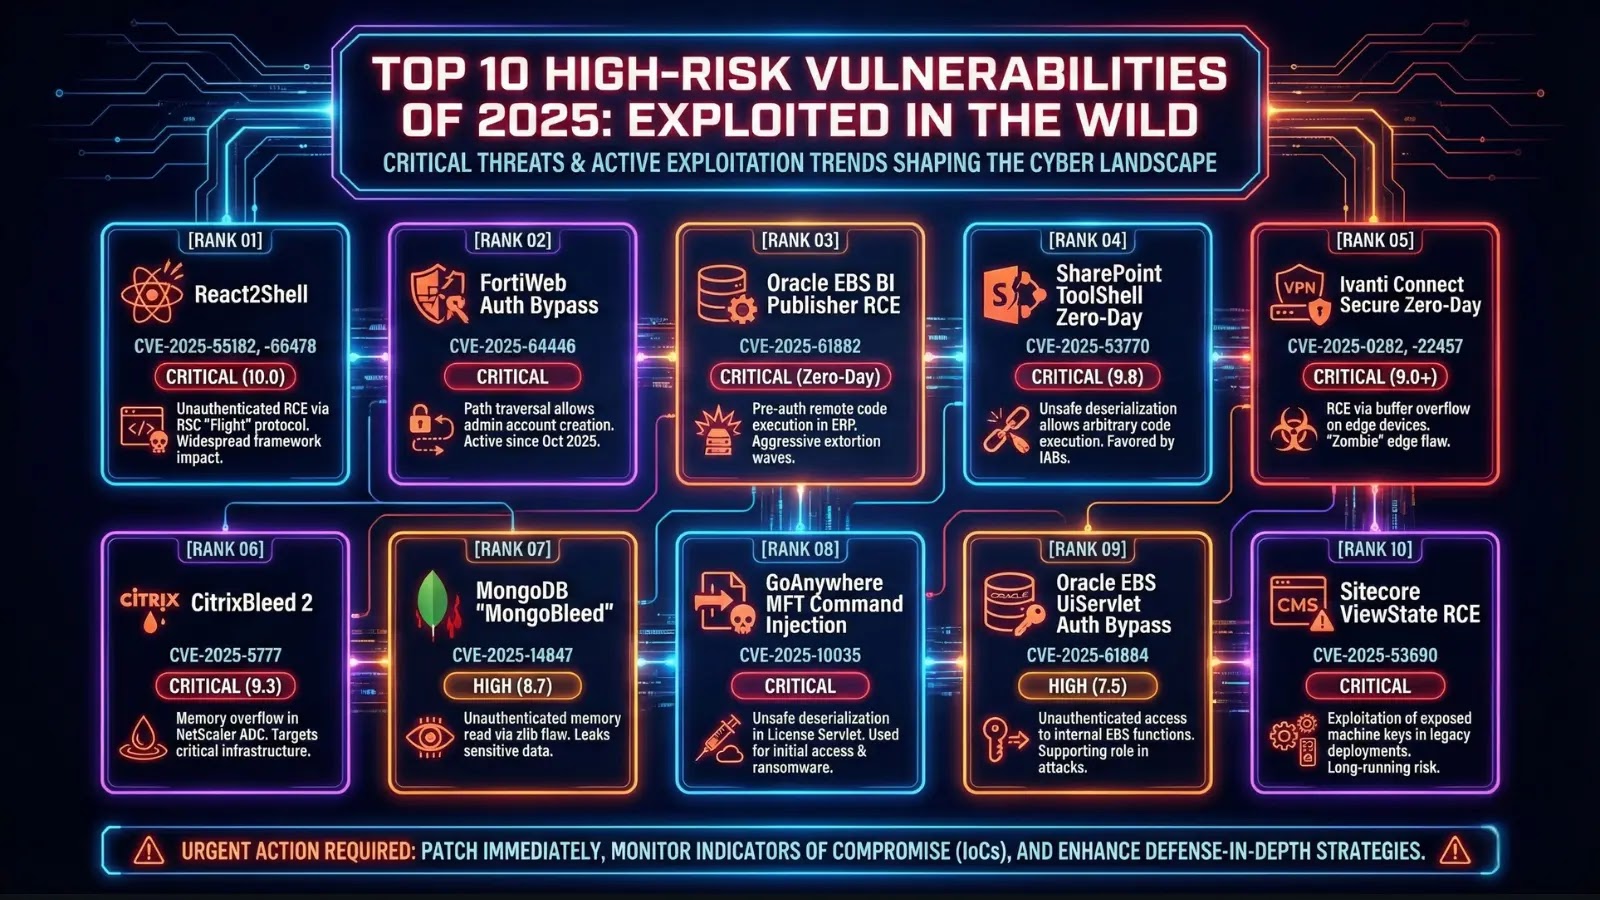
Top 10 High-Risk Vulnerabilities Of 2025 that Exploited in the Wild Top 10 High-Risk Vulnerabilities Of 2025 that Exploited in the Wild Cyber Security News
Urgent Chrome Update Fixes Critical 0-Day Vulnerability Urgent Chrome Update Fixes Critical 0-Day Vulnerability Cyber Security News
Samourai Wallet Cryptocurrency Mixing Founders Jailed for Laundering Over 7 Million Samourai Wallet Cryptocurrency Mixing Founders Jailed for Laundering Over $237 Million Cyber Security News
GTFire Phishing Attacks Exploit Google Services for Data Theft GTFire Phishing Attacks Exploit Google Services for Data Theft Cyber Security News
Hackers Exploit RTL/LTR Scripts and Browser Gaps to Hide Malicious URLs Hackers Exploit RTL/LTR Scripts and Browser Gaps to Hide Malicious URLs Cyber Security News
North Korean Hackers Attacking Developers with 338 Malicious npm Packages North Korean Hackers Attacking Developers with 338 Malicious npm Packages Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Trump Appoints Clayton to Lead Federal AI Task Force
  • South Korea Initiates Security Overhaul After Bank Data Breaches
  • China-Linked TA419 Targets U.S. AI Experts with Phishing
  • Key Arrest in ShinyHunters Case Aids FBI Investigation
  • Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher $50K

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Trump Appoints Clayton to Lead Federal AI Task Force
  • South Korea Initiates Security Overhaul After Bank Data Breaches
  • China-Linked TA419 Targets U.S. AI Experts with Phishing
  • Key Arrest in ShinyHunters Case Aids FBI Investigation
  • Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher $50K

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark