Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
New Malware Exploits Microsoft 365 Calendars for Covert Commands

New Malware Exploits Microsoft 365 Calendars for Covert Commands

Posted on July 20, 2026 By CWS

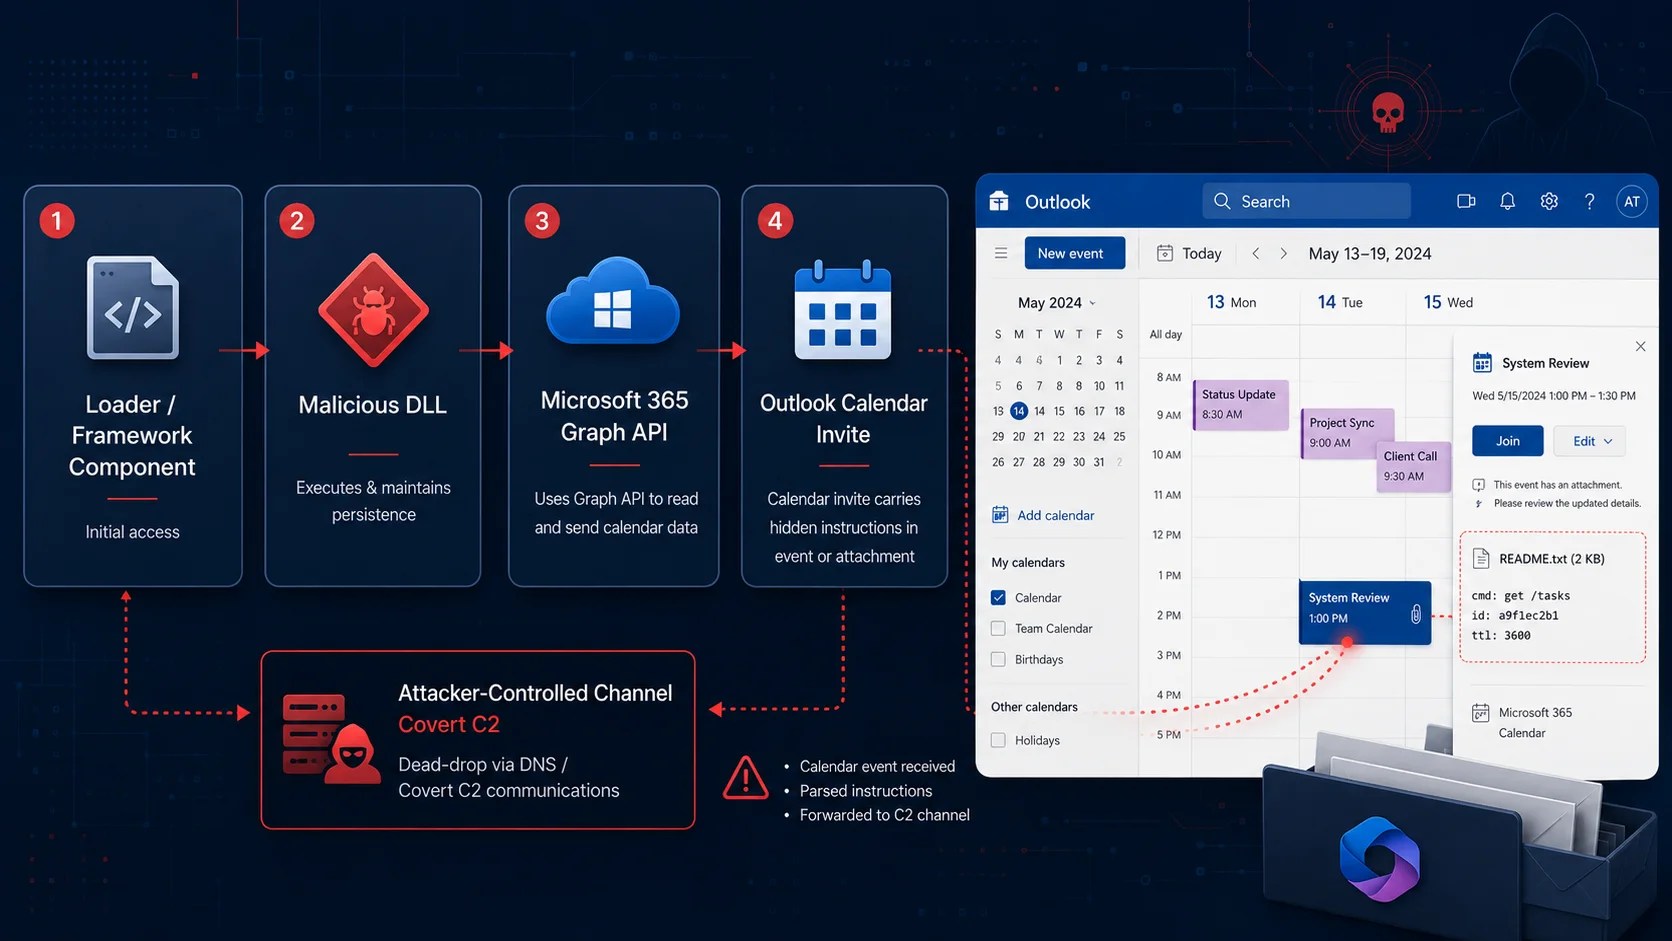
A sophisticated new cyber threat has emerged with the discovery of HOLLOWGRAPH, a malware that covertly communicates with hackers by hijacking Microsoft 365 calendars. By disguising its commands as typical calendar events, this malware remains under the radar while executing its malicious activities.

Malware Exploitation of Microsoft 365 Calendars

HOLLOWGRAPH is a malware component compiled in .NET, leveraging the Microsoft Graph API through compromised Microsoft 365 accounts. It transforms the mailbox calendar into a secret communication channel, or ‘dead drop’, for attackers. This malware operates using two basic commands: ‘get’ and ‘send’. By routing traffic through Microsoft’s cloud infrastructure, it blends seamlessly with regular business operations.

According to a report by Group-IB, attackers embed instructions within calendar events, while the malware extracts stolen files by creating encrypted events, hiding data within file attachments. To ensure these events are unnoticed by users, they are scheduled far into the future, specifically on May 13, 2050.

Additional Stealth Techniques

Beyond calendar manipulation, HOLLOWGRAPH employs DNS tunneling via IPv6 AAAA records to the domain ‘cloudlanecdn[.]com’. This tactic refreshes its Microsoft Entra ID credentials, storing them in a file misleadingly named ‘logAzure.txt’.

The data exchanged through the Graph API is secured with hybrid RSA and AES-256-GCM encryption, using distinct key pairs for incoming and outgoing data, ensuring cryptographic separation.

Attribution and Impact

Group-IB attributes HOLLOWGRAPH with high confidence to the Cavern backdoor framework, a toolkit previously linked to an Iranian actor known as Cavern Manticore. This is based on similar command syntax and shared self-command codes. Some technical similarities to the Lyceum group, associated with Iran’s Ministry of Intelligence and Security, were also noted, although this connection is less certain.

The campaign is not widespread; only 12 systems were identified as infected, with three actively communicating with attackers. The operation appears focused on Israeli organizations, indicating a targeted espionage effort rather than random attacks.

Protection and Detection Measures

Organizations can identify potential infections by searching for calendar events scheduled for 2050-05-13, or events with subjects resembling GUIDs or patterns like ‘Event ID:’ and ‘Boss{..}ID{..}’. Attachments may be named ‘File{n}.txt’.

Security teams should monitor Microsoft Graph activity for unexpected calendar changes, watch for unusual AAAA DNS queries, and flag the domain ‘cloudlanecdn[.]com’ and ‘logAzure.txt’ file. Group-IB advises enhancing cloud visibility, monitoring for misuse of trusted cloud services, and tightening controls on OAuth application permissions and Entra ID credentials to detect similar threats early.

Strengthen your SOC by integrating advanced threat detection tools with your current systems to ensure rapid identification and response to emerging cyber threats.
Cyber Security News Tags:Azure AD, Cavern Manticore, cloud security, cloudlanecdn.com, cyber espionage, Cybersecurity, DNS tunneling, Graph API, Group-IB, HollowGraph, Iranian threat actors, Lyceum, Malware, Microsoft 365, OilRig

Post navigation

Previous Post: Critical WordPress RCE Vulnerability Discovered by AI
Next Post: FakeGit Exploits GitHub to Distribute SmartLoader Malware

Related Posts

RondoDox Botnet Updated Their Arsenal with 650% More Exploits Targeting Enterprises RondoDox Botnet Updated Their Arsenal with 650% More Exploits Targeting Enterprises Cyber Security News
Biggest Ever GreedyBear Attack With 650 Hacking Tools Stolen  Million from Victims Biggest Ever GreedyBear Attack With 650 Hacking Tools Stolen $1 Million from Victims Cyber Security News
Google Enhances Chrome Security with Device-Bound Sessions Google Enhances Chrome Security with Device-Bound Sessions Cyber Security News
GREYVIBE Hackers Exploit AI for Sophisticated Cyberattacks GREYVIBE Hackers Exploit AI for Sophisticated Cyberattacks Cyber Security News
.NET 10.0.7 Update Fixes Critical Vulnerability .NET 10.0.7 Update Fixes Critical Vulnerability Cyber Security News
Malicious Ads Deploy FlutterShell Backdoor on macOS Malicious Ads Deploy FlutterShell Backdoor on macOS Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI-Driven Attacks Target Over 100 Companies, Cost $5,000
  • SBI Alleged Data Breach: Hackers Claim Access to Vast Database
  • ROMULUS Platform Exploited by Hackers for Malware Distribution
  • AI Uncovers Hidden Cryptocurrency Miner on Mac
  • AI Agents Pose Potential Security Risks, Microsoft Warns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI-Driven Attacks Target Over 100 Companies, Cost $5,000
  • SBI Alleged Data Breach: Hackers Claim Access to Vast Database
  • ROMULUS Platform Exploited by Hackers for Malware Distribution
  • AI Uncovers Hidden Cryptocurrency Miner on Mac
  • AI Agents Pose Potential Security Risks, Microsoft Warns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark