Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft Entra ID to End SMS Sign-In by 2027

Microsoft Entra ID to End SMS Sign-In by 2027

Posted on September 21, 2026 By CWS

Microsoft has announced its decision to phase out SMS first-factor sign-in for Microsoft Entra ID workforce tenants globally by February 1, 2027. The transition requires organizations to shift affected users to more secure authentication methods before the deadline.

Reasons Behind the Transition

The move aims to enhance security by eliminating the use of registered phone numbers and SMS one-time passcodes as primary sign-in methods. This change could affect access to Microsoft 365 and other Entra-protected services if not properly managed by administrators.

The existing system, known as SignInNoPassword, allows users to authenticate using a phone number and a six-digit SMS code instead of a traditional username and password. Originally created to aid frontline workers, Microsoft now advises a shift to modern, phishing-resistant authentication methods.

Impact on Current Users

Beginning in February 2027, attempts to authenticate using a phone number and SMS code as the primary factor will be blocked. This change applies to worldwide and US Government Community Cloud tenants but excludes Azure AD B2C or Microsoft Entra External ID scenarios.

Users with alternative authentication methods can continue accessing their accounts. However, accounts solely dependent on SMS sign-in face potential access issues. Microsoft is moving away from SMS-based authentication due to vulnerabilities such as phishing, SIM-swapping, and interception risks.

Recommended Actions for Organizations

Organizations should treat the February 2027 deadline as an identity migration project. This involves transitioning from SMS-based methods to secure alternatives like passkeys, which use FIDO standards and origin-bound public-key cryptography, offering resistance to phishing attacks.

Administrators should first identify users relying on SMS sign-in and check for available alternative methods. It is crucial to address shared-device environments and users without corporate smartphones. Recommended alternatives include passkeys, Windows Hello, and FIDO2 security keys.

Implementing a staged migration with comprehensive user communication and support will help mitigate last-minute issues. By acting now, organizations can prevent access disruptions and enhance their security posture.

The February 2027 deadline represents a significant shift towards increased security. By adopting phishing-resistant credentials and eliminating SMS dependencies, organizations can avoid lockouts and strengthen their Microsoft Entra ID security framework.
Cyber Security News Tags:Authentication, cloud tenants, Cybersecurity, Entra ID, February 2027, FIDO, IT management, Microsoft, Passkeys, Passwordless, Phishing, Security, SMS authentication, Technology

Post navigation

Previous Post: Fake LastPass App Distributes Rapuncel Malware
Next Post: Cyberattacks Target Colorado Water Utilities’ OT Systems

Related Posts

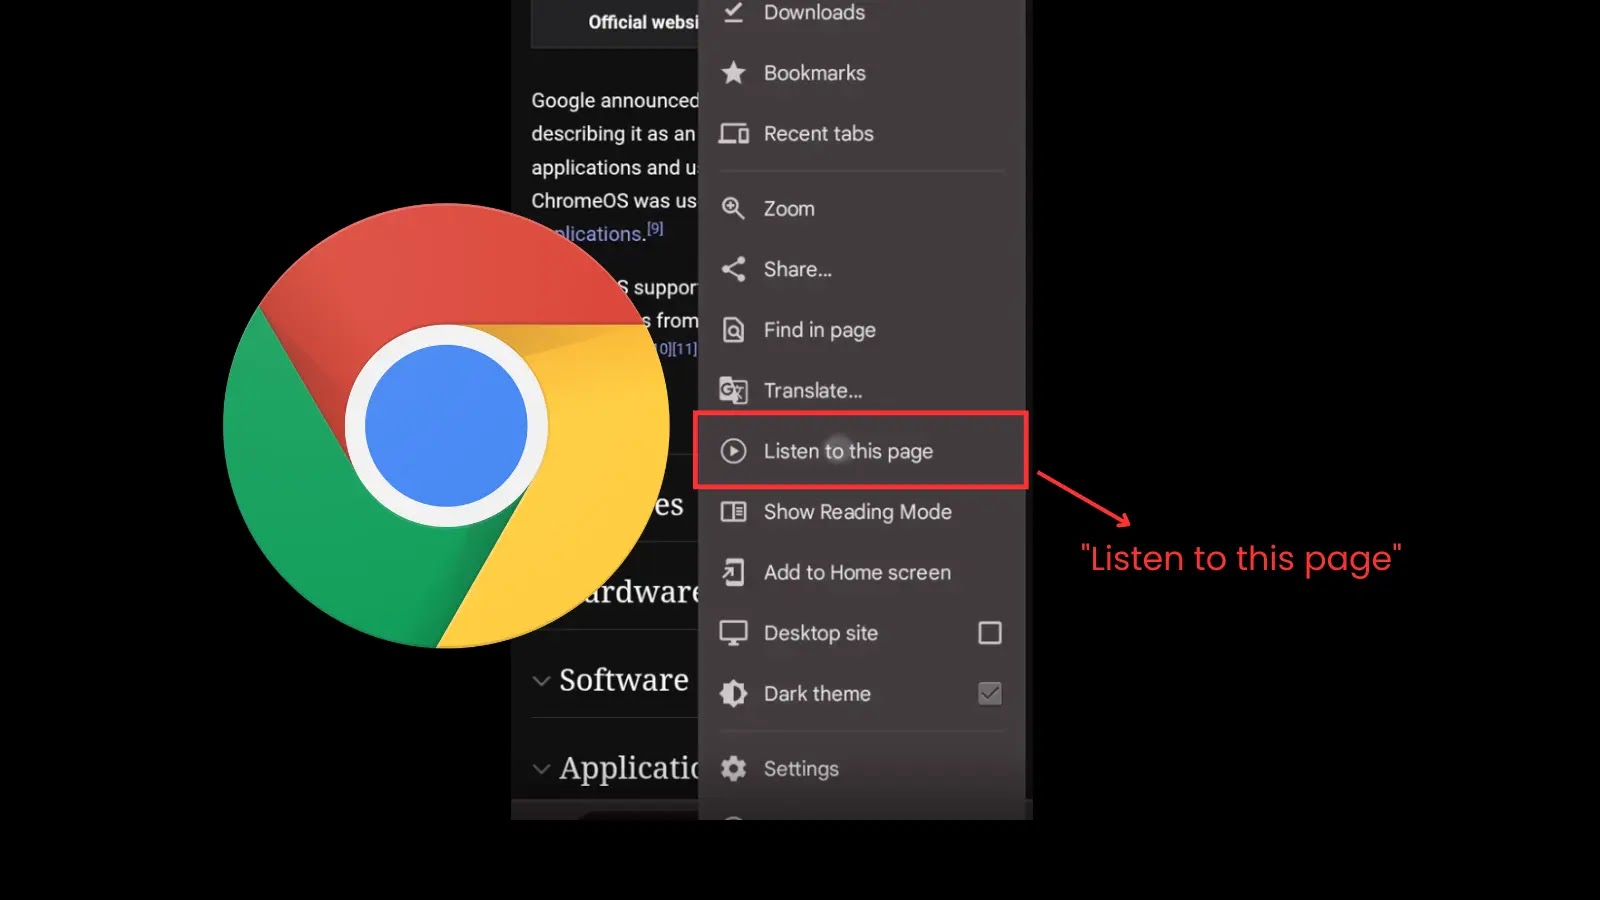
Google Chrome May Soon Turn Webpages Into Podcasts With AI Audio Overviews Google Chrome May Soon Turn Webpages Into Podcasts With AI Audio Overviews Cyber Security News
Malicious npm Package Exploits Hugging Face for Cyber Attacks Malicious npm Package Exploits Hugging Face for Cyber Attacks Cyber Security News
US Firms Under Siege from New JS.MonoGlyphRAT Malware US Firms Under Siege from New JS.MonoGlyphRAT Malware Cyber Security News
Scammers Exploit Azure for Fake Security Alerts in 80 Firms Scammers Exploit Azure for Fake Security Alerts in 80 Firms Cyber Security News
Salt Typhoon Using Zero-Day Exploits and DLL Sideloading Techniques to Attack Organizations Salt Typhoon Using Zero-Day Exploits and DLL Sideloading Techniques to Attack Organizations Cyber Security News
Linux Cryptomining Attack Uses PAM to Conceal XMRig Botnet Linux Cryptomining Attack Uses PAM to Conceal XMRig Botnet Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Dark Project Ransomware Offers 80% Cut to Hackers
  • White House Network Found Hosting Residential Proxies
  • OpenSSH SSHole Vulnerability Exploited by Hackers
  • Massive WordPress Vulnerability Exploit Attempts Uncovered
  • Ahold Delhaize Faces Major Financial Hit from Cyberattack

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Dark Project Ransomware Offers 80% Cut to Hackers
  • White House Network Found Hosting Residential Proxies
  • OpenSSH SSHole Vulnerability Exploited by Hackers
  • Massive WordPress Vulnerability Exploit Attempts Uncovered
  • Ahold Delhaize Faces Major Financial Hit from Cyberattack

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark