Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft Probes Teams Calling Disruption Affecting Users

Microsoft Probes Teams Calling Disruption Affecting Users

Posted on September 21, 2026 By CWS

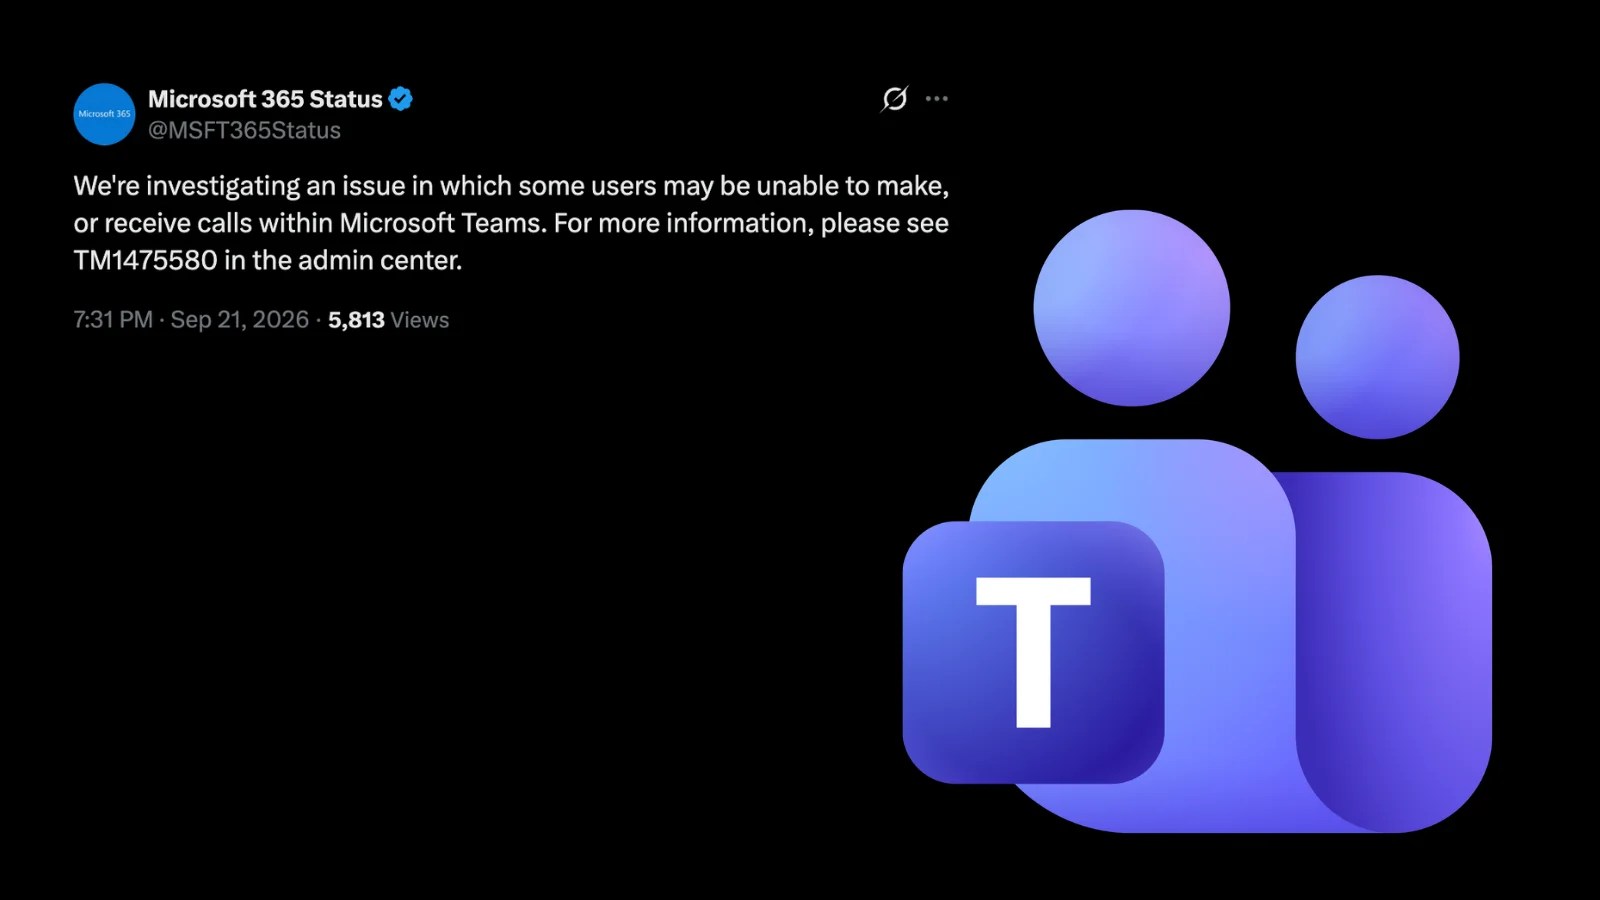
Microsoft is currently investigating an issue impacting the calling functionality in its Teams application. This disruption is preventing certain users from making or receiving calls through the platform, according to the company’s announcement via the Microsoft 365 Status account on September 21. Administrators are advised to refer to incident TM1475580 in the Microsoft 365 admin center for specific details.

Impact and Scope of the Service Incident

The advisory notes that the problem is affecting only ‘some users,’ but does not specify regions, customer segments, or the type of calls affected. The lack of detailed information leaves businesses uncertain about the full extent of the disruption, emphasizing the need for organizations to assess their own systems for any related issues.

While the issue is currently limited to calls, organizations are cautioned against assuming other features like chat, messaging, or file sharing are unaffected unless their telemetry suggests otherwise. The incident could impact critical business operations such as help desks, contact centers, and executive communications.

Operational Considerations for Businesses

For IT and security teams, distinguishing between this service-side issue and potential local faults or malicious activities is crucial. Administrators are encouraged to examine user reports alongside Microsoft’s advisory and review network, endpoint, and identity logs to rule out other causes.

To manage the disruption, administrators should log into the admin center to check for tenant-specific impact statements and updates related to TM1475580. The admin center remains the primary source for understanding an organization’s specific exposure to the issue.

Maintaining Communication and Security

During the ongoing investigation, businesses are urged to implement resilient communication plans. This might involve using PSTN calling, designated conference bridges, or corporate mobile phones as interim solutions, rather than altering existing configurations broadly.

Employees should be reminded to rely on approved tools for sensitive discussions, as unexpected outages can increase the risks of phishing attacks, fake support communications, and unauthorized data exchanges.

Microsoft’s investigation into the Teams calling issue continues. Administrators are advised to keep track of the incident’s progress, share updates internally, and revert any temporary strategies once Microsoft confirms the restoration of normal service.

For businesses, this incident underscores the importance of having robust contingency plans to ensure continuity and security in communication operations.

Cyber Security News Tags:admin center, business communication, call issues, incident response, IT management, Microsoft, Microsoft 365, service disruption, service health, Teams

Post navigation

Previous Post: Cyberattacks Target Colorado Water Utilities’ OT Systems

Related Posts

Phishing Emails Exploit Code of Conduct in AiTM Attack Phishing Emails Exploit Code of Conduct in AiTM Attack Cyber Security News
AI Phishing Is Your Company’s Biggest Security Risk in 2026 AI Phishing Is Your Company’s Biggest Security Risk in 2026 Cyber Security News
New JSCEAL Attack Targeting Crypto App Users To Steal Credentials and Wallets New JSCEAL Attack Targeting Crypto App Users To Steal Credentials and Wallets Cyber Security News
Hackers Mimic ReliaQuest Staff for Credential Theft Hackers Mimic ReliaQuest Staff for Credential Theft Cyber Security News
Cloudflare Warns of DDoS Attacks Targeting Journalists and News Organizations Cloudflare Warns of DDoS Attacks Targeting Journalists and News Organizations Cyber Security News
Threat Actors Leverage Google Apps Script To Host Phishing Websites Threat Actors Leverage Google Apps Script To Host Phishing Websites Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft Probes Teams Calling Disruption Affecting Users
  • Cyberattacks Target Colorado Water Utilities’ OT Systems
  • Microsoft Entra ID to End SMS Sign-In by 2027
  • Fake LastPass App Distributes Rapuncel Malware
  • PowerShell Backdoor TASK#STOMP Steals Sensitive Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft Probes Teams Calling Disruption Affecting Users
  • Cyberattacks Target Colorado Water Utilities’ OT Systems
  • Microsoft Entra ID to End SMS Sign-In by 2027
  • Fake LastPass App Distributes Rapuncel Malware
  • PowerShell Backdoor TASK#STOMP Steals Sensitive Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark