Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
WatchGuard API Flaws Allow Command Execution

WatchGuard API Flaws Allow Command Execution

Posted on September 29, 2026 By CWS

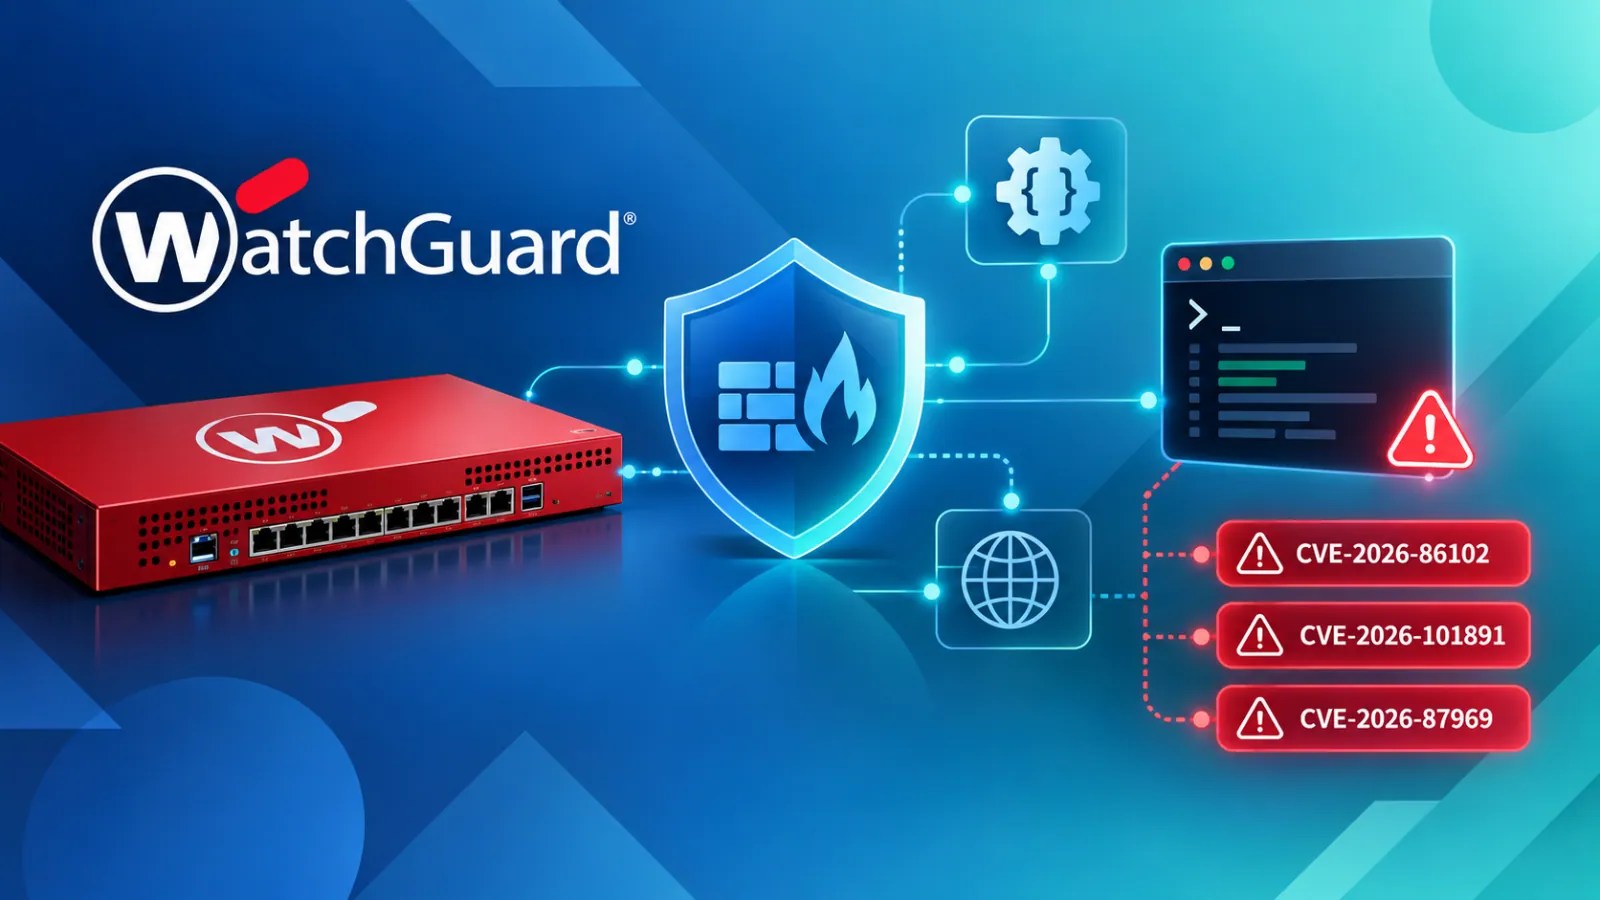
WatchGuard has released details about three security vulnerabilities affecting its AP devices, with two posing critical risks. These flaws could enable unauthorized access and command execution on susceptible access points.

Organizations using firmware versions prior to 3.4.8 are urged to immediately upgrade. The vulnerabilities, disclosed on September 28, 2026, impact WatchGuard APs from versions 1.0 through 3.4.7.

Critical Vulnerabilities in WatchGuard APs

The most severe vulnerability, identified as CVE-2026-86102, is an OS command injection flaw in the internal management API, scoring 9.3 on the CVSS v4 scale. Attackers with network access can exploit this by sending crafted inputs to execute arbitrary shell commands.

No user authentication is required, making this flaw dangerous when the API service is exposed to untrusted networks.

Access Control Flaws and Risk Mitigation

The second critical issue, CVE-2026-101891, also rated 9.3, arises from poor access control in an internal API service. This allows unauthenticated attackers to access protected functionalities, potentially leading to further compromises.

The third vulnerability, CVE-2026-87969, is a high-severity command injection problem, rated 8.6. Exploitation requires authenticated administrator privileges, allowing malicious users to execute operating system commands via the diagnostic command-line interface.

Securing Your Network Against Exploits

Security teams should identify and update all WatchGuard AP devices running firmware versions earlier than 3.4.8. Access to management interfaces and internal API services should be restricted to trusted networks.

Reviewing access logs, administrative activities, and configuration changes is crucial for detecting suspicious actions. Rotating administrative credentials is advised if any exposure is suspected.

Network segmentation can limit the impact of compromised devices by restricting their communication with critical systems. Currently, there is no evidence of active exploitation or public proof-of-concept for these vulnerabilities, but their critical nature necessitates immediate action.
Cyber Security News Tags:access control, API vulnerabilities, command execution, critical flaws, CVE-2026-86102, Cybersecurity, firmware update, network appliances, network security, OS command injection, security update, unauthorized access, WatchGuard

Post navigation

Previous Post: Microsoft Analyzes NeedyMantis Malware from Daemon Tools Hack
Next Post: Dutch Authorities Detain Hacker Tied to ShinyHunters

Related Posts

Interlock Ransomware Employs ClickFix Technique to Run Malicious Commands on Windows Machines Interlock Ransomware Employs ClickFix Technique to Run Malicious Commands on Windows Machines Cyber Security News
Attackers Exploiting React2Shell Vulnerability to Attack IT Sectors Attackers Exploiting React2Shell Vulnerability to Attack IT Sectors Cyber Security News
Google Chrome 0-Day Vulnerability Actively Exploited in the Wild Google Chrome 0-Day Vulnerability Actively Exploited in the Wild Cyber Security News
VMware Tools and Aria 0-Day Vulnerability Exploited for Privilege Escalation and Code Execution VMware Tools and Aria 0-Day Vulnerability Exploited for Privilege Escalation and Code Execution Cyber Security News
Microsoft Investigating Issue Impacting Exchange Online, Teams, and M365 Suite Microsoft Investigating Issue Impacting Exchange Online, Teams, and M365 Suite Cyber Security News
Critical Flaw in Check Point Servers Actively Exploited Critical Flaw in Check Point Servers Actively Exploited Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • BotHelper RAT Exploits Encrypted Payloads for Windows Surveillance
  • Dutch Authorities Detain Hacker Tied to ShinyHunters
  • WatchGuard API Flaws Allow Command Execution
  • Microsoft Analyzes NeedyMantis Malware from Daemon Tools Hack
  • Amsterdam Man Arrested in ShinyHunters Hacking Probe

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • BotHelper RAT Exploits Encrypted Payloads for Windows Surveillance
  • Dutch Authorities Detain Hacker Tied to ShinyHunters
  • WatchGuard API Flaws Allow Command Execution
  • Microsoft Analyzes NeedyMantis Malware from Daemon Tools Hack
  • Amsterdam Man Arrested in ShinyHunters Hacking Probe

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark