A deceptive Zoom installer has been identified as a threat to Mac users, tricking them into revealing their login credentials and unknowingly launching a new backdoor named CloudSyncD. This malware masquerades as a familiar application, using misleading instructions and fake prompts to transform a standard setup process into a privileged compromise.
The Emergence of CloudSyncD
The initial sample of this malware was discovered on September 15, 2026, while it was still under development. Within a mere two days, researchers had traced related builds that pointed to accessible command and control servers across two domains, indicating an impending deployment. However, the report lacks specific details on the number of infections, affected entities, or financial losses incurred. The malware was first detected by Jamf Threat Labs during their routine analysis of executables submitted to VirusTotal.
According to a report shared with Cyber Security News, CloudSyncD operates through a two-stage process. The backdoor is embedded within the installer itself, rather than being downloaded separately, posing immediate risks of unauthorized execution with elevated privileges and potential for additional malicious payloads.
Fake Installation Process
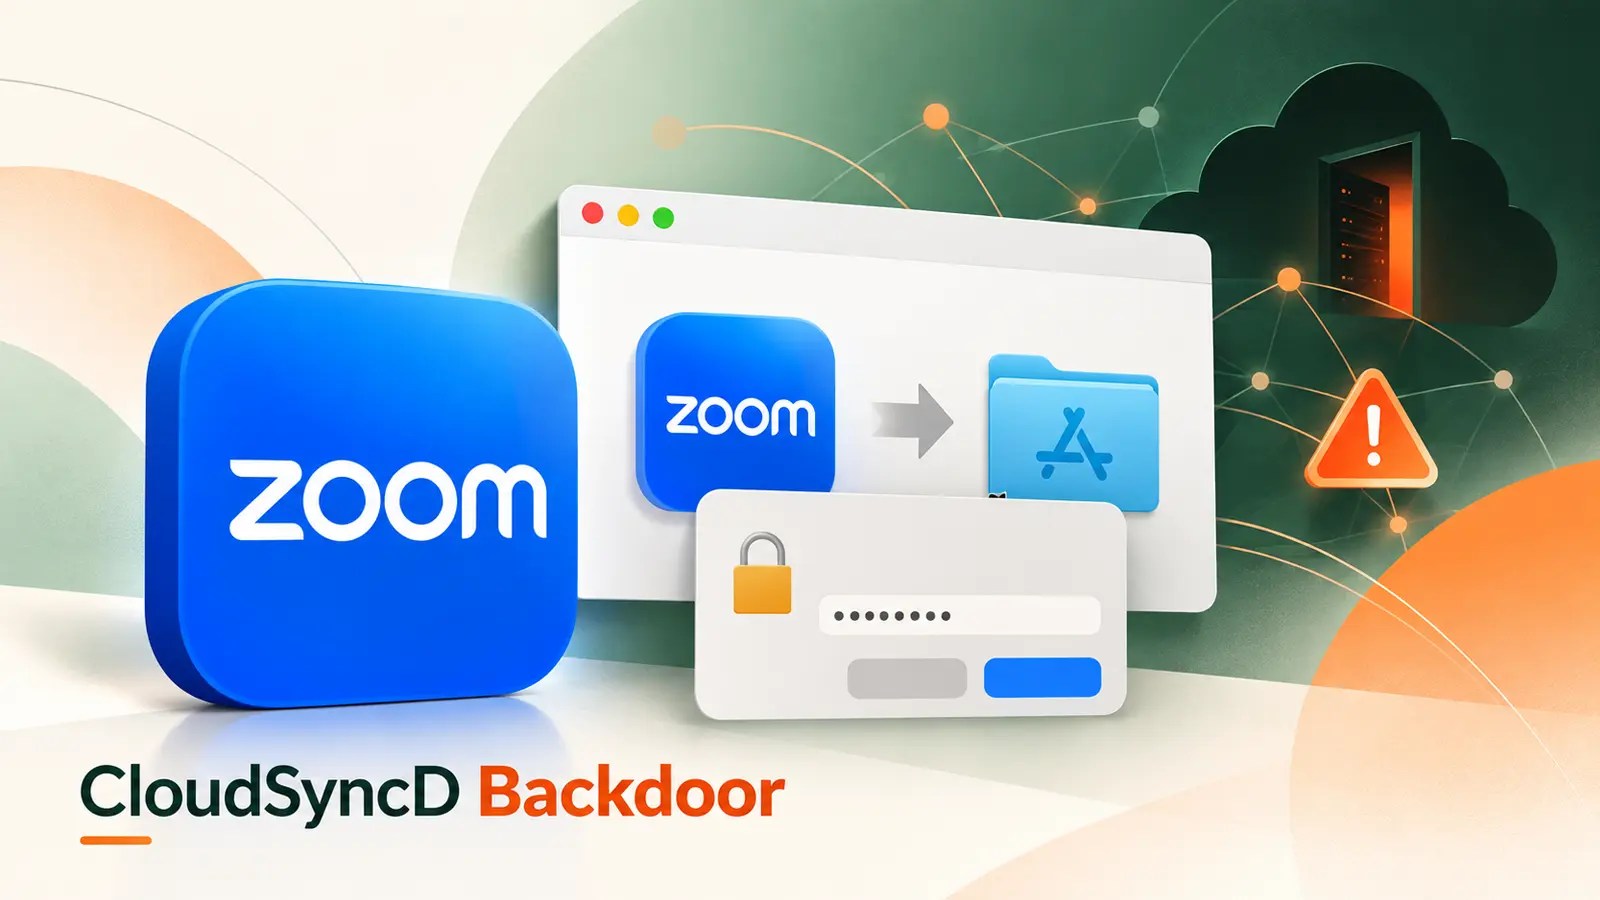
The counterfeit Zoom installer presents a familiar interface, pairing an application icon with an Applications shortcut. Users are led through a series of steps that direct them into System Settings, then Privacy & Security settings, where they are instructed to select ‘Open Anyway’ and enter their administrator password. This method circumvents Gatekeeper protections as the application lacks a verified developer signature.
The installer uses a fake authorization dialog to repeatedly prompt for the user’s password until successful authentication is achieved. This captured password is then hidden within a seemingly normal settings file, obfuscated with random characters and invisible Unicode markers to identify its position.
Operational Details and Security Recommendations
CloudSyncD is compatible with both Apple silicon and Intel-based Macs. On initial contact, it sends a device survey including hardware details, operating system information, and network data. Subsequent interactions primarily transmit hardware identifiers with live traffic observed every eight to 16 seconds. The server can then send encrypted tasks containing executable programs, either directly or within compressed archives.
Despite these capabilities, the researchers did not find evidence of persistence, application replacement, or delivery of remote tasks. Unlike other backdoor infections that establish startup mechanisms, the samples remained at their staging locations. Jamf recommends blocking and reporting similar threats through endpoint security measures and web protections.
For investigators, the report highlights encrypted implant logs, hidden characters in settings files, and password-validation command lines as key indicators of compromise. These details can aid in the detection and prevention of similar threats in the future.
Indicators of compromise (IoCs) such as SHA-256 hashes and command-and-control endpoints are detailed in the report, providing crucial information for cybersecurity professionals to track and mitigate the threat effectively.