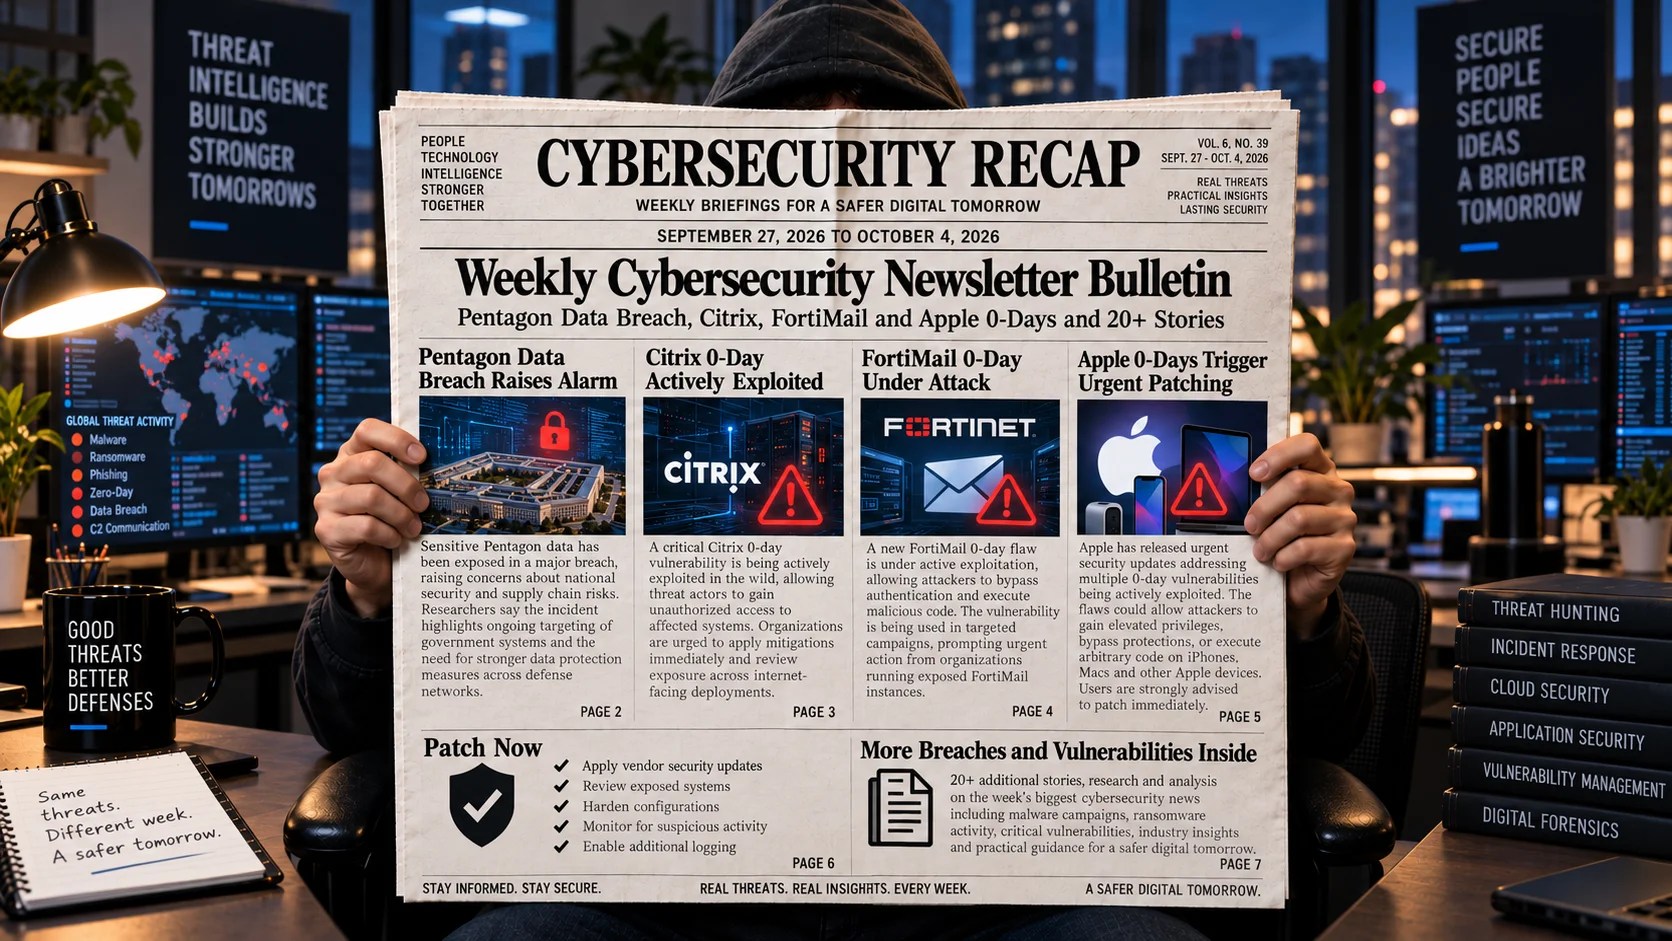
This week, the cybersecurity landscape was heavily influenced by a substantial data breach at the Pentagon, impacting the personal data of millions, alongside vulnerabilities in major companies like Apple and Fortinet. These incidents highlight the growing challenges in safeguarding sensitive information from unauthorized access and exploitation.
Pentagon’s Significant Data Breach
The Pentagon revealed an unauthorized access event involving the Defense Manpower Data Center, compromising the data of 2.76 million individuals. This breach, resulting from a file-sharing vulnerability, exposed personal and demographic details, though no evidence of misuse has been reported yet. The prolonged exposure of such data poses ongoing risks of fraud and impersonation.
The breach underscores the importance of robust data protection measures. Affected individuals are being offered credit monitoring and identity restoration services as a precaution against potential identity theft and fraud.
Apple and Fortinet Zero-Day Exploits
Apple has released updates for iOS and iPadOS to address a critical zero-day vulnerability in CoreGraphics, which was actively being exploited. The flaw allowed attackers to execute arbitrary code through malicious files, affecting iPhone 11 models and later. Users are strongly advised to apply these updates promptly to mitigate potential risks.
Similarly, Fortinet alerted users to a critical zero-day in FortiMail, which is actively exploited. This vulnerability could enable attackers to write files using crafted HTTP requests, prompting administrators to take immediate security measures and apply the necessary patches.
Unresolved Citrix RCE Vulnerabilities
Security firm watchTowr has identified two remote-code-execution vulnerabilities in Citrix’s NetScaler, which are reportedly being exploited. Although Citrix has not yet released an official advisory or patches, organizations using NetScaler are urged to mitigate exposure by restricting access and preserving evidence for further investigation.
As these vulnerabilities remain unpatched, high-risk organizations should consider isolating affected systems and closely monitoring Citrix’s channels for updates.
Impact on Security Infrastructure
These incidents emphasize the critical need for organizations to stay vigilant and proactive in securing their digital infrastructure. The increasing sophistication of cyber threats demands constant updates and monitoring to prevent unauthorized access and data breaches.
Security teams are encouraged to implement comprehensive security frameworks, conduct regular vulnerability assessments, and maintain up-to-date systems to protect against evolving cyber threats. The recent breaches serve as a wake-up call for enhanced protective measures across all sectors.