Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Legacy WebBrowser Control Exploits Lead to RCE

Legacy WebBrowser Control Exploits Lead to RCE

Posted on June 8, 2026 By CWS

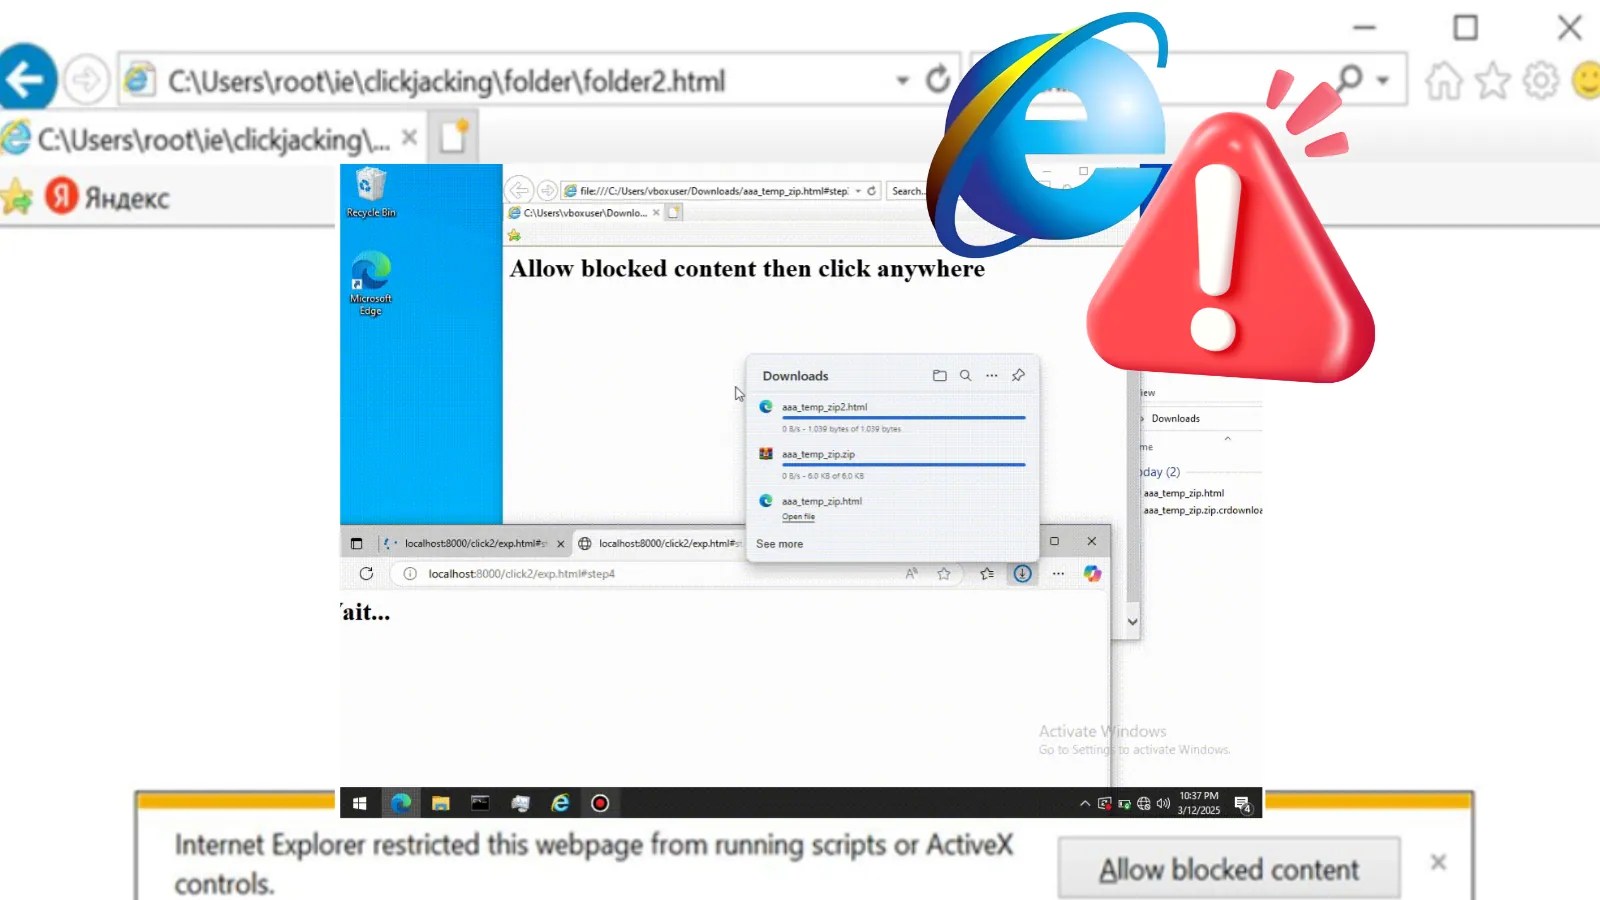
The legacy WebBrowser control within Internet Explorer remains a significant security risk, enabling attackers to achieve remote code execution (RCE) on Windows systems through a single user interaction. Despite Internet Explorer being officially retired, its embedded components in various applications continue to pose vulnerabilities.

Exploitation of Internet Explorer’s Legacy Components

Security researchers at PT Security have highlighted how attackers exploit Internet Explorer’s zone model, Mark of the Web (MOTW), and COM/ActiveX components to execute code remotely. The mshtml engine and WebBrowser control are integral to many desktop applications, particularly older VB, .NET, and C/C++ tools, which often lack adequate HTML and JavaScript sanitization, making them susceptible to cross-site scripting (XSS) attacks.

Mechanics of the RCE Attack Chain

Once attackers achieve script execution within a localhost context, they harness Internet Explorer’s handling of localhost and file zones to open local HTML files, effectively elevating the script’s privileges. A timing flaw in Internet Explorer’s window operations permits crafted JavaScript to open these files without security prompts, enabling the bypass of MOTW restrictions.

Microsoft has addressed the direct execution from localhost scripts, yet the attack chain persists. By leveraging both Internet Explorer and Microsoft Edge, attackers can bypass MOTW, turning remote payloads into local scripts without security warnings, thus facilitating higher-privilege execution.

Mitigation Strategies and Future Outlook

To mitigate these risks, experts recommend replacing Internet Explorer’s WebBrowser control with modern, sandboxed alternatives. Eliminating XSS vulnerabilities in localhost web interfaces and enforcing stringent ActiveX/COM policies are critical steps. Additionally, enhancing MOTW-based execution rules can significantly reduce exposure to these exploits.

The continued reliance on outdated components like Internet Explorer’s WebBrowser control underscores the importance of proactive cybersecurity measures. Organizations must prioritize updating legacy systems to prevent exploitation and safeguard against potential threats.

Stay informed about the latest cybersecurity developments by following us on Google News, LinkedIn, and X.
Cyber Security News Tags:ActiveX, COM components, Cybersecurity, Internet Explorer, Microsoft Edge, MOTW, RCE, Security, WebBrowser control, XSS

Post navigation

Previous Post: Critical VMware XSS Vulnerabilities Exposed
Next Post: VerdantBamboo Targets Linux with New BRICKSTORM Variant

Related Posts

CISA Adds Digiever Authorization Vulnerability to KEV List Following Active Exploitation CISA Adds Digiever Authorization Vulnerability to KEV List Following Active Exploitation Cyber Security News
Mythos Preview AI Revolutionizes Vulnerability Exploitation Mythos Preview AI Revolutionizes Vulnerability Exploitation Cyber Security News
BlackHat AI Hacking Tool WormGPT Variant Powered by Grok and Mixtral BlackHat AI Hacking Tool WormGPT Variant Powered by Grok and Mixtral Cyber Security News
CodeIgniter Vulnerability Exposes Million of Webapps to File Upload Attacks CodeIgniter Vulnerability Exposes Million of Webapps to File Upload Attacks Cyber Security News
Multiple HPE StoreOnce Vulnerabilities Let Attackers Execute Malicious Code Remotely Multiple HPE StoreOnce Vulnerabilities Let Attackers Execute Malicious Code Remotely Cyber Security News
Vidar 2.0 Malware Targets Gamers via Fake Cheats Vidar 2.0 Malware Targets Gamers via Fake Cheats Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Top Email Encryption Services of 2026 Revealed
  • Capcom Data Breach Exposes 11 Million Emails
  • x402 SDK Vulnerability Poses Risks to AI Agent Tokens
  • Cisco Expressway Flaw Allows Remote Access as Root
  • LiteLLM Faces Supply Chain Breach, Compromised Packages Removed

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Top Email Encryption Services of 2026 Revealed
  • Capcom Data Breach Exposes 11 Million Emails
  • x402 SDK Vulnerability Poses Risks to AI Agent Tokens
  • Cisco Expressway Flaw Allows Remote Access as Root
  • LiteLLM Faces Supply Chain Breach, Compromised Packages Removed

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark