Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
ClickFix Campaign Exploits Fake CAPTCHA for Malware

ClickFix Campaign Exploits Fake CAPTCHA for Malware

Posted on October 5, 2026 By CWS

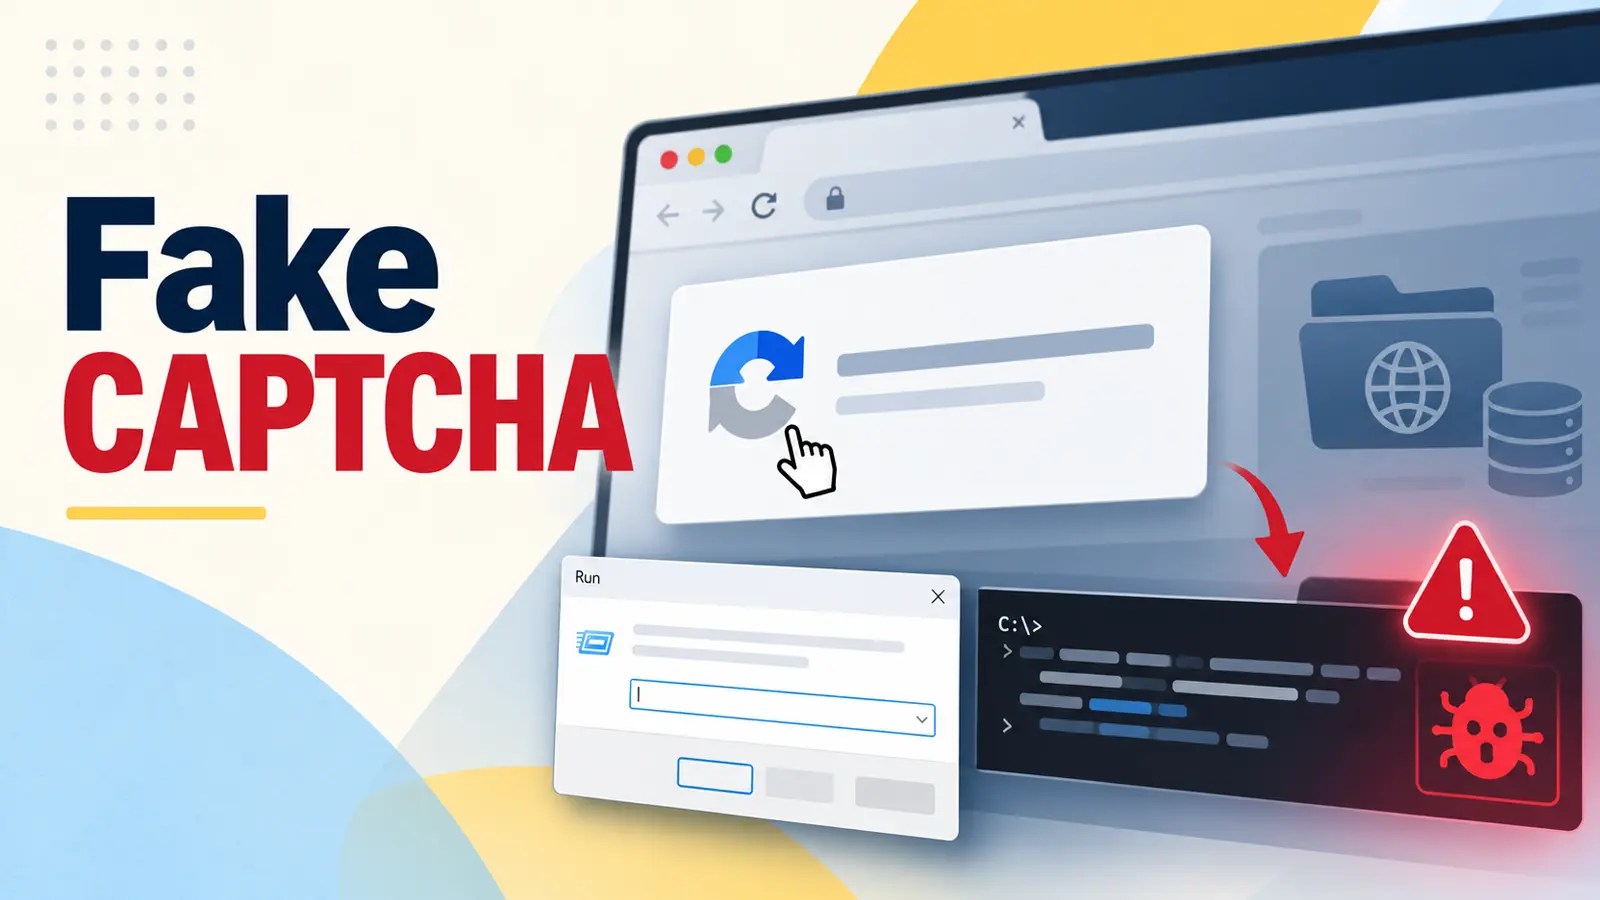
The ClickFix campaign has introduced a novel method for delivering malware through fake CAPTCHA prompts on compromised websites. Users are tricked into executing commands that lead to malware infections, making this a significant threat in web security.

How the ClickFix Campaign Operates

This malicious campaign begins when a user visits an altered website. The site presents a deceptive CAPTCHA or repair prompt, instructing users to open the Windows Run dialog, paste a specific command, and execute it. Unlike legitimate CAPTCHA checks, this method requires users to run system commands, which is unusual and risky.

Microsoft Threat Intelligence has shed light on how these attacks are executed. The attackers cleverly store a malicious script disguised as a PNG file within the browser cache. This script is downloaded beforehand, minimizing the need for obvious downloads and allowing attackers to execute commands more covertly.

Technical Aspects and Risks

The attack leverages Windows Script Host to execute a VBScript, which is stored in the browser cache. This VBScript retrieves additional malicious scripts, such as a PowerShell script, furthering the attack’s reach. The design targets credential theft, as attackers aim to harvest sensitive information from the victim’s device.

Compromised websites involved in these attacks do not follow standard malware patterns, as they prefetch the harmful script into the cache rather than downloading it during execution. This technique aids in evading detection by conventional security measures that focus on new downloads.

Preventive Measures and Detection

Security experts suggest several measures to combat these threats. Microsoft recommends enabling cloud-delivered and web protection, along with thorough monitoring of browser-cache activities and unusual child processes. Investigating alerts for command execution and outbound connections can be crucial in detecting these attacks.

Users are advised to be cautious of any webpage requesting them to paste commands into system dialogs like Run, Terminal, or PowerShell. Recognizing this boundary can prevent the execution of harmful commands, even when the payload is preloaded.

Conclusion and Future Outlook

The ClickFix campaign highlights a growing trend in human-led infection strategies that exploit user trust in security processes. While Microsoft has not disclosed the full scope of affected individuals, the campaign underlines the importance of vigilance and robust security practices to mitigate such threats. Continued research and updates from security teams will be vital in countering this evolving threat landscape.

Cyber Security News Tags:browser cache, ClickFix, credential theft, Cybersecurity, fake CAPTCHA, Malware, malware protection, Microsoft Threat Intelligence, security alert, web safety

Post navigation

Previous Post: AI Exploit in Zammad Exposes Critical Security Flaws
Next Post: RemoveMacAI Clears 12GB by Eliminating Apple AI Models

Related Posts

Malvertising Campaign Exploits Tax Season with EDR Attacks Malvertising Campaign Exploits Tax Season with EDR Attacks Cyber Security News
Server Leak Uncovers TheGentlemen Ransomware Toolkit Server Leak Uncovers TheGentlemen Ransomware Toolkit Cyber Security News
Promptware Kill Chain – Five-Step Kill Chain Model for Analyzing Cyberthreats Promptware Kill Chain – Five-Step Kill Chain Model for Analyzing Cyberthreats Cyber Security News
Critical AVEVA Software Vulnerabilities Enables Remote Code Execution Under System Privileges Critical AVEVA Software Vulnerabilities Enables Remote Code Execution Under System Privileges Cyber Security News
Hackers Hijacked 18 Very Popular npm Packages With 2 Billion Weekly Downloads Hackers Hijacked 18 Very Popular npm Packages With 2 Billion Weekly Downloads Cyber Security News
New SHUYAL Attacking 19 Popular Browsers to Steal Login Credentials New SHUYAL Attacking 19 Popular Browsers to Steal Login Credentials Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Java Vulnerability Affects Palo Alto Products: Key Details
  • Debian Packages Retain Distrusted Certificates Despite Updates
  • WhatsApp Fixes Android Security Flaw Amid Scam Concerns
  • Microsoft Probes Attachment Upload Issues in New Outlook
  • Critical OpenSSL Vulnerability Discovered in Base64 Encoding

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Java Vulnerability Affects Palo Alto Products: Key Details
  • Debian Packages Retain Distrusted Certificates Despite Updates
  • WhatsApp Fixes Android Security Flaw Amid Scam Concerns
  • Microsoft Probes Attachment Upload Issues in New Outlook
  • Critical OpenSSL Vulnerability Discovered in Base64 Encoding

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark