Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Investigator Uncovers Crypto Network Tied to Lazarus Group

Investigator Uncovers Crypto Network Tied to Lazarus Group

Posted on October 5, 2026 By CWS

Investigator Uncovers Crypto Network Tied to Lazarus Group

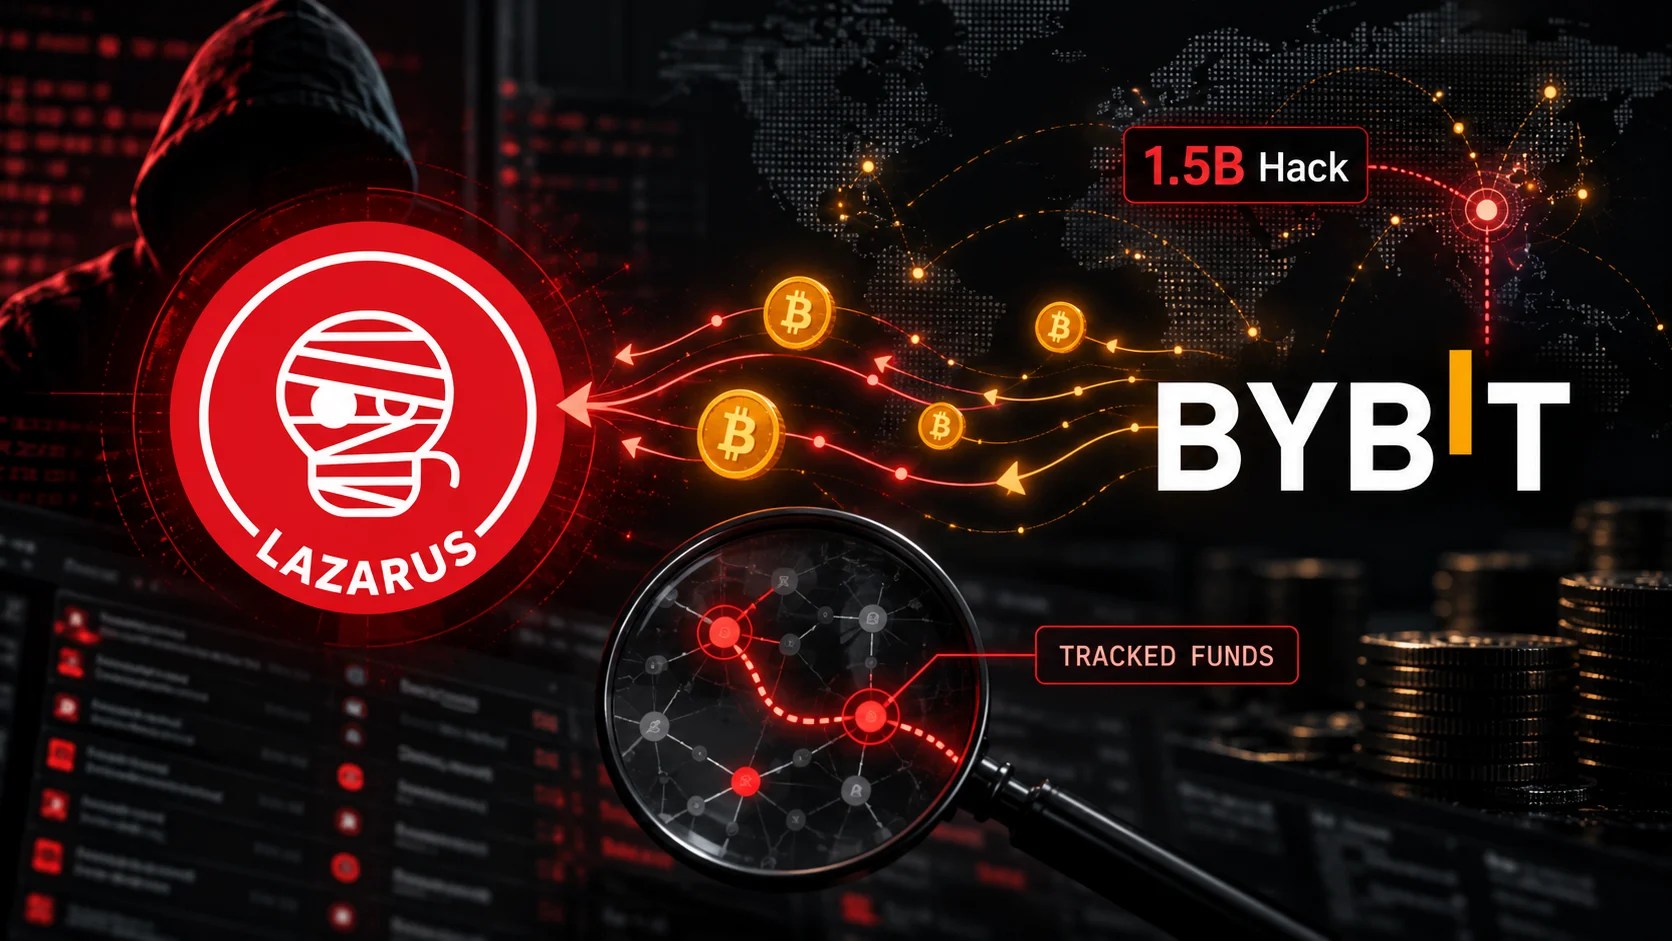
An independent blockchain investigator known as ZachXBT has successfully infiltrated a cryptocurrency laundering operation tied to the notorious Lazarus Group following the significant $1.5 billion hack on the Bybit exchange. His investigation sheds light on the methods used by hackers to circulate stolen assets.

Unveiling the Laundering Operations

Through a combination of private conversations and public blockchain data, ZachXBT claims to have traced over $1 billion in laundered funds across various hacks. Although this figure is his estimate, it highlights the vast scale of activities connected to these illicit networks. His findings have been instrumental in freezing stolen assets and exposing operators claiming ties to major thefts.

Infiltration Tactics and Findings

Posing as a potential client, ZachXBT entered Telegram and Discord groups where he identified more than 15 accounts linked to the Bybit hack. In March 2025, he created a new Ethereum wallet and strategically exchanged USDC for USDT, incurring minor losses to gain trust within the network. This infiltration allowed him to gather critical information from an operator known as “Jimmy Green,” who alleged that his team processed the majority of stolen assets from Hong Kong and mainland China.

Linking Chats to Blockchain Transactions

By matching the operator’s claims with blockchain records, ZachXBT demonstrated how Jimmy’s wallet received funds from an address associated with the Bybit theft. Further evidence was provided through screenshots that aligned with timing and amounts of THORChain transfers. This meticulous work enabled him to identify wallet clusters involving over $12 million in stolen funds and resulted in Tether freezing 442,000 USDT related to these activities.

The Federal Bureau of Investigation previously attributed the Bybit theft to North Korean entities, labeling the operation as TraderTraitor. Their advisory highlighted the dispersion of stolen assets across thousands of blockchain addresses, emphasizing the complexity of tracking these funds.

Implications and Future Outlook

ZachXBT’s efforts have reportedly led to the freezing of more than $75 million linked to North Korean cyber activities since 2022. Despite these successes, the recovery of stolen assets remains a challenging endeavor. The investigator’s work underscores the importance of patient undercover operations, detailed blockchain analysis, and prompt dissemination of information to prevent further movement of illicit funds. The case exemplifies how individual dedication can significantly impact the fight against cybercrime.
Cyber Security News Tags:blockchain investigation, Bybit hack, crypto laundering, crypto theft, Cybersecurity, Lazarus Group, North Korea, USDC, USDT, ZachXBT

Post navigation

Previous Post: 16 Arrested in Timor-Leste for Posing as Japanese Police
Next Post: AI Exploit in Zammad Exposes Critical Security Flaws

Related Posts

Cisco 0-Day RCE Secure Email Gateway Vulnerability Exploited in the Wild Cisco 0-Day RCE Secure Email Gateway Vulnerability Exploited in the Wild Cyber Security News
Rapid Response: Microsoft Defender Thwarts Ransomware in Seconds Rapid Response: Microsoft Defender Thwarts Ransomware in Seconds Cyber Security News
Hackers Exploit Qinglong RCE Vulnerabilities Hackers Exploit Qinglong RCE Vulnerabilities Cyber Security News
Yoma Fleet Enhances Cybersecurity with AccuKnox SIEM Yoma Fleet Enhances Cybersecurity with AccuKnox SIEM Cyber Security News
Threat Actors Turning Job Offers Into Traps, Over 4 Million Lost in 2024 Alone Threat Actors Turning Job Offers Into Traps, Over $264 Million Lost in 2024 Alone Cyber Security News
Global Outage Disrupts Microsoft Exchange Online Access Global Outage Disrupts Microsoft Exchange Online Access Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI Exploit in Zammad Exposes Critical Security Flaws
  • Investigator Uncovers Crypto Network Tied to Lazarus Group
  • 16 Arrested in Timor-Leste for Posing as Japanese Police
  • Critical Microsoft Exchange Vulnerability Patched
  • HEIC Image Vulnerability Leads to WordPress Security Risk

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI Exploit in Zammad Exposes Critical Security Flaws
  • Investigator Uncovers Crypto Network Tied to Lazarus Group
  • 16 Arrested in Timor-Leste for Posing as Japanese Police
  • Critical Microsoft Exchange Vulnerability Patched
  • HEIC Image Vulnerability Leads to WordPress Security Risk

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark