Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
New phpAfterShell Vulnerability Enables Remote Code Execution

New phpAfterShell Vulnerability Enables Remote Code Execution

Posted on November 19, 2026 By CWS

A recently discovered vulnerability, termed phpAfterShell, poses a significant risk of remote code execution on servers running certain PHP versions. This threat persists even on systems updated with the October patches addressing the PHP2Shell exploit.

Discovery and Technical Details

Depthfirst researchers revealed the phpAfterShell flaw on November 19, demonstrating its potential to exploit a separate PHP bug for remote code execution. Identified as CVE-2026-126714, this vulnerability has a high CVSS v4.0 score of 9.2, indicating its critical nature.

The issue lies in PHP’s default file-based session handler, which is responsible for maintaining user session data such as login status and shopping cart contents. With upload progress enabled, PHP can manipulate session files even while processing upload requests, risking the creation of corrupted session files.

Mechanism of Exploitation

When a session update is interrupted, PHP may leave a session file with both outdated and new data. This flawed file might be accepted as valid when the application calls session_start(), leading to potential deserialization issues. The October security updates did not address this particular scenario.

Depthfirst’s analysis shows that the phpAfterShell exploit circumvents the previous PHP2Shell restrictions by targeting session files outside the upload-progress phase, combined with a memory corruption flaw in PHP classes to achieve code execution.

Mitigation and Future Outlook

The phpAfterShell exploit executes code with the permissions of the PHP worker, potentially exposing sensitive server data. However, applications using Redis or databases for session storage are not affected by this flaw.

The recommended mitigation involves upgrading to PHP versions 8.2.36, 8.3.37, 8.4.28, or 8.5.13, as the October updates do not cover this vulnerability. For immediate protection, Depthfirst suggests disabling session.upload_progress in the php.ini configuration.

Organizations are encouraged to regularly monitor PHP advisory updates and apply necessary patches promptly to safeguard against emerging threats. As PHP 8.0 and 8.1 become unsupported, migrating to newer, supported versions is crucial for maintaining security.

Cyber Security News Tags:CVE-2026-126714, Cybersecurity, Depthfirst, Deserialization, PHP patches, PHP security, PHP vulnerability, phpAfterShell, remote code execution, session handler

Post navigation

Previous Post: New AI Threats and Cybersecurity Challenges Uncovered

Related Posts

ILSpy Site Hacked, Spreads Malware to Developers ILSpy Site Hacked, Spreads Malware to Developers Cyber Security News
AI-Powered NotC2 Framework Exploits AWS Services AI-Powered NotC2 Framework Exploits AWS Services Cyber Security News
OpenSSH Vulnerability Bypasses Authentication on Linux OpenSSH Vulnerability Bypasses Authentication on Linux Cyber Security News
Malware Exploits Google Passkey Vulnerabilities Malware Exploits Google Passkey Vulnerabilities Cyber Security News
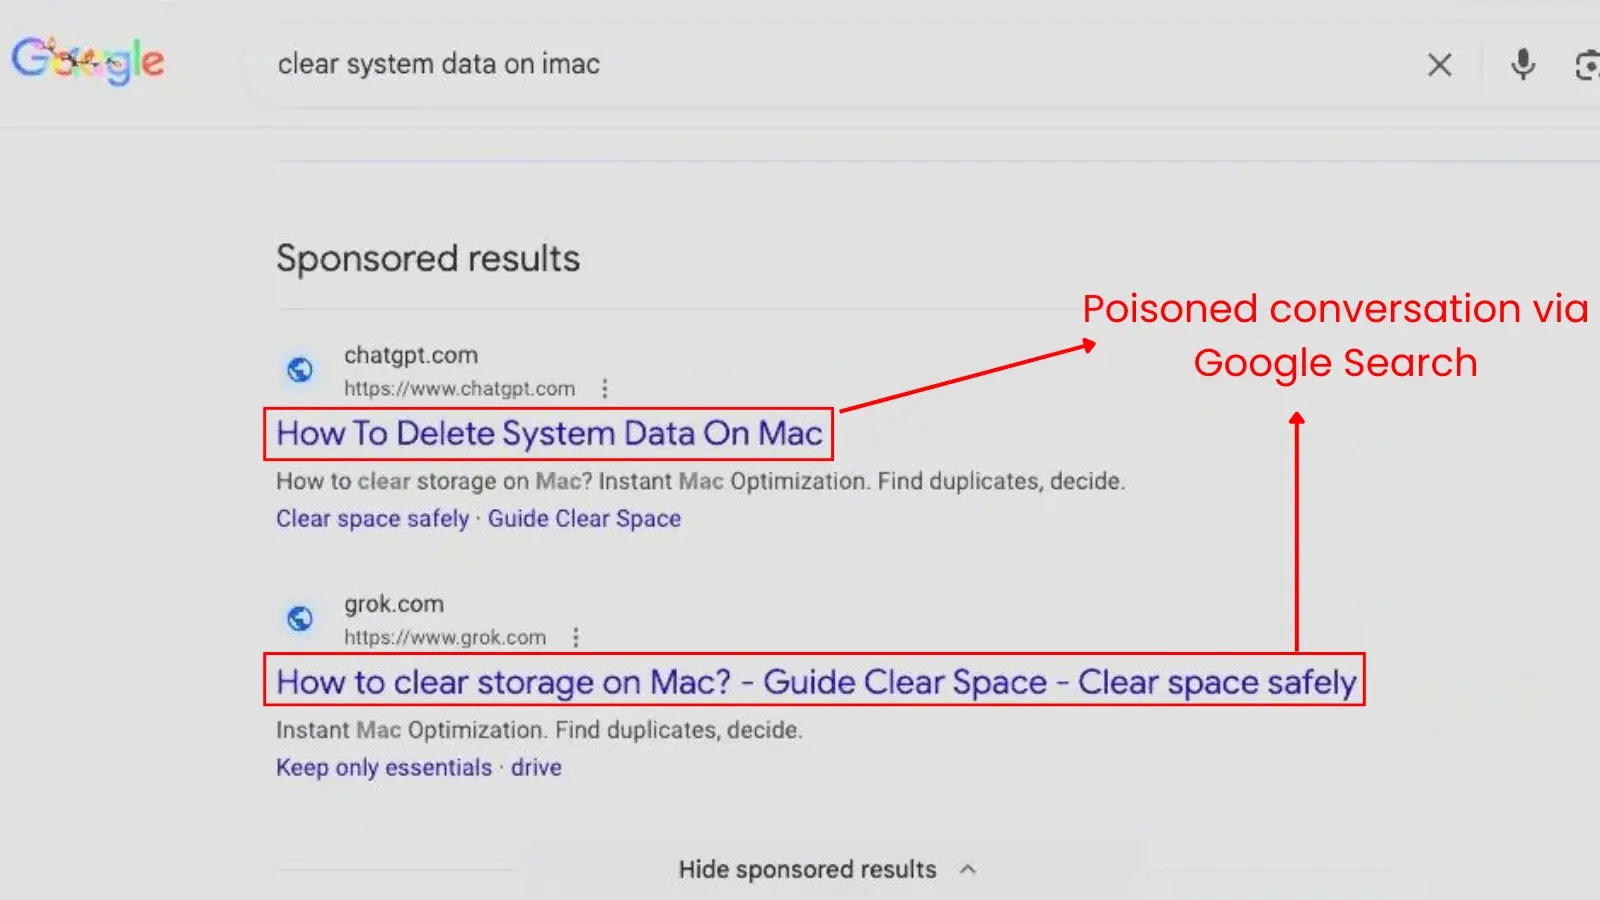
Threat Actors Weaponize ChatGPT and Grok Conversations to Deploy AMOS Stealer Threat Actors Weaponize ChatGPT and Grok Conversations to Deploy AMOS Stealer Cyber Security News
Top Managed File Transfer Solutions for 2026 Top Managed File Transfer Solutions for 2026 Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • New phpAfterShell Vulnerability Enables Remote Code Execution
  • New AI Threats and Cybersecurity Challenges Uncovered
  • Criminal IP’s New AI Tool Enhances Cybersecurity Exposure Management
  • VMware vCenter Zero-Day Exploited by Espionage Group
  • JPMorgan Chase Reports Third-Party Data Breach Incident

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • New phpAfterShell Vulnerability Enables Remote Code Execution
  • New AI Threats and Cybersecurity Challenges Uncovered
  • Criminal IP’s New AI Tool Enhances Cybersecurity Exposure Management
  • VMware vCenter Zero-Day Exploited by Espionage Group
  • JPMorgan Chase Reports Third-Party Data Breach Incident

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark