Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
AI-Powered NotC2 Framework Exploits AWS Services

AI-Powered NotC2 Framework Exploits AWS Services

Posted on November 9, 2026 By CWS

Varonis Threat Labs has developed a new proof-of-concept command-and-control (C2) framework named NotC2, which operates entirely using native AWS services. This innovative framework leverages Amazon Bedrock to convert plain English into cloud commands, representing a sophisticated method of service abuse rather than a flaw in Bedrock itself. Importantly, the framework can only be utilized after an attacker has obtained AWS credentials.

Innovative Use of AWS Services in C2 Framework

Traditional C2 frameworks rely on custom servers and protocols that can be detected and blocked by security tools. To circumvent these defenses, attackers have shifted to using recognized platforms like Telegram, Discord, and GitHub, which are essential to business operations, making them difficult to block. Cloud storage solutions such as Amazon S3 and Google Drive have similarly been used to carry commands and stolen data.

Researchers have shown that cloud-based C2 traffic often travels over port 443, rendering reputation-based blocking ineffective. The development of NotC2 builds on previous work, such as Dhiraj Mishra’s XRayC2, which disguises commands within AWS X-Ray trace annotations. Additionally, Rhino Security Labs demonstrated using S3 objects for Cobalt Strike beacons, though these methods have limitations like requiring API keys and experiencing delays due to constant polling.

Mechanics of the NotC2 Framework

According to Varonis Threat Labs’ research, NotC2, which stands for “notification” and “C2,” employs four AWS services, each playing a distinct role. Amazon SQS is used for command input, where the attacker’s server places messages in a queue, avoiding continuous connections that could be detected. AWS Lambda functions as the processing engine, executing tasks without leaving lasting processes, though logs of these activities remain in the cloud.

Amazon SNS handles result delivery, sending outputs to an attacker’s HTTPS endpoint without direct contact. Amazon Bedrock acts as the AI interpreter, transforming simple requests into complex AWS API calls. This allows attackers to execute cloud operations efficiently without knowing specific CLI syntax.

Defensive Measures and Future Implications

The NotC2 framework’s success hinges on the permissions associated with compromised credentials. Deploying this system requires specific AWS permissions, and attackers often use open-source tools like Pacu to identify exploitable paths. Real-world incidents show attackers leveraging stolen credentials to run up costs on cloud services or targeting AI gateways linked to Amazon Bedrock.

Defensive strategies should focus on monitoring for unusual cloud activities, such as external SNS subscriptions created by a Lambda role or a sudden increase in specific Bedrock API calls. Implementing least privilege access controls, restricting SNS subscriptions, and monitoring cloud logs for anomalies are critical steps in mitigating these threats.

Overall, NotC2 illustrates the challenges of maintaining security in serverless environments where traditional perimeter defenses are ineffective. Security teams must prioritize securing workload identities and monitoring service interactions to disrupt the NotC2 chain effectively.
Cyber Security News Tags:AI-powered C2, Amazon Bedrock, AWS security, AWS services, cloud commands, cloud security, Cybersecurity, network defense, serverless security, Varonis Threat Labs

Post navigation

Previous Post: CISA Highlights SonicOS SSLVPN Security Weakness

Related Posts

Data-Leak Sites Hit an All-Time High With New Scattered Spider RaaS and LockBit 5.0 Data-Leak Sites Hit an All-Time High With New Scattered Spider RaaS and LockBit 5.0 Cyber Security News
Google Fixes 200+ Android Security Flaws, Including Zero-Click Risks Google Fixes 200+ Android Security Flaws, Including Zero-Click Risks Cyber Security News
FBI Unveils IOCs for Cyber Attacks Targeting Salesforce Instances for Data Exfiltration FBI Unveils IOCs for Cyber Attacks Targeting Salesforce Instances for Data Exfiltration Cyber Security News
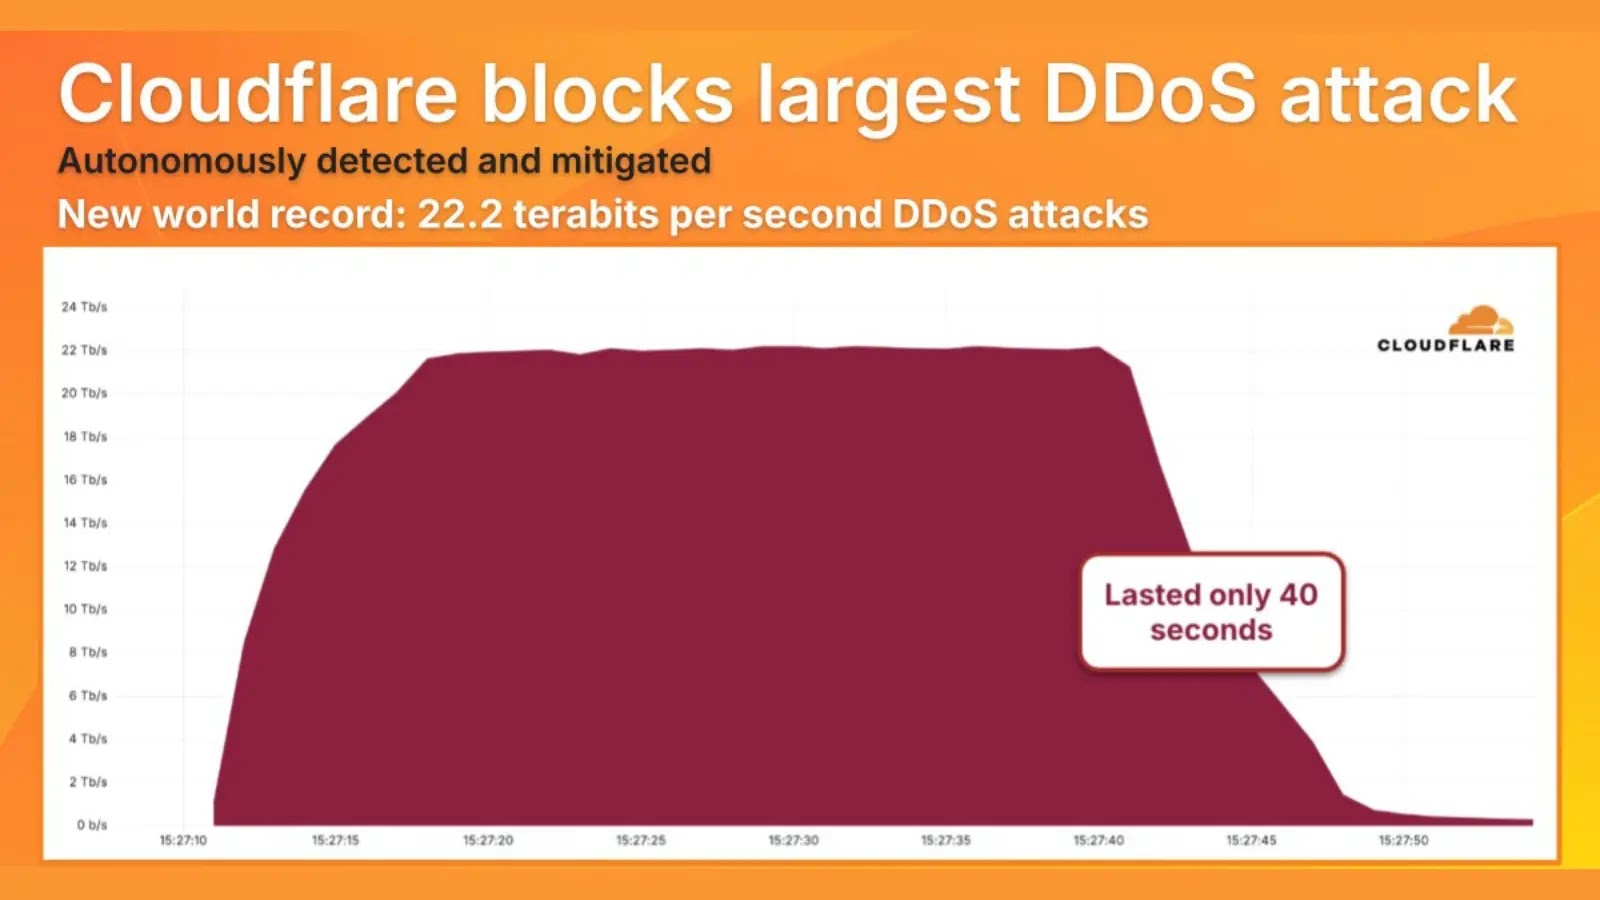
22.2 Tbps DDoS Attack Breaks Internet With New World Record 22.2 Tbps DDoS Attack Breaks Internet With New World Record Cyber Security News
Amazon Catches North Korean IT Worker by Tracking Tiny 110ms Keystroke Delays Amazon Catches North Korean IT Worker by Tracking Tiny 110ms Keystroke Delays Cyber Security News
Malware Operators Collaborate With Covert North Korean IT Workers to Attack Corporate Organizations Malware Operators Collaborate With Covert North Korean IT Workers to Attack Corporate Organizations Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI-Powered NotC2 Framework Exploits AWS Services
  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI-Powered NotC2 Framework Exploits AWS Services
  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark