Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Apple Enhances macOS Disk Access Amid AI Concerns

Apple Enhances macOS Disk Access Amid AI Concerns

Posted on October 5, 2026 By CWS

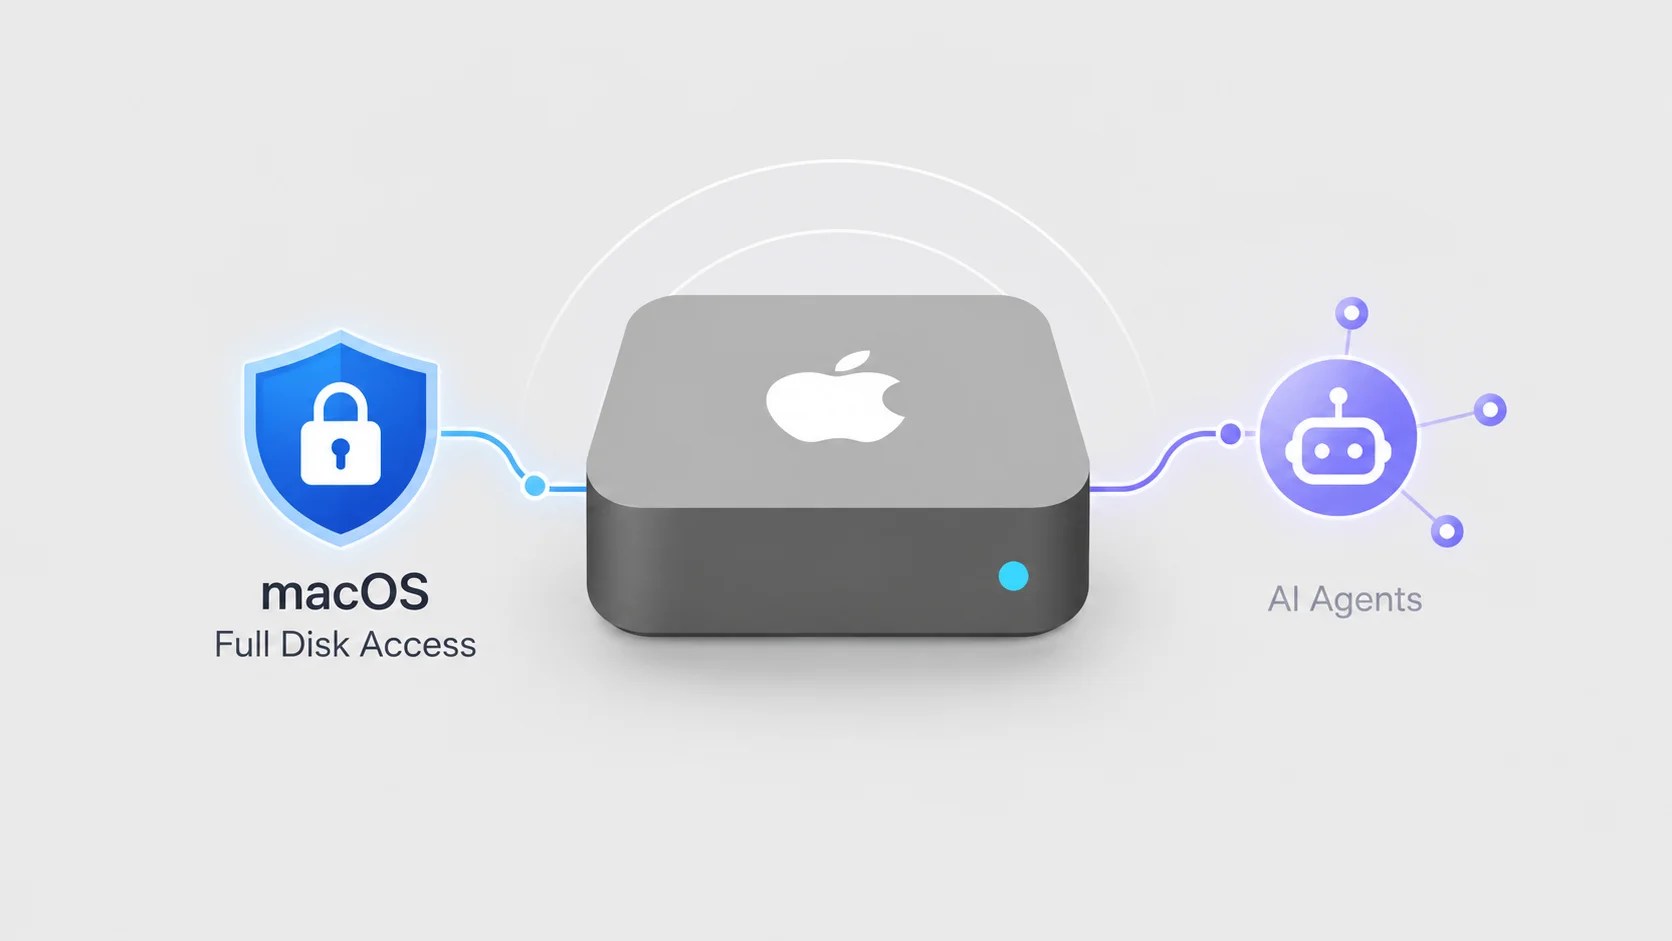
Apple is set to implement stricter regulations on macOS Full Disk Access permissions due to the rising capabilities of AI agents. The tech giant has expressed concerns that these permissions could potentially expose users’ sensitive information, prompting a need for more deliberate user actions before granting such access.

Understanding Full Disk Access

Initially, Full Disk Access was designed to support reliable Mac utilities, like backup programs, to bypass standard privacy restrictions when necessary. This permission allows apps to access files across the Mac, including data from Mail, Messages, Safari, and other critical system settings.

Apple’s existing protocols already view Full Disk Access as a high-risk feature, requiring manual user intervention through the macOS Privacy & Security settings. Despite this, some developers have been using these permissions in ways that might leave users unaware of the extent of data visibility.

AI Agents and Increased Privacy Risks

The proliferation of AI agents has intensified the potential risks associated with Full Disk Access. Unlike typical applications with singular functions, AI agents can gather and process information from multiple sources, potentially granting them expansive insights into personal and business data.

This broad access could expose sensitive information, such as emails, private messages, and browsing histories, not only of the users but also involving other parties in communication exchanges. As AI tools evolve, the associated risks are expected to escalate significantly.

Future Outlook and User Recommendations

While Apple has not disclosed the specific design or release timeline for these enhanced controls, its direction indicates a move towards a more transparent permission process. The aim is to ensure users fully comprehend the extent of data access before enabling Full Disk Access permissions.

For Mac users, a proactive step involves reviewing the current applications with Full Disk Access permissions. This can be done by navigating to System Settings, selecting Privacy & Security, and then Full Disk Access. It is advisable to revoke permissions for applications that are obsolete or lack a justified need for extensive data access.

The planned update by Apple comes amidst broader concerns about vulnerabilities in macOS Transparency, Consent, and Control (TCC) protections. Recent reports have highlighted potential bypasses and the increasing danger of AI-driven ransomware attacks. Apple’s initiative underscores the necessity of robust permission frameworks as AI technology continues to integrate deeper into user devices.
Cyber Security News Tags:AI agents, Apple, Cybersecurity, data security, Full Disk Access, macOS, permission controls, Privacy, TCC protections, technology news

Post navigation

Previous Post: GlassWorm Exploits VS Code Themes in Supply Chain Attack
Next Post: Trump Mobile Data Breach Exposes Thousands of Records

Related Posts

Unremovable Spyware on Samsung Devices Comes Pre-installed on Galaxy Series Devices Unremovable Spyware on Samsung Devices Comes Pre-installed on Galaxy Series Devices Cyber Security News
AWS Middle East Outage Disrupts EC2 and Networking Services AWS Middle East Outage Disrupts EC2 and Networking Services Cyber Security News
WhatsApp Users Targeted by Spyware in Italy WhatsApp Users Targeted by Spyware in Italy Cyber Security News
Hackers Use Zoho WorkDrive to Distribute LOTUSLITE V2 Hackers Use Zoho WorkDrive to Distribute LOTUSLITE V2 Cyber Security News
Cybersecurity Awareness 2026: Strengthening Digital Habits Cybersecurity Awareness 2026: Strengthening Digital Habits Cyber Security News
APT Hackers Attacking Indian Government Using GOGITTER tool and GITSHELLPAD Malware APT Hackers Attacking Indian Government Using GOGITTER tool and GITSHELLPAD Malware Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Java Vulnerability Affects Palo Alto Products: Key Details
  • Debian Packages Retain Distrusted Certificates Despite Updates
  • WhatsApp Fixes Android Security Flaw Amid Scam Concerns
  • Microsoft Probes Attachment Upload Issues in New Outlook
  • Critical OpenSSL Vulnerability Discovered in Base64 Encoding

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Java Vulnerability Affects Palo Alto Products: Key Details
  • Debian Packages Retain Distrusted Certificates Despite Updates
  • WhatsApp Fixes Android Security Flaw Amid Scam Concerns
  • Microsoft Probes Attachment Upload Issues in New Outlook
  • Critical OpenSSL Vulnerability Discovered in Base64 Encoding

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark