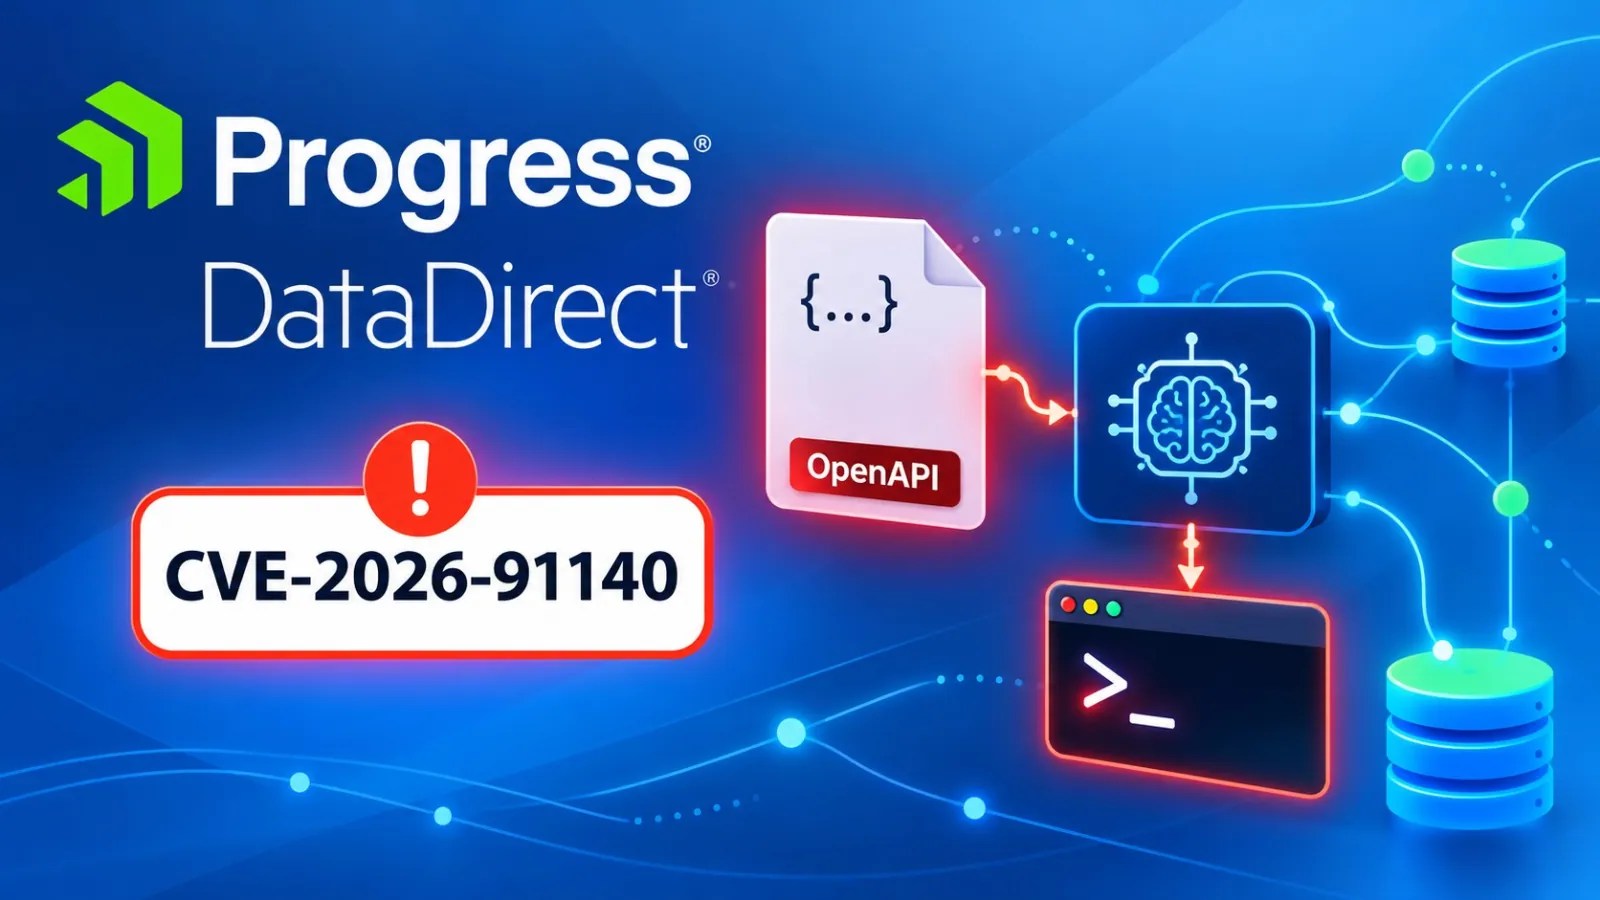
Progress has announced a critical security vulnerability identified as CVE-2026-91140 in its DataDirect Autonomous REST Connector AI Model Generator. This flaw allows malicious OpenAPI or Swagger files to execute arbitrary operating system commands.
Details of the Vulnerability
On October 6, 2026, Progress released a security bulletin detailing the vulnerability, which affects Early Access agent definitions available via the public progress/datadirect-arc-ai-model-gen GitHub repository. It is crucial for users to update these definitions before using the agents again.
The flaw stems from a filename value extracted from OpenAPI or Swagger documents, which is utilized in shell operations without adequate validation or quoting. This oversight can permit specially crafted input to alter shell command interpretations, leading to execution of attacker-controlled commands.
Impact and Mitigation Measures
The vulnerability primarily exploits shell-based temporary-file cleanup instructions, creating potential attack vectors within developer workspaces or continuous integration environments. Progress emphasizes that the malicious input does not need to be a standalone executable, but rather an API specification that becomes hazardous when processed by the affected agent.
Notably, the flaw does not trigger a specific error message, making detection challenging without careful monitoring. Developers might observe unexpected files or commands as a sign of exploitation.
Recommended Actions for Users
Progress has identified three agent and prompt definitions affected by this vulnerability: ARCGenAI-Generator.agent.md version 2.0, ARCGenAI-Generator.prompt.md version 1.0, and ARCGenAI-EntityGen.agent.md version 1.0. The company has released updated versions 2.1 for all definitions, and users are advised to obtain these from the repository immediately.
Customers who have previously processed untrusted OpenAPI or Swagger documents with the vulnerable definitions should thoroughly review their workspaces or CI environments for unexpected changes. This proactive review is crucial even after updating the definitions, as it addresses environments where potentially harmful documents might have already been executed.
For further assistance, customers are encouraged to contact Progress Technical Support. Implementing these updates and reviews can significantly mitigate the risks posed by this critical flaw.