Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
SkyW4lker Phishing Scheme Targets U.S. Microsoft 365 Accounts

SkyW4lker Phishing Scheme Targets U.S. Microsoft 365 Accounts

Posted on November 4, 2026 By CWS

A sophisticated phishing campaign known as SkyW4lker is increasingly targeting Microsoft 365 accounts, with a significant focus on U.S. enterprises. Unlike traditional phishing tactics, SkyW4lker bypasses password theft and MFA by manipulating users into approving legitimate device-code sign-ins, granting attackers access to corporate accounts.

SkyW4lker’s Approach to Phishing

SkyW4lker, active since June 2026, leverages Microsoft’s OAuth 2.0 device-code flow, tricking users into entering codes on genuine login pages. This grants attackers access tokens without revealing passwords. The ongoing threat has been tracked by ANY.RUN, revealing a rapid increase in activity, particularly in the United States, which accounts for nearly half of the campaign’s submissions.

Impact on U.S. Enterprises

U.S. companies, especially those in technology, manufacturing, and government sectors, are heavily targeted. These sectors rely on Microsoft 365 for collaboration, making them vulnerable to data breaches. The structural risk lies in users completing MFA sign-ins on attackers’ behalf, allowing unauthorized access to various Microsoft applications.

Technical Breakdown and Countermeasures

SkyW4lker employs CAPTCHAs, obfuscated JavaScript, and trusted platforms like Google Sites to evade detection. Its connection to the Gabagool phishing kit suggests a shared origin, complicating defense efforts. To combat this, security teams must tighten device-code authentication, integrate email and identity monitoring, and utilize interactive sandboxes for threat analysis.

In conclusion, SkyW4lker’s exploitation of Microsoft’s features underscores the need for comprehensive security measures. By restricting unnecessary device-code authentication and enhancing threat visibility, enterprises can mitigate the risks posed by such advanced phishing schemes.
Cyber Security News Tags:ANY.RUN, cyber threats, Cybersecurity, device code phishing, identity threat, MFA, Microsoft 365, OAuth 2.0, Phishing, phishing protection, Security, Skyw4lker, US enterprises

Post navigation

Previous Post: Prompt Adware Found in OpenAI Codex Jailbreak

Related Posts

Nessus Windows Vulnerabilities Allow Overwrite of Arbitrary Local System Files Nessus Windows Vulnerabilities Allow Overwrite of Arbitrary Local System Files Cyber Security News
Hackers Exploit Notepad++ Plugins for Silent System Breach Hackers Exploit Notepad++ Plugins for Silent System Breach Cyber Security News
Malware Detected in Hugging Face Repository with 200k Downloads Malware Detected in Hugging Face Repository with 200k Downloads Cyber Security News
Massive “Shai-Halud” Supply Chain Attack Compromised 477 NPM Packages Massive “Shai-Halud” Supply Chain Attack Compromised 477 NPM Packages Cyber Security News
Want To Detect Incidents Before It’s Too Late? You Need Threat Intelligence Want To Detect Incidents Before It’s Too Late? You Need Threat Intelligence Cyber Security News
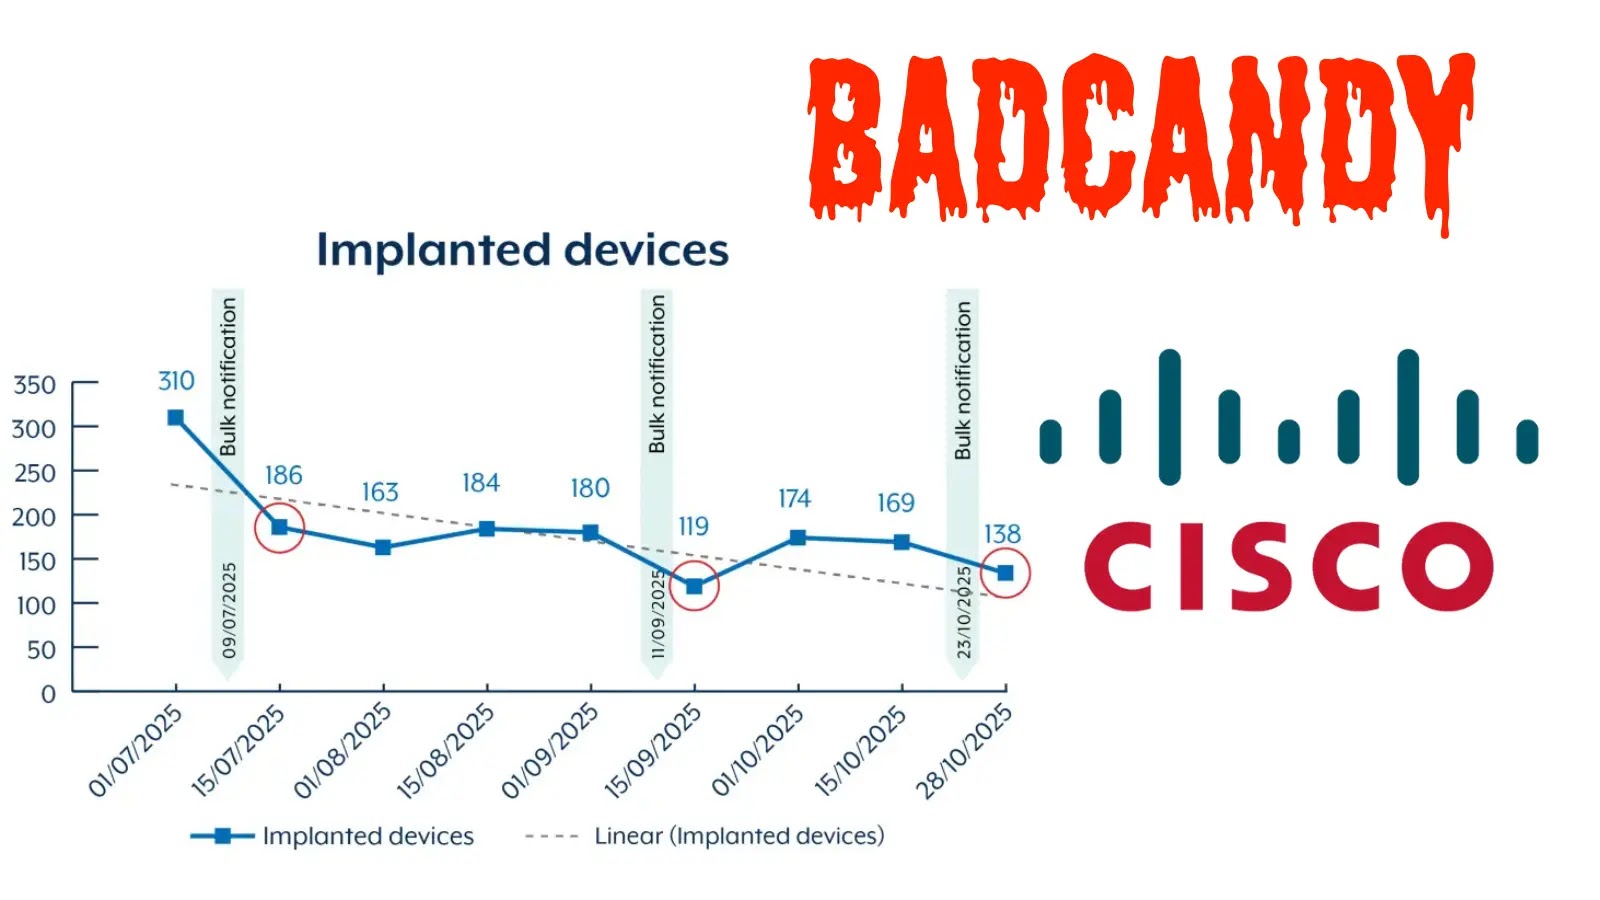
Hackers Exploiting Cisco IOS XE Vulnerability in the Wild to Deploy BADCANDY Web Shell Hackers Exploiting Cisco IOS XE Vulnerability in the Wild to Deploy BADCANDY Web Shell Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • SkyW4lker Phishing Scheme Targets U.S. Microsoft 365 Accounts
  • Prompt Adware Found in OpenAI Codex Jailbreak
  • APT Vulnerability in Debian and Ubuntu Risks Root Code Execution
  • Binance Hack: Details Emerge on $6 Billion Heist
  • SonicWall Declines Patching GMS Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • SkyW4lker Phishing Scheme Targets U.S. Microsoft 365 Accounts
  • Prompt Adware Found in OpenAI Codex Jailbreak
  • APT Vulnerability in Debian and Ubuntu Risks Root Code Execution
  • Binance Hack: Details Emerge on $6 Billion Heist
  • SonicWall Declines Patching GMS Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark