Security operations centers (SOCs) are under increasing pressure to manage complex threats efficiently while working within budgetary and staffing limitations. As 2027 approaches, the landscape of cybersecurity challenges continues to evolve, demanding more sophisticated detection and investigation strategies from security teams.
Threat intelligence is set to play a pivotal role in helping SOCs and Managed Security Service Providers (MSSPs) identify malicious activities earlier, streamline suspicious behavior investigations, and optimize analyst expertise. Incorporating intelligence into daily security processes is crucial for enhancing effectiveness from initial detection to response.
Detecting Threats Before They Escalate
One major challenge SOCs face is the need to identify threats before they become full-fledged incidents. Recognizing already identified malicious activities elsewhere can significantly enhance detection. Without relevant intelligence, organizations might waste resources on investigations that automated systems could flag.
Research by ANY.RUN shows that 30% of unique malicious indicators of compromise (IOCs) found in sandbox investigations had previously been included in threat intelligence feeds. This presents an opportunity for SOCs and MSSPs to detect known malicious activities sooner, reducing investigative workloads.
Integrating threat intelligence feeds into security systems can help organizations detect attacks in real-time and allocate analyst resources more strategically. By continuously updating intelligence workflows, SOCs can focus manual investigations on activities requiring deeper analysis.
Prioritizing Threats Efficiently
Another critical challenge is efficiently prioritizing threats without spending excessive time on research. The sheer volume of alerts can be overwhelming, and understanding the significance of each alert is crucial for risk assessment. Analysts need comprehensive information about the history and broader context of suspicious indicators.
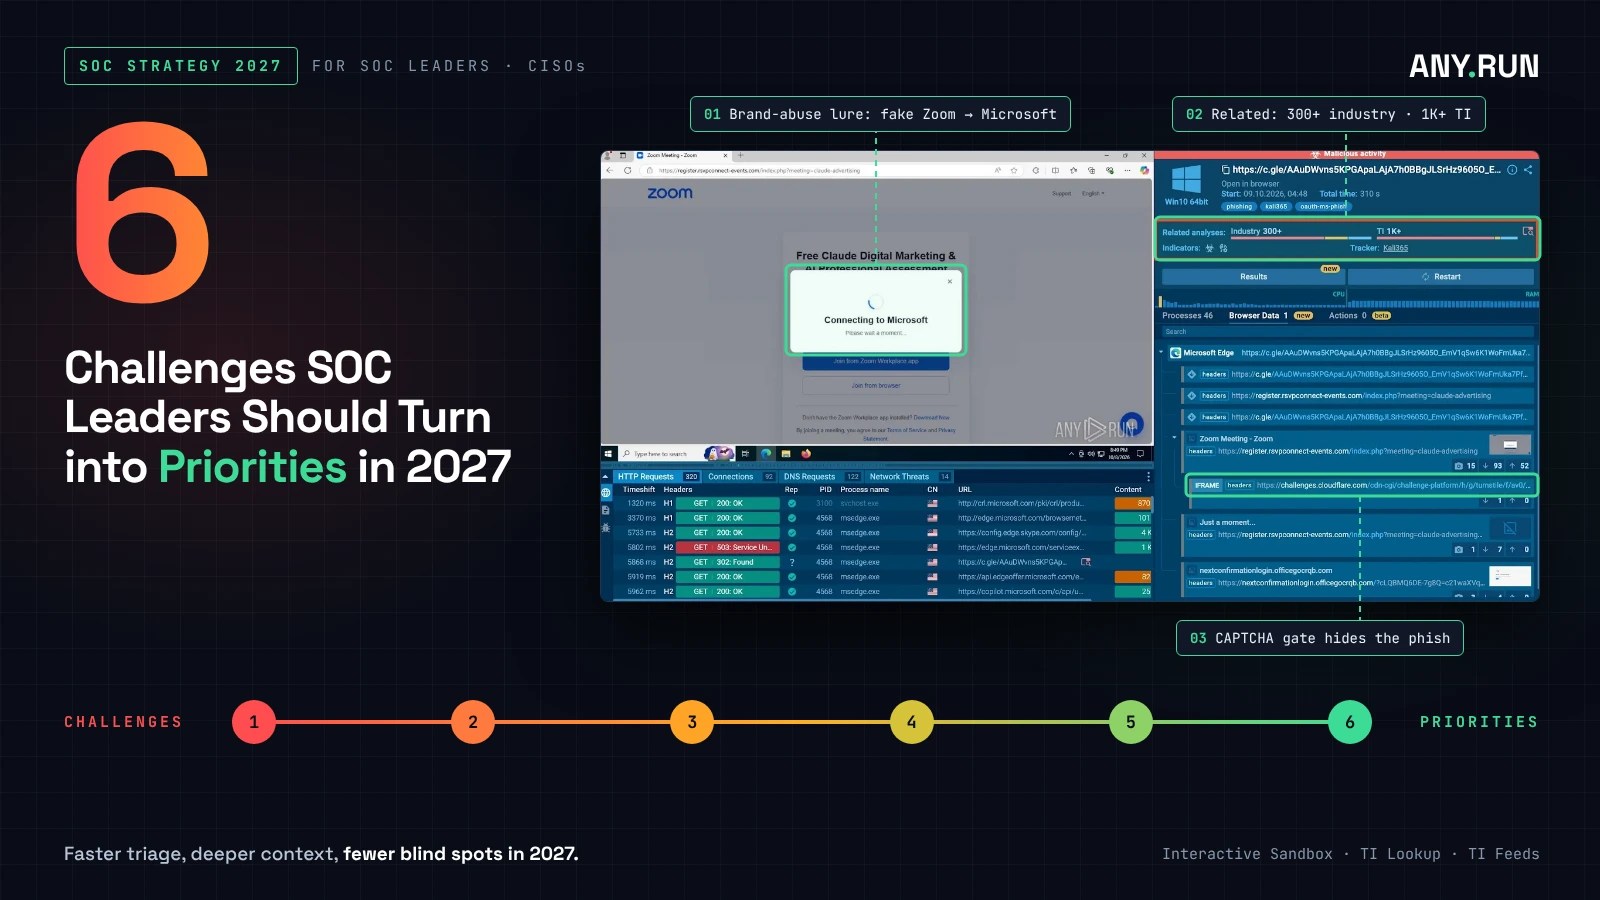
ANY.RUN’s Threat Intelligence Lookup and TI Reports provide valuable insights into campaigns, infrastructure, techniques, and behaviors associated with alerts. These tools allow analysts to establish the significance of suspicious activities swiftly and prioritize their investigations based on stronger evidence.
Connecting behavioral analysis with related threat intelligence helps SOCs and MSSPs identify unnoticed relationships and make informed escalation decisions, ultimately improving resource allocation and investigative efficiency.
Overcoming Investigation Bottlenecks
SOCs often face bottlenecks when suspicious files or URLs require manual investigation, which can delay the entire security operation. The faster the initial analysis, the more cases a team can handle within existing staffing levels.
ANY.RUN Interactive Sandbox provides rapid analysis with virtual machines starting in under 10 seconds and Tier 1 reports available in approximately 40 seconds. These reports include AI-generated summaries and actionable recommendations, expediting the investigative process.
By reducing the time from suspicious artifact to behavioral evidence, SOCs can increase their capacity to handle cases and make timely decisions based on readily available evidence. This approach also allows analysts to build on previous findings, enhancing threat detection and reducing duplicated efforts.
Conclusion: Advancing SOC Efficiency in 2027
The interconnected challenges of 2027 require SOCs to focus on early threat detection, prioritize efficiently, and streamline investigation processes. By integrating validated intelligence into existing systems, organizations can achieve repeatable improvements across security operations.
The effectiveness of SOCs in 2027 will be determined by their ability to maximize security value from existing resources, detect threats earlier, accelerate investigations, and transform intelligence into lasting security enhancements.