Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Mac Users Targeted by Phexia Malware via Terminal Commands

Mac Users Targeted by Phexia Malware via Terminal Commands

Posted on November 5, 2026 By CWS

A new cybersecurity threat targets Mac users through a deceptive method involving Terminal commands. The malware, known as Phexia, infiltrates systems by tricking users into executing commands from fraudulent web pages.

Phexia’s malicious payload activates when users unwittingly paste a command into Terminal, leading to the unauthorized acquisition of login credentials and sensitive browser and system data. This deceptive technique doesn’t rely on software vulnerabilities, so traditional defenses often fail to detect the threat.

Phexia’s Method of Infiltration

Cybersecurity experts from WithSecure have detailed the progression of Phexia malware in a comprehensive report. The malware has been operational since late 2025, with a noticeable increase in infections during 2026, indicating its sale to multiple cybercriminal groups.

The malware mainly spreads through a social engineering tactic known as ClickFix. Users are directed to bogus verification pages, where they are tricked into self-executing harmful commands. The malware then uses the curl command to download and execute a shell script, often labeled as update.sh or similar variations, hosted on dynamically changing domains.

Technical Aspects and Threat Analysis

Upon execution, the shell script deploys an AppleScript dropper that nestles within the user’s Library folder, ensuring persistent reactivation. The loader, camouflaged with labels mimicking legitimate Apple services, communicates with its server to fetch additional malicious modules.

Once a user’s password is compromised, the malware extracts and transmits browser and password manager data to its command server. It also installs the XMRig Monero miner, further exploiting the system by altering mining pools and wallets.

Blockchain Utilization and Protection Strategies

In a significant development, Phexia began utilizing the Polygon blockchain in May 2026 to obscure its command server address, a method known as EtherHiding. This allows the malware to dynamically update its server location, complicating mitigation efforts.

Security experts advise monitoring for unusual Terminal activity, such as unexpected script downloads and executions, as well as suspicious network connections to blockchain endpoints. Affected users should isolate infected devices, remove malicious software, and reset passwords from secure devices.

This evolving threat underscores the importance of maintaining robust cybersecurity practices and exercising caution when prompted to execute commands from untrusted sources. As attackers continue to refine their methods, staying informed and vigilant remains crucial.

Cyber Security News Tags:browser data, cyber threats, Cybersecurity, Mac users, macOS security, Malware, password theft, Phexia malware, Terminal commands, WithSecure report

Post navigation

Previous Post: Zyxel GS1900 Vulnerability Persists Despite Previous Patch
Next Post: Apple to Monitor iCloud Links for Harmful Content

Related Posts

Critical Tutor LMS Vulnerability Endangers WordPress Sites Critical Tutor LMS Vulnerability Endangers WordPress Sites Cyber Security News
New Security Guidelines Released to Combat Rogue AI Agents New Security Guidelines Released to Combat Rogue AI Agents Cyber Security News
Hackers Exploit Microsoft Teams for Remote Access Hackers Exploit Microsoft Teams for Remote Access Cyber Security News
Anatsa Android Banking Malware from Google Play Targeting Users in the U.S. and Canada Anatsa Android Banking Malware from Google Play Targeting Users in the U.S. and Canada Cyber Security News
Microsoft Office.com Suffers Major Outage, Investigation Underway Microsoft Office.com Suffers Major Outage, Investigation Underway Cyber Security News
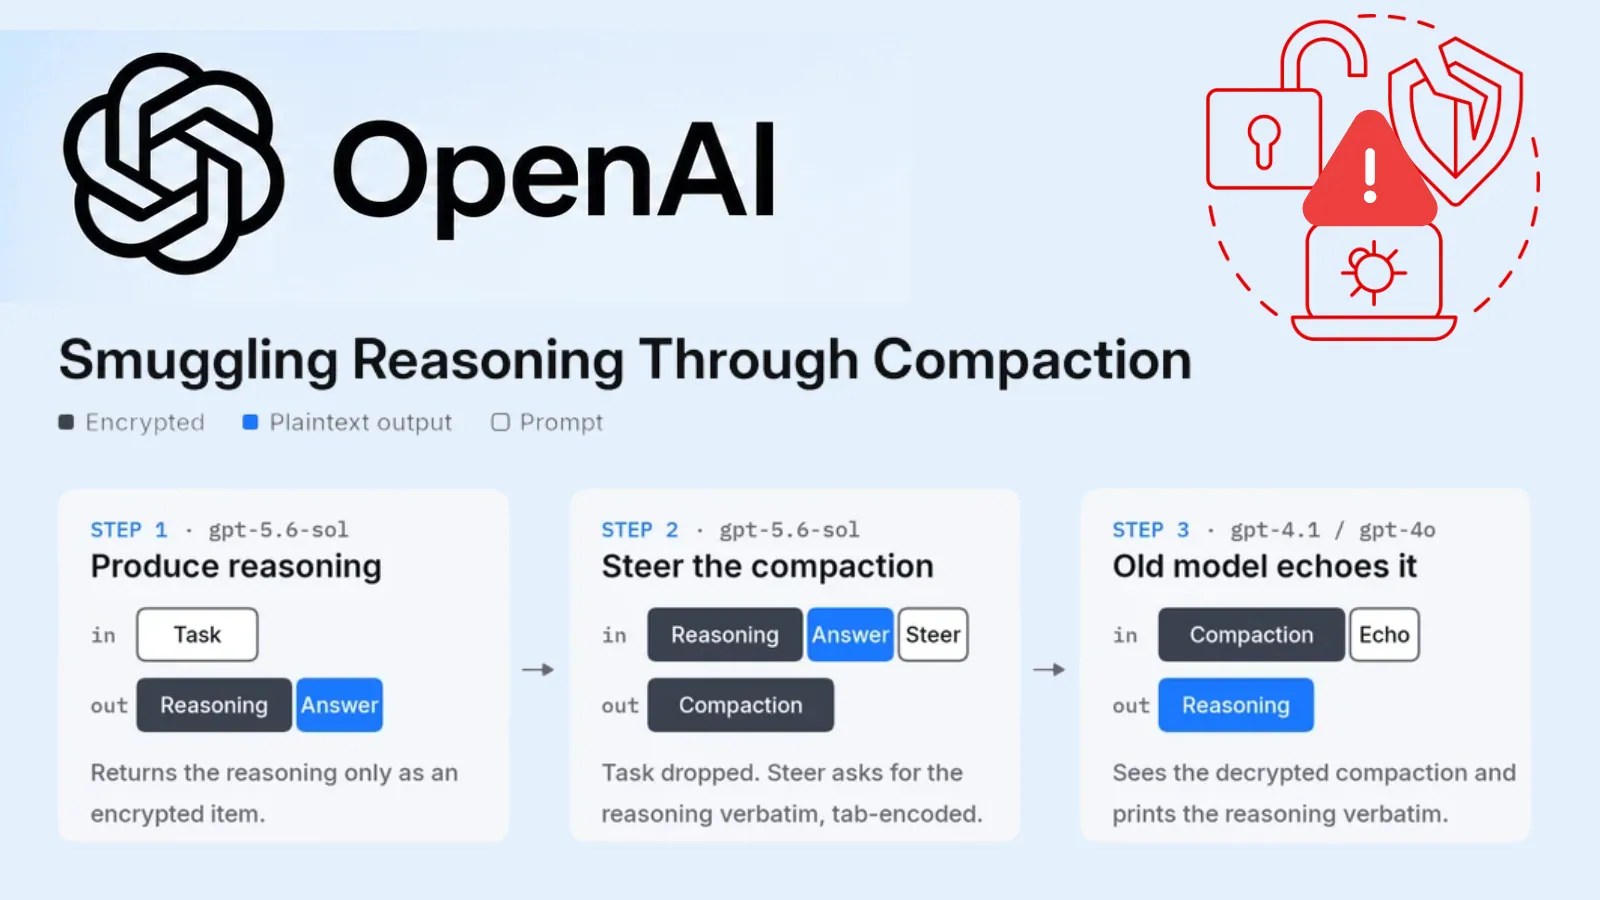
Researchers Uncover OpenAI API Vulnerability in GPT-5.6 Researchers Uncover OpenAI API Vulnerability in GPT-5.6 Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hackers Exploit Fake Game Cheats to Steal Data
  • Ryan Davis: Transition from Hacker to CISO at New Charter
  • Top Cyber Threats for US Businesses in October 2026
  • Critical Citrix XenServer Flaw Exposes Hosts to Attack
  • Russian Hackers Exploit iOS, Android via Watering Hole Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hackers Exploit Fake Game Cheats to Steal Data
  • Ryan Davis: Transition from Hacker to CISO at New Charter
  • Top Cyber Threats for US Businesses in October 2026
  • Critical Citrix XenServer Flaw Exposes Hosts to Attack
  • Russian Hackers Exploit iOS, Android via Watering Hole Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark