Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Chrome Vulnerability Fixed by Google

Critical Chrome Vulnerability Fixed by Google

Posted on November 10, 2026 By CWS

Google has recently addressed a significant security flaw in its Chrome browser, identified as CVE-2026-125350. This zero-day vulnerability has been actively exploited, allowing attackers to execute malicious code remotely. Users are urged to update their browsers promptly to safeguard against potential threats.

Details of the Chrome Security Update

The latest update, which elevates Chrome to version 157.0.8103.50/.51 for Windows and Mac users, and 157.0.8103.50 for Linux, will gradually be available to users over the next few weeks. Google’s security team keeps specific bug details confidential until the majority of users have implemented the update, ensuring widespread protection.

The flaw in question is a high-severity use-after-free vulnerability in the browser’s XML component. Notably, this vulnerability was reported by an anonymous researcher on November 6, 2026, just three days before Google released the patch.

Additional Vulnerabilities Addressed

Alongside CVE-2026-125350, Google’s latest Chrome update fixes eight additional security vulnerabilities. Seven of these are also rated as High severity. Noteworthy issues include an uninitialized resource in WebGL (CVE-2026-125345), incorrect authorization in the FileSystem (CVE-2026-125347), and a buffer overflow in Compositing (CVE-2026-125343).

Another vulnerability, CVE-2026-125346, a second use-after-free flaw in XML, was reported by Arni Hardarson of Neonix Security. Two Medium severity flaws were also addressed, both involving uninitialized resources in the GPU, with one reported by Vo Duc Thang.

Security Implications and User Recommendations

Browsers frequently process untrusted content, making memory vulnerabilities a prime target for attackers. Exploits like these can be distributed through phishing emails, malicious advertisements, or compromised websites, requiring only a simple click from potential victims.

This recent fix follows a pattern seen with previous Chrome updates, such as the June zero-day patch, which also permitted remote code execution. The new patch is available to enterprise users as well, with the Extended Stable channel receiving the update in version 156.0.8078.96.

Google employs advanced tools like AddressSanitizer and MemorySanitizer to catch security bugs before they reach users. However, the emergence of zero-day vulnerabilities underscores the importance of timely updates. Users can ensure their browser is updated by navigating to Help, selecting About Google Chrome, and clicking Relaunch after updates download in the background. Linux users should utilize their package manager for updates. Users of Chromium-based browsers should also watch for vendor-specific patches due to shared engine code.

Cyber Security News Tags:browser security, Chrome patch, CVE-2026-125350, Cybersecurity, Google Chrome, remote code execution, security update, software update, Vulnerability, zero-day

Post navigation

Previous Post: Terminal2Shell: Satirical ‘Zero-Day’ Misleads on Security
Next Post: Google Releases Critical Chrome Security Updates

Related Posts

ROMULUS Platform Facilitates Malicious Software Attacks ROMULUS Platform Facilitates Malicious Software Attacks Cyber Security News
Quantum Threats Preparing Your Encryption Strategy Quantum Threats Preparing Your Encryption Strategy Cyber Security News
Google Chrome Enhances Security with Device-Bound Credentials Google Chrome Enhances Security with Device-Bound Credentials Cyber Security News
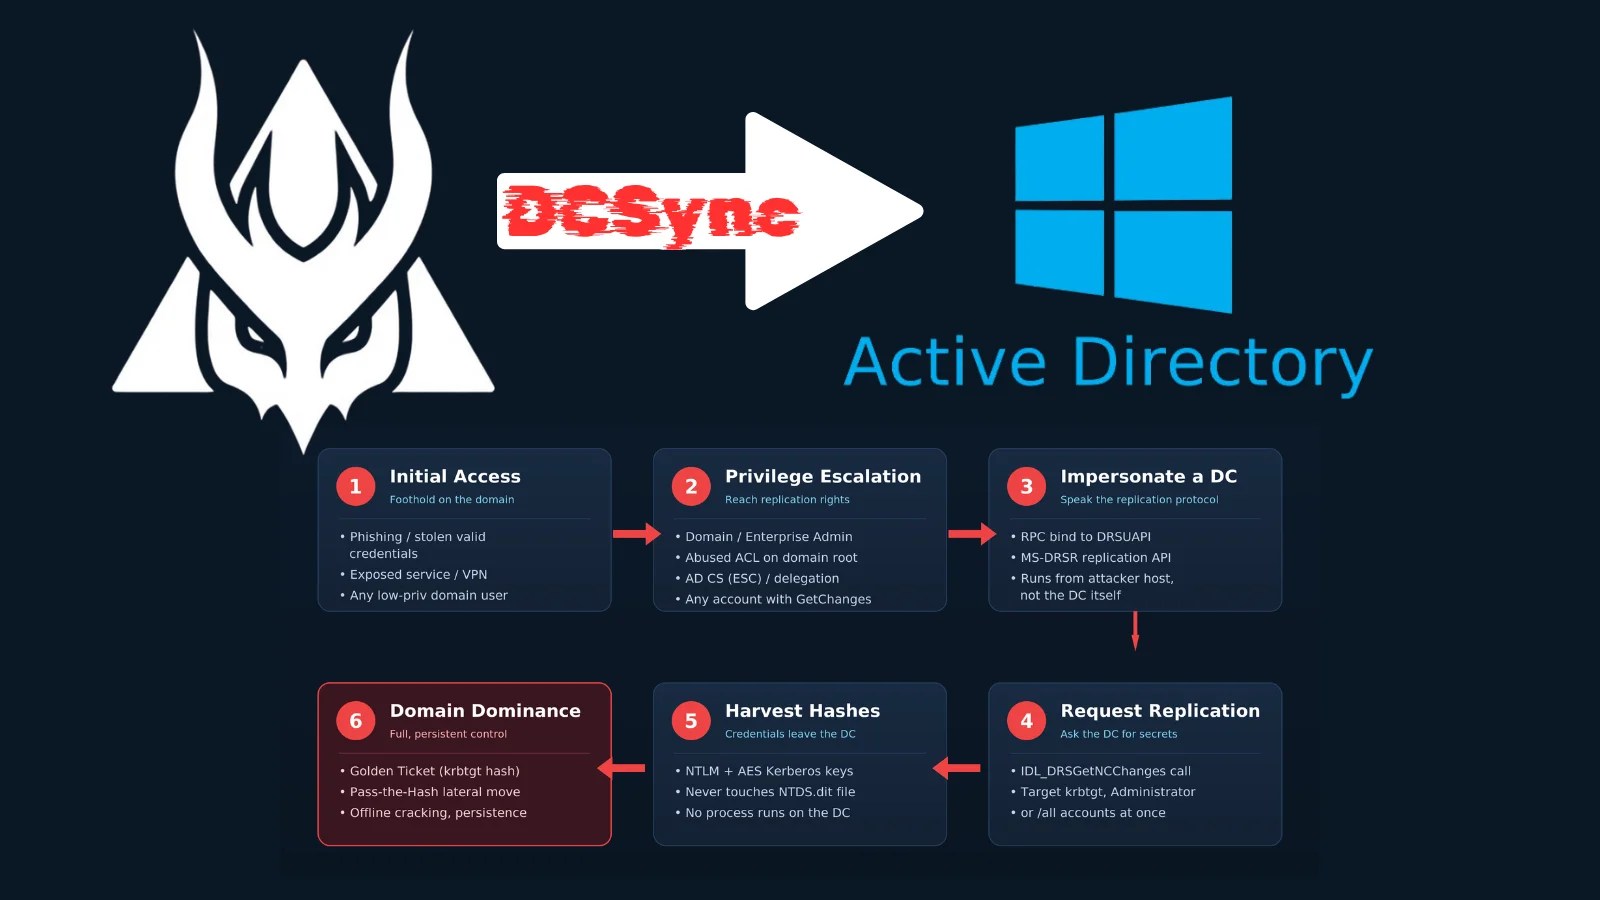
Qilin Ransomware Exploits Active Directory with DCSync Qilin Ransomware Exploits Active Directory with DCSync Cyber Security News
Building a Scalable Cybersecurity Training Program Building a Scalable Cybersecurity Training Program Cyber Security News
Hackers Drop Info-Stealing Malware On TikTok Users Device Using AI-Generated Videos Hackers Drop Info-Stealing Malware On TikTok Users Device Using AI-Generated Videos Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Git Addresses Critical Vulnerability in Recursive Clone Operations
  • Notion AI Chat Transcripts Exposed in Security Breach
  • Adobe Addresses Critical Vulnerabilities in Patch Update
  • Fireworks AI Security Breach Exposes Billing and Model Data
  • Railway Exposes AI Agent Exploit Causing $740K in Charges

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Git Addresses Critical Vulnerability in Recursive Clone Operations
  • Notion AI Chat Transcripts Exposed in Security Breach
  • Adobe Addresses Critical Vulnerabilities in Patch Update
  • Fireworks AI Security Breach Exposes Billing and Model Data
  • Railway Exposes AI Agent Exploit Causing $740K in Charges

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark