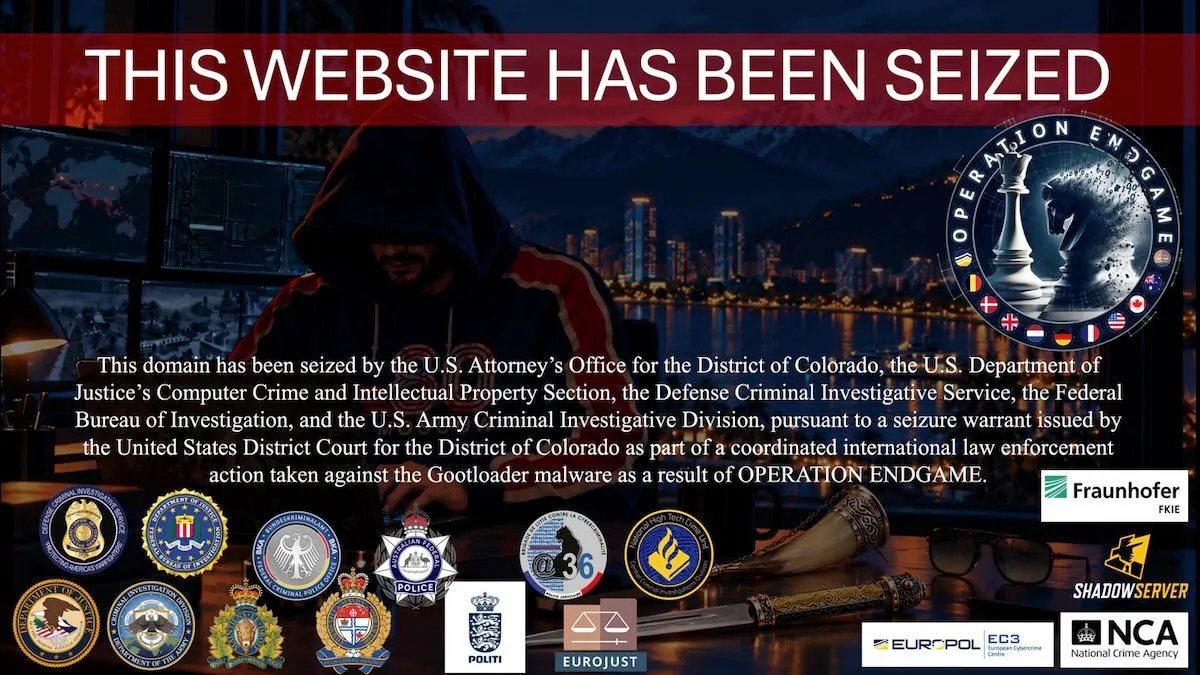
In a coordinated international effort, law enforcement agencies from the United States, Europe, Australia, and Canada have successfully dismantled the infrastructure supporting the notorious Gootloader, CastleRAT, and StealC malware. This operation marks a significant blow to global cybercrime networks.
Seizure of Malicious Infrastructure
Authorities have confiscated 235 servers and 257 domains linked to these malicious activities, significantly disrupting their operational capabilities. According to Europol, this seizure represents a critical step in undermining the distribution networks of these cyber threats.
Functioning under a cybercrime-as-a-service model, Gootloader, CastleRAT, and StealC facilitated various illicit activities, including ransomware attacks and data theft. These operations were often executed through deceptive websites that hosted fake legal documents.
Impact on Gootloader Operations
Since its emergence in 2018, Gootloader has been a major player in cybercrime, acting primarily as a dropper for other malware, including ransomware. It has reportedly infected over 25,000 devices and caused an estimated $28.8 million in damages within the United States alone.
The recent law enforcement efforts, part of an initiative known as Operation Endgame, have led to the removal of Gootloader from 100 servers. Europol reports that the operation resulted in the seizure of 14 servers and 218 domains, along with the cleanup of 681 compromised websites.
Disruption of CastleRAT and StealC
CastleRAT, a remote access trojan active since 2025, has been used by threat actors to gain control over infected systems, facilitating the deployment of ransomware. Law enforcement agencies successfully seized 120 servers and 39 domains associated with CastleRAT, acquiring significant victim data in the process.
StealC, operational since at least 2023, has been focused on extracting passwords, data, and identities. Recent efforts have disrupted 102 servers associated with this malware, with Europol reporting the seizure of 6.4 million victim credentials. These credentials have been distributed to organizations like HaveIBeenPwned and the Shadowserver Foundation for further analysis.
Europol emphasizes that these credentials were being sold for use in further cyber-attacks, highlighting the importance of this law enforcement operation in preventing future threats.
This extensive crackdown on cybercrime infrastructure showcases the power of international cooperation in tackling digital threats. The dismantling of these networks not only disrupts current criminal activities but also serves as a deterrent for future cybercriminal endeavors.