Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Best Web Vulnerability Scanners of 2026 Analyzed

Best Web Vulnerability Scanners of 2026 Analyzed

Posted on November 13, 2026 By CWS

Web application security is a critical concern in 2026, with vulnerability scanners playing a pivotal role in identifying potential risks. These tools are essential for analyzing web applications, including single-page apps, authenticated flows, and API backends, to provide a comprehensive security overview.

Leading Web Vulnerability Scanners

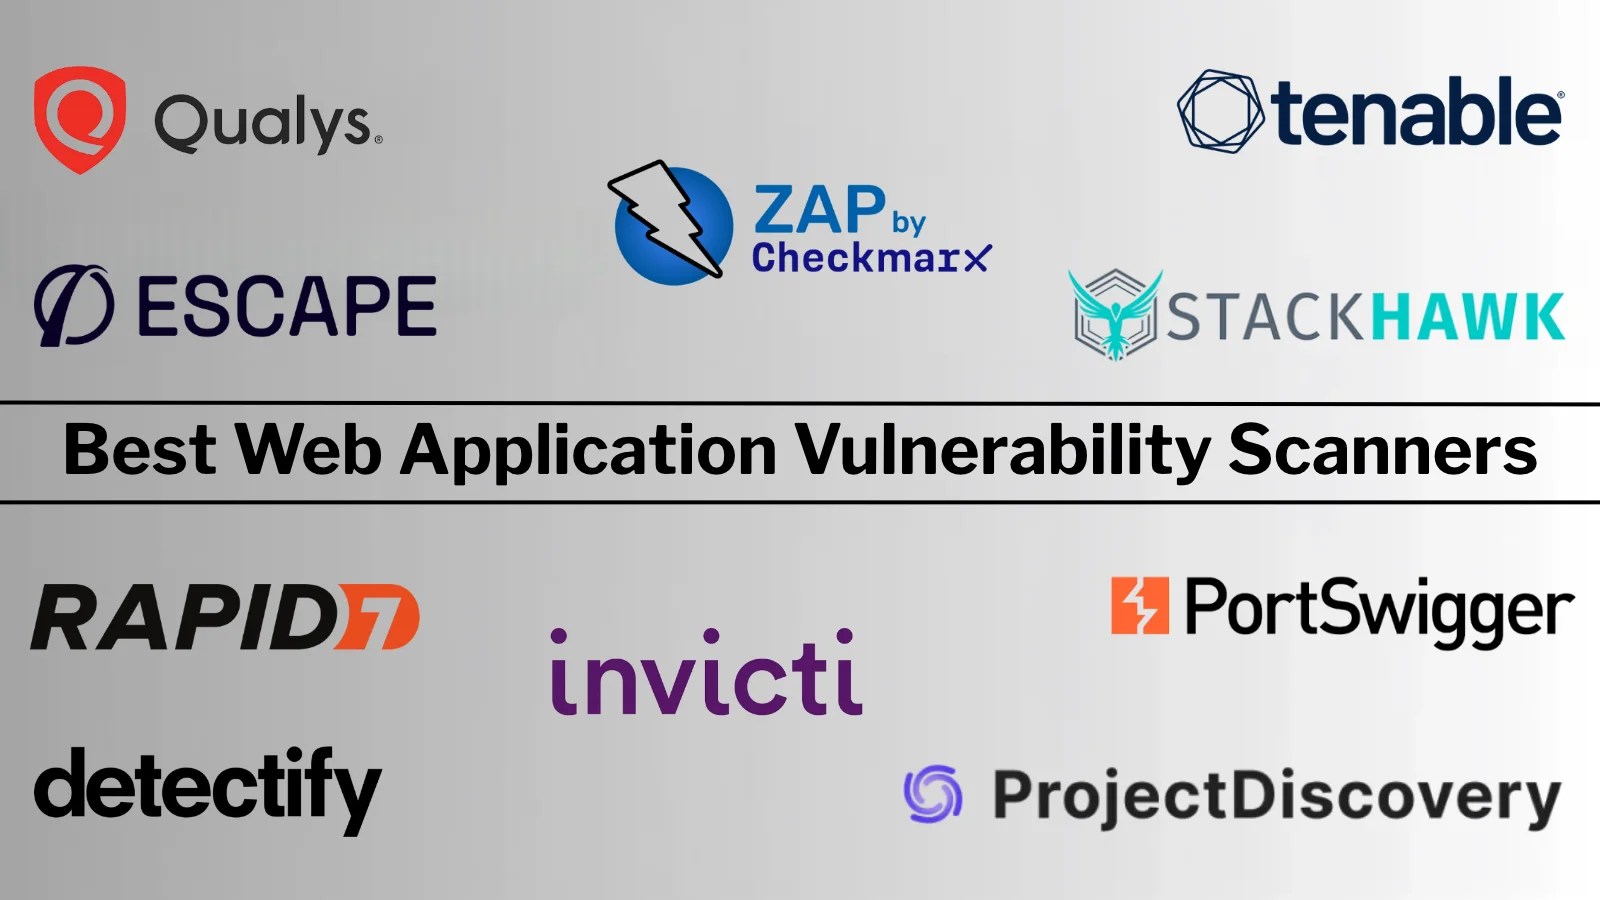
Among the top contenders, PortSwigger’s Burp Suite stands out as the professional benchmark, combining human expertise with automation. Invicti and Qualys follow closely, each offering unique benefits such as automation and platform integration.

Burp Suite is renowned for its depth in manual and automated testing, making it a favorite among cybersecurity professionals. Invicti’s strength lies in its proof-based validation, ensuring accurate findings, while Qualys integrates seamlessly with broader platform estates.

Scoring Methodology

The evaluation of these tools was research-driven, without lab testing or paid placements. Key criteria included crawl coverage, accuracy, integration with CI pipelines, and pricing. Coverage truth and accuracy each accounted for 25% of the total score.

Other factors like pipeline fit, scale ergonomics, and pricing accessibility were also considered, ensuring a balanced assessment of each scanner’s capabilities and limitations.

Top Picks and Features

OWASP ZAP is highlighted as the best open-source option, providing extensive scriptability at no cost. It’s an ideal choice for those looking to train and deploy in budget-conscious environments.

StackHawk excels in developer-pipeline integration, facilitating CI-native operations. Meanwhile, Detectify leverages crowdsourced payloads to enhance scanning accuracy.

ProjectDiscovery’s Nuclei addresses the need for rapid template updates, ensuring timely detection of new vulnerabilities. Escape focuses on API-first scanning, crucial for modern applications utilizing REST and GraphQL.

Overall, selecting the right tool depends on specific needs, including the requirement for proof-based validation, integration with existing platforms, and the ability to handle modern web technologies.

Conclusion and Future Outlook

As web vulnerabilities evolve, the importance of choosing the right scanner cannot be overstated. These tools not only help in maintaining security standards but also streamline the testing process, ensuring that applications are thoroughly evaluated before deployment.

Looking ahead, the integration of advanced technologies such as AI and machine learning will likely enhance the capabilities of these scanners, providing even more robust security solutions for web applications worldwide.

Cyber Security News Tags:API scanning, Cybersecurity, cybersecurity tools, DAST, SAST, security tools, vulnerability scanners, web app security, web application security, web security

Post navigation

Previous Post: Global Operation Shuts Down Major Cybercrime Networks
Next Post: Managing AI Agent Errors: Effective Control Strategies

Related Posts

Aeternum C2: Unstoppable Botnet Leveraging Blockchain Aeternum C2: Unstoppable Botnet Leveraging Blockchain Cyber Security News
Nx Console Extension Breach: Developer Secrets at Risk Nx Console Extension Breach: Developer Secrets at Risk Cyber Security News
Critical Vulnerability in OpenAI Codex Exposes macOS Users Critical Vulnerability in OpenAI Codex Exposes macOS Users Cyber Security News
UAT-638 Hackers Exploit Cityworks Zero-Day to Attack IIS Servers With VSHell Malware UAT-638 Hackers Exploit Cityworks Zero-Day to Attack IIS Servers With VSHell Malware Cyber Security News
Critical GitHub Copilot Vulnerability Let Attackers Exfiltrate Source Code From Private Repos Critical GitHub Copilot Vulnerability Let Attackers Exfiltrate Source Code From Private Repos Cyber Security News
Citrix Calls for Urgent Patching of Critical NetScaler Flaw Citrix Calls for Urgent Patching of Critical NetScaler Flaw Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI-Powered Cyberattacks Breach Multiple Organizations
  • Apify Cyberattack Exposes Customer Data
  • Managing AI Agent Errors: Effective Control Strategies
  • Best Web Vulnerability Scanners of 2026 Analyzed
  • Global Operation Shuts Down Major Cybercrime Networks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI-Powered Cyberattacks Breach Multiple Organizations
  • Apify Cyberattack Exposes Customer Data
  • Managing AI Agent Errors: Effective Control Strategies
  • Best Web Vulnerability Scanners of 2026 Analyzed
  • Global Operation Shuts Down Major Cybercrime Networks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark