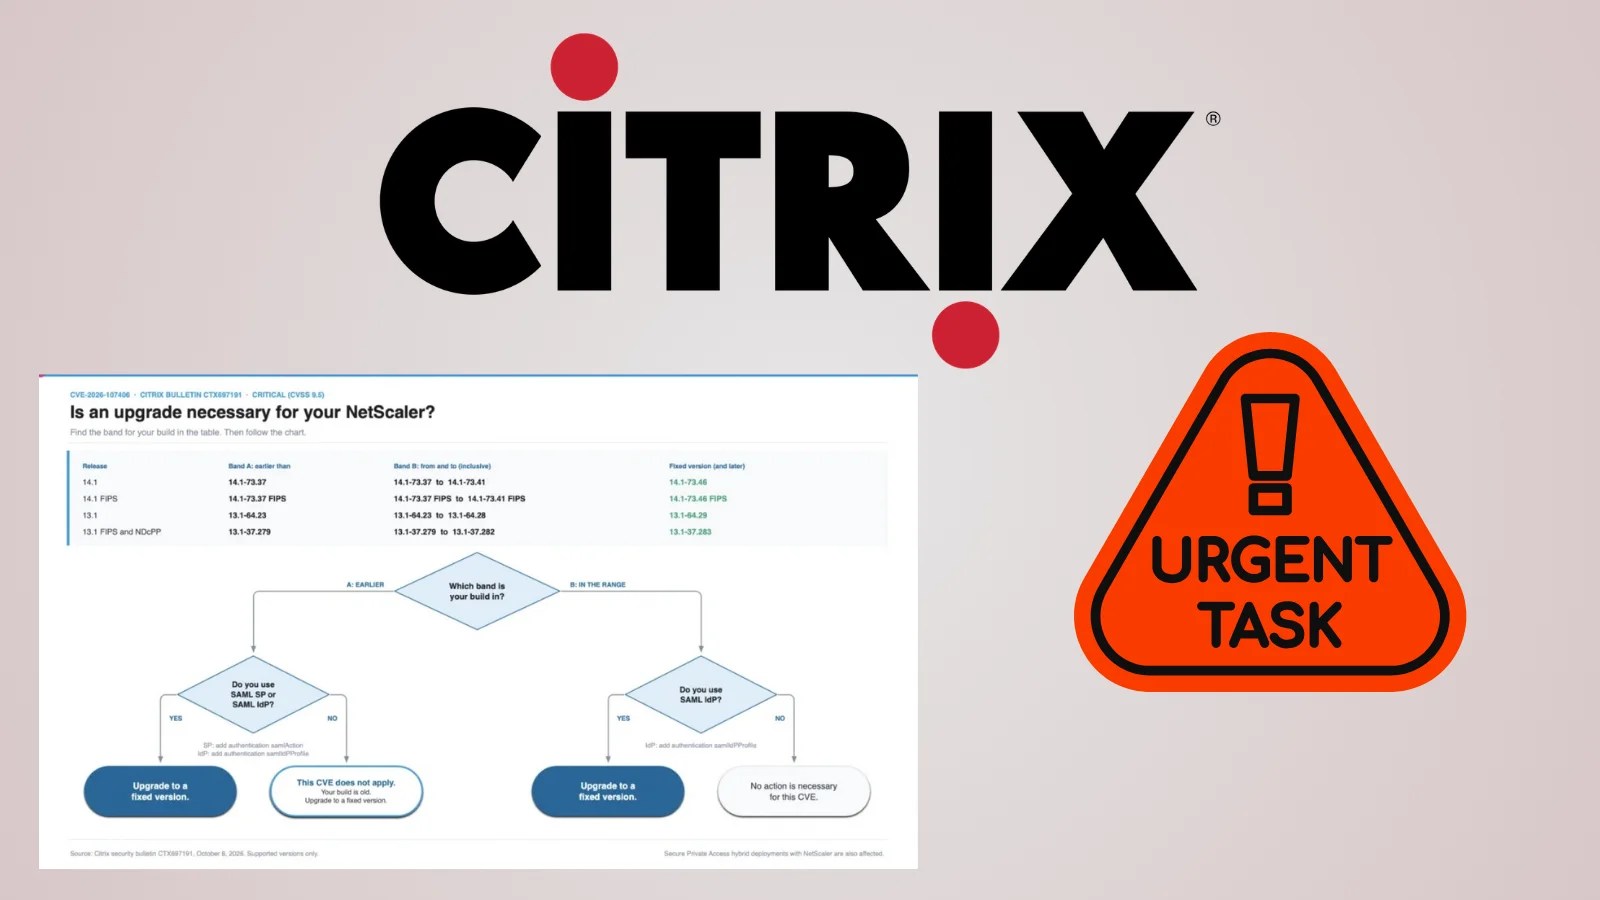
Citrix has issued an urgent advisory for customers to address a critical vulnerability in its NetScaler ADC and NetScaler Gateway products. The flaw, identified as CVE-2026-107406, poses significant risks including remote code execution and denial of service. With a CVSS v4.0 score of 9.5, this memory overflow issue primarily affects systems configured with specific SAML settings. Detailed in the security bulletin CTX697191, the vulnerability was highlighted on October 8, 2026.
Understanding the Vulnerability
At the time of publication, Citrix reported no known unmitigated exploits. However, this does not guarantee immunity for all deployments. Users must verify both their software versions and authentication configurations to assess their exposure. Classified under CWE-119, the vulnerability indicates improper memory buffer restrictions. An attacker might exploit this flaw to execute arbitrary code or disrupt services. Although complex, the attack requires no special privileges or user interaction. Citrix has refrained from providing specific exploit instructions in the bulletin.
Contributors to discovering this vulnerability include Michael Tucker, Chew Keong Tan, and Alex Bernier from the JPMorgan Chase XOR Team, alongside Maxim Suhanov. The bulletin lacks details on any active attack campaigns or specific organizations affected, focusing solely on technical aspects.
Impact on NetScaler Deployments
The vulnerability’s impact hinges on whether NetScaler functions as a SAML Identity Provider (IdP) or Service Provider (SP), both crucial for single sign-on operations. Affected versions include NetScaler ADC and Gateway builds 14.1-73.37 through 14.1-73.41 and 13.1-64.23 through 13.1-64.28, specifically when configured as a SAML IdP. Similar conditions apply to NetScaler ADC 14.1-FIPS builds and other specified versions.
Older supported builds face broader exposure if configured as either SAML SP or IdP, with critical thresholds outlined for various branches. Administrators are advised to inspect their configurations for specific SAML settings and compare them against the affected version ranges.
Recommended Actions and Future Updates
To mitigate the vulnerability, Citrix advises upgrading NetScaler ADC and Gateway to versions 14.1-73.46 or later in the 14.1 branch and 13.1-64.29 or later in the 13.1 branch. For FIPS and NDcPP configurations, the requisite updates are also detailed. These updates are crucial for Secure Private Access Hybrid deployments using affected instances.
This advisory follows previous updates concerning NetScaler security issues, including a SAML zero-day vulnerability. While past advisories provide context, the current bulletin, CTX697191, should be the primary reference for addressing this specific flaw. Administrators are encouraged to promptly confirm SAML roles on all affected appliances and implement the recommended updates to ensure security integrity.