Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
US Cybersecurity Agency Flags Wi-Fi Range Extender Vulnerability Under Active Attack

US Cybersecurity Agency Flags Wi-Fi Range Extender Vulnerability Under Active Attack

Posted on September 3, 2025September 3, 2025 By CWS

The US cybersecurity company CISA issued a contemporary warning {that a} lacking authentication vulnerability in TP-Hyperlink TL-WA855RE Wi-Fi vary extender merchandise has been exploited in assaults.

Tracked as CVE-2020-24363 (CVSS rating of 8.8), the flaw is described as a lacking authentication for a important operate challenge that permits an attacker on the identical community to ship unauthenticated requests for a manufacturing facility reset and reboot.

“The attacker can then get hold of incorrect entry management by setting a brand new administrative password,” a NIST advisory reads.

In August 2020, malwrforensics warned that, though the system’s net interface requires authentication to entry administrative controls, unauthenticated attackers can ship TDDP_RESET POST requests and circumvent the mechanism.

“Nevertheless, an attacker can bypass it and use the APIs supplied to ship the TDDP_RESET code which doesn’t have any authentication,” malwrforensics stated.

TP-Hyperlink resolved the vulnerability over half a decade in the past, in firmware launch (EU)_V5_200731, and has since launched a number of different firmware updates for the extender. Nevertheless, the TL-WA855RE extender is now marked as discontinued on the corporate’s web site.

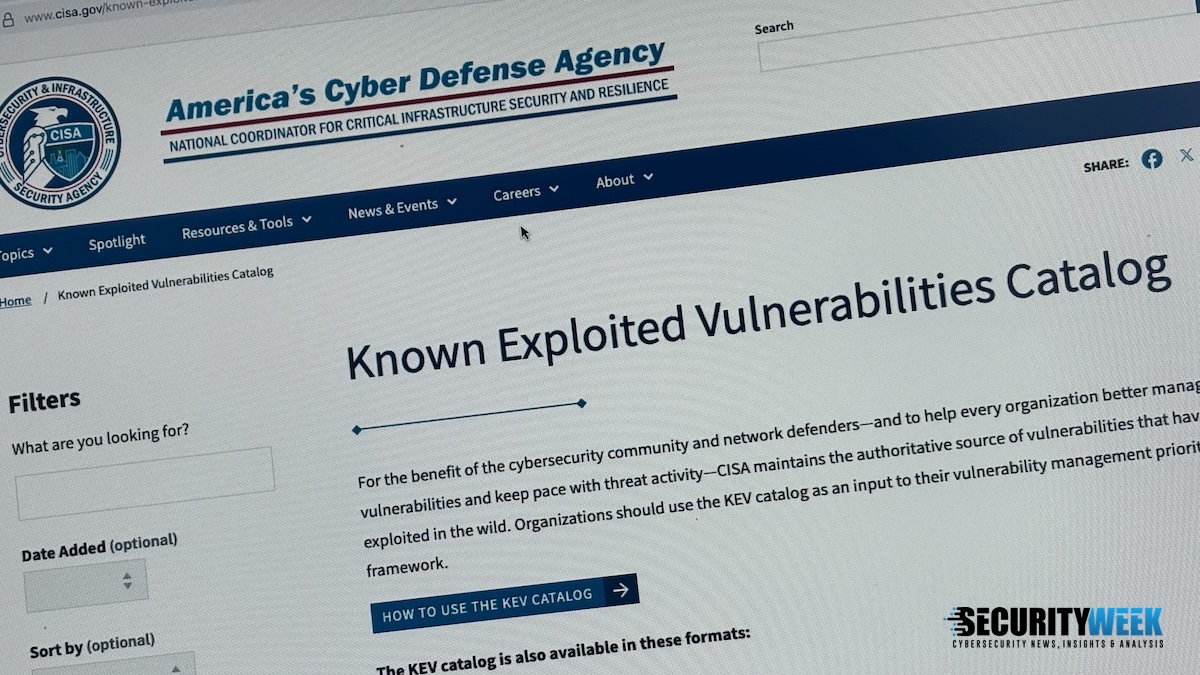
On Tuesday, CISA added CVE-2020-24363 to its Identified Exploited Vulnerabilities (KEV) catalog together with the not too long ago disclosed WhatsApp zero-day, urging federal businesses to handle each by September 23.

“The impacted merchandise may very well be end-of-life (EoL) and/or end-of-service (EoS). Customers ought to discontinue product utilization,” CISA notes in CVE-2020-24363’s description.Commercial. Scroll to proceed studying.

There look like no experiences on the CVE’s in-the-wild exploitation previous to CISA’s warning, however proof-of-concept (PoC) exploit code focusing on the vulnerability has been publicly out there since July 2020.

Associated: Sangoma Patches Important Zero-Day Exploited to Hack FreePBX Servers

Associated: WhatsApp Zero-Day Exploited in Assaults Focusing on Apple Customers

Associated: Hundreds of SaaS Apps May Nonetheless Be Prone to nOAuth

Associated: Microsoft Utilizing AI to Uncover Important Bootloader Vulnerabilities
Security Week News Tags:Active, Agency, Attack, Cybersecurity, Extender, Flags, Range, Vulnerability, WiFi

Post navigation

Previous Post: A Milestone Powering Crypto’s Global Reach
Next Post: CISA Warns of Critical SunPower Device Vulnerability Let Attackers Gain Full Device Access

Related Posts

MITRE Posts Results of 2025 ATT&CK Enterprise Evaluations MITRE Posts Results of 2025 ATT&CK Enterprise Evaluations Security Week News
AI Models Struggle with Nuclear-Sabotage Malware Analysis AI Models Struggle with Nuclear-Sabotage Malware Analysis Security Week News
Meta’s Muse AI Bug Bounty Program Awards .2 Million Meta’s Muse AI Bug Bounty Program Awards $1.2 Million Security Week News
Huskeys Secures  Million in Seed Funding for ESM Platform Huskeys Secures $8 Million in Seed Funding for ESM Platform Security Week News
Critical PHP Vulnerabilities Prompt Urgent Patches Critical PHP Vulnerabilities Prompt Urgent Patches Security Week News
Turla and Gamaredon Working Together in Fresh Ukrainian Intrusions Turla and Gamaredon Working Together in Fresh Ukrainian Intrusions Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Apple Patches Bluetooth and AirPlay Security Flaws
  • Critical Cisco and Openwave Flaws Under Active Exploitation
  • Fortinet Security Vulnerabilities Allow Remote Code Execution
  • GhostFrame Malware Threatens VMware ESXi Servers
  • Hackers Exploit Outlook Flaw to Steal Authentication Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Apple Patches Bluetooth and AirPlay Security Flaws
  • Critical Cisco and Openwave Flaws Under Active Exploitation
  • Fortinet Security Vulnerabilities Allow Remote Code Execution
  • GhostFrame Malware Threatens VMware ESXi Servers
  • Hackers Exploit Outlook Flaw to Steal Authentication Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark