Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Beware of Fake Online Speedtest Application With Obfuscated JS Codes

Beware of Fake Online Speedtest Application With Obfuscated JS Codes

Posted on September 23, 2025September 23, 2025 By CWS

A complicated malware marketing campaign has emerged that leverages faux on-line pace take a look at purposes to deploy obfuscated JavaScript payloads on Home windows techniques.

These malicious utilities masquerade as legit community pace testing instruments, guide readers, PDF utilities, and numerous search frontends to deceive unsuspecting customers into putting in harmful code that operates covertly within the background.

The assault begins when customers obtain what seems to be a practical pace testing software from compromised or malicious domains equivalent to onlinespeedtestservice[.]com.

Upon set up, the applying delivers its marketed performance, making a false sense of safety whereas concurrently deploying a hidden Node.js runtime surroundings alongside closely obfuscated JavaScript recordsdata.

The seen executable performs as anticipated, sustaining the person’s belief whereas the malicious elements set up themselves inside the system.

Safety Magic analysts recognized that these purposes are packaged utilizing Inno-Packer installers, which bundle legit performance with malicious elements together with a conveyable Node runtime, scheduled activity configurations, and obfuscated JavaScript payloads that serve no objective for the applying’s major perform.

The malware operates independently from the primary executable, considerably increasing the assault floor and offering menace actors with persistent entry to compromised techniques.

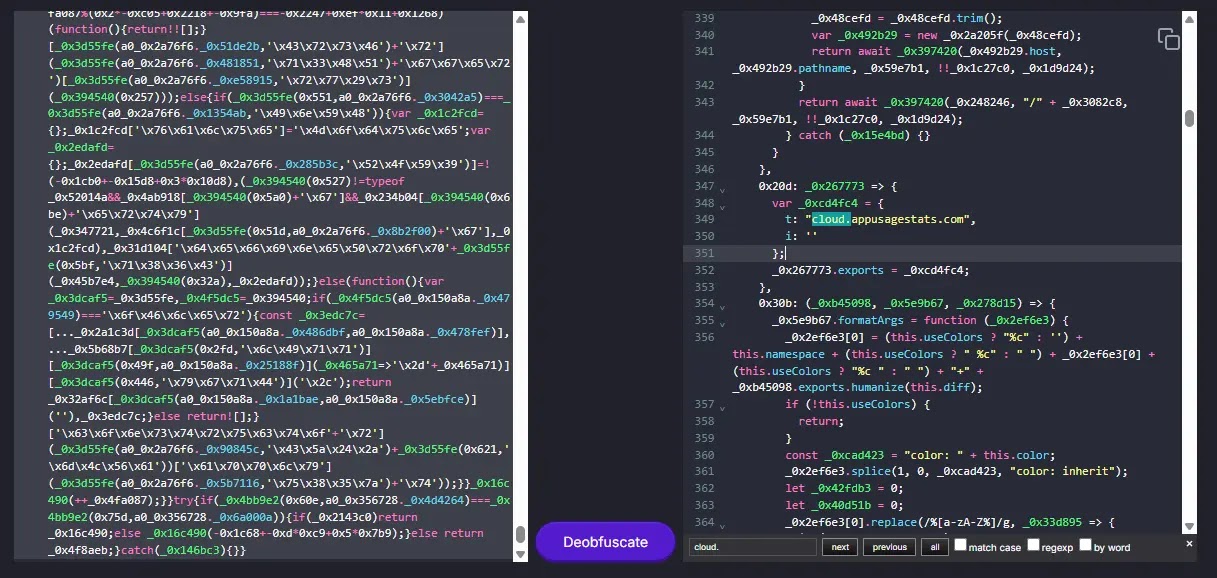
Obfuscated JS (Supply – Safety Magic)

The an infection establishes persistence by scheduled duties that execute the malicious JavaScript payload roughly each 12 hours.

This JavaScript element maintains encrypted communications with command and management servers, particularly cloud.appusagestats.com, and possesses the aptitude to execute arbitrary code delivered by distant servers.

The malware queries system data together with the Home windows registry key HKLMSoftwareMicrosoftCryptographyMachineGuid to assemble machine identification knowledge for transmission to attackers.

Superior Obfuscation and Command Execution Mechanisms

The JavaScript payload employs subtle obfuscation strategies that conceal its true objective from safety evaluation.

Researchers found that the obfuscated code accommodates encoded strings that may be decoded by patching the return assertion of the decode perform.

When decoded, the JavaScript reveals its communication protocol with the command and management infrastructure. The malware transmits JSON-formatted knowledge containing model data, system identifiers, and functionality flags.

Evaluation of community communications reveals the payload can obtain and execute PowerShell instructions, with researchers observing take a look at executions that displayed message packing containers by Home windows Kinds assemblies.

The command execution mechanism makes use of Node.js child_process modules to spawn system processes, enabling arbitrary code execution with person privileges whereas sustaining stealth by hidden window modes and no-profile PowerShell executions.

Observe us on Google Information, LinkedIn, and X to Get Extra On the spot Updates, Set CSN as a Most well-liked Supply in Google.

Cyber Security News Tags:Application, Beware, Codes, Fake, Obfuscated, Online, Speedtest

Post navigation

Previous Post: Two New Supermicro BMC Bugs Allow Malicious Firmware to Evade Root of Trust Security
Next Post: A Massive Telecom Threat Was Stopped Right As World Leaders Gathered at UN Headquarters in New York

Related Posts

SilkParasite Cyber Espionage Unveiled in Central Asia SilkParasite Cyber Espionage Unveiled in Central Asia Cyber Security News
Red Hat Confirms Data Breach After Hackers Claim to Steal 570GB of Private GitHub Repositories Red Hat Confirms Data Breach After Hackers Claim to Steal 570GB of Private GitHub Repositories Cyber Security News
New Osiris Ransomware Using Wide Range of Living off the Land and Dual-use Tools in Attacks New Osiris Ransomware Using Wide Range of Living off the Land and Dual-use Tools in Attacks Cyber Security News
North Korean Hackers Target South Korean Firms with Backdoor North Korean Hackers Target South Korean Firms with Backdoor Cyber Security News
China-Linked Group OP-512 Exploits IIS Servers China-Linked Group OP-512 Exploits IIS Servers Cyber Security News
Critical Marimo Flaw Exploited Within Hours of Disclosure Critical Marimo Flaw Exploited Within Hours of Disclosure Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark