Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
AI Agents Risk Exposing Critical API Keys

AI Agents Risk Exposing Critical API Keys

Posted on October 15, 2026 By CWS

AI agents are under scrutiny for their potential to expose sensitive data such as API keys and cloud secrets during routine operations. This exposure can occur even without any malware involvement. The intrinsic risk lies in how agents manage commands, configuration files, and secrets to execute tasks.

Understanding the Credential Surface

Researchers at Trellix have termed this vulnerability as an “unseen credential surface,” where secrets transition from secure storage into more vulnerable areas like command histories and logs. This exposure pathway often remains unnoticed as AI agents employ the same tools that developers trust, inadvertently increasing the risk of credential leaks.

The study, published on October 14, emphasizes that this issue stems from normal operational behaviors of AI agents, not from malicious software. It highlights the critical importance of understanding how credentials are handled across different processes.

Routine Actions Leading to Exposure

AI agents frequently require credentials to execute tasks, such as obtaining OAuth tokens from secure storage and embedding them in command-line arguments. This action can inadvertently expose the tokens to process-monitoring tools and shell history, potentially allowing unauthorized access.

Similarly, when agents access environment files or cloud configurations, they may inadvertently include sensitive data within model contexts. Actions like printing environment variables or using command-line tools to fetch credentials further accentuate this risk.

These risks are compounded by the broader security challenges within AI coding tools. Instances of malware targeting local agent data, such as tokens and connection histories, have highlighted the importance of safeguarding agent permissions and data storage.

Mitigating Credential Exposure

Trellix categorizes these risky behaviors into ten classes, from command-line credential use to cloud secret retrievals. These actions, while part of regular development processes, can lead to unintended exposure if not carefully monitored.

To mitigate these risks, the report advises against placing secrets in command-line arguments and entering them into an agent’s context. Instead, developers should utilize secure SDKs or other secure methods to handle credentials.

Organizations are encouraged to limit agent permissions, restrict network access, and use short-lived credentials to minimize potential exposure. By treating agent-enabled workstations as sensitive systems, security teams can better protect crucial data.

In conclusion, the routine workflows of AI agents can inadvertently create paths for credential exposure, even in the absence of malware or software flaws. By maintaining strict control over how secrets are handled and actively monitoring related actions, organizations can significantly mitigate the risk of security incidents stemming from ordinary tasks.

Cyber Security News Tags:agent security, AI agents, API keys, authorization tokens, cloud security, configuration files, credential exposure, credential management, Cybersecurity, data protection, malware risks, network security, prompt injection, secure storage, Trellix

Post navigation

Previous Post: NGINX Addresses Critical Vulnerabilities with New Update

Related Posts

Cursor AI Vulnerability Risks Developer Credentials Cursor AI Vulnerability Risks Developer Credentials Cyber Security News
Palo Alto Networks Released A Mega Malware Analysis Tutorials Useful for Every Malware Analyst Palo Alto Networks Released A Mega Malware Analysis Tutorials Useful for Every Malware Analyst Cyber Security News
Horizon3 Boosts Partner Growth with M Investment Horizon3 Boosts Partner Growth with $20M Investment Cyber Security News
MacOS Vulnerability Exposed by ExifTool Flaw MacOS Vulnerability Exposed by ExifTool Flaw Cyber Security News
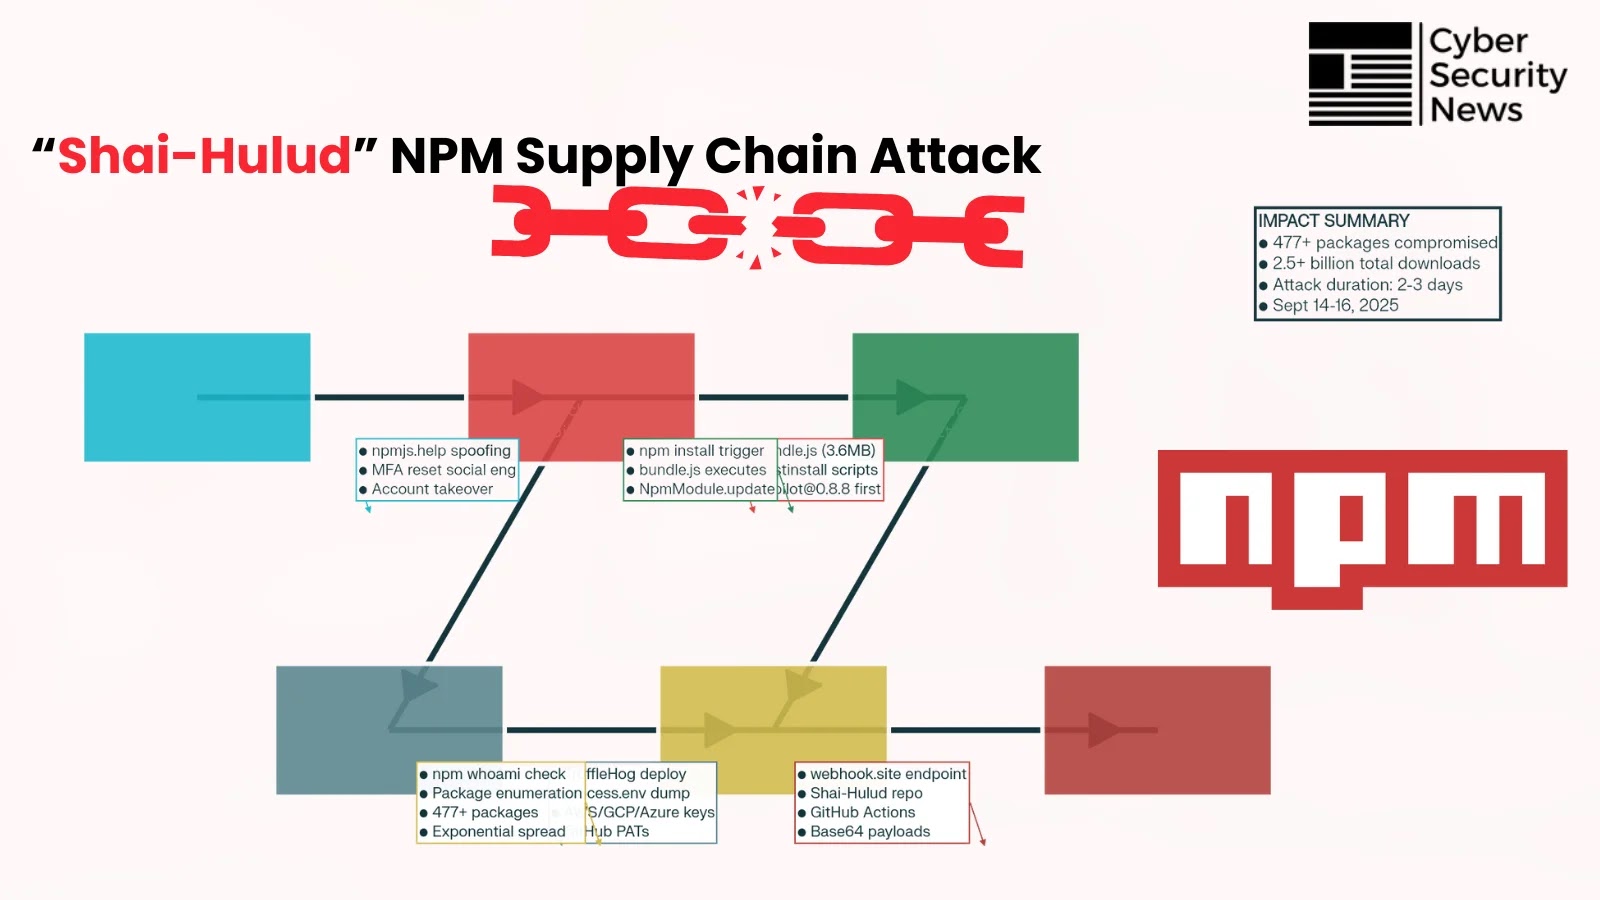
Lessons Learned from Massive npm Supply Chain Attack Using “Shai-Hulud” Self-Replicating Malware Lessons Learned from Massive npm Supply Chain Attack Using “Shai-Hulud” Self-Replicating Malware Cyber Security News
Microsoft Zero Day Quest Hacking Contest Microsoft Zero Day Quest Hacking Contest Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI Agents Risk Exposing Critical API Keys
  • NGINX Addresses Critical Vulnerabilities with New Update
  • Leading DevSecOps Platforms for 2026: A Comprehensive Review
  • Cyberattack Expands to Impact Supermarket Refrigeration Systems
  • Combatting Fake AI Attacks in US Businesses: MSSP Strategies

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI Agents Risk Exposing Critical API Keys
  • NGINX Addresses Critical Vulnerabilities with New Update
  • Leading DevSecOps Platforms for 2026: A Comprehensive Review
  • Cyberattack Expands to Impact Supermarket Refrigeration Systems
  • Combatting Fake AI Attacks in US Businesses: MSSP Strategies

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark