Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
AI Systems Under Siege: RCE and API Key Threats

AI Systems Under Siege: RCE and API Key Threats

Posted on August 28, 2026 By CWS

Cybercriminals are increasingly targeting artificial intelligence infrastructures by exploiting vulnerabilities for remote code execution (RCE), credential theft, and cryptomining. The expanding use of AI systems in the cloud has created new avenues for these attacks.

Emerging Techniques in AI System Exploitation

Over a three-month period, attackers have developed sophisticated methods to compromise services that route AI model traffic and connect agent tools. These campaigns leverage weaknesses in exposed servers, directing AI agents to execute unauthorized commands and seek out API keys.

Research from Wiz.io has highlighted ongoing malicious activity through honeypots designed to mimic AI services. This research covered a range of systems including LiteLLM, MCP servers, LangChain, and more, unveiling customized intrusion strategies.

Vulnerabilities in AI Proxies and Gateways

Wiz.io’s report, shared with Cyber Security News, emphasizes that a single compromised application can have far-reaching effects. AI proxies often centralize critical credentials and permissions, making them attractive targets. Poorly configured deployments can become gateways to sensitive data and systems.

One notable attack focused on Model Context Protocol (MCP) services exposed to the internet. These services enable agents to access databases and internal APIs, magnifying the impact of a breached gateway. Exploits included LiteLLM vulnerabilities, such as an authentication bypass and command injection flaws.

Securing AI Systems Against Attack

Security experts stress the necessity of integrating AI security with traditional infrastructure defenses. A seemingly minor configuration error in a model gateway can lead to major enterprise-wide security breaches. Comprehensive security evaluations should include every tool, secret, and network path involved.

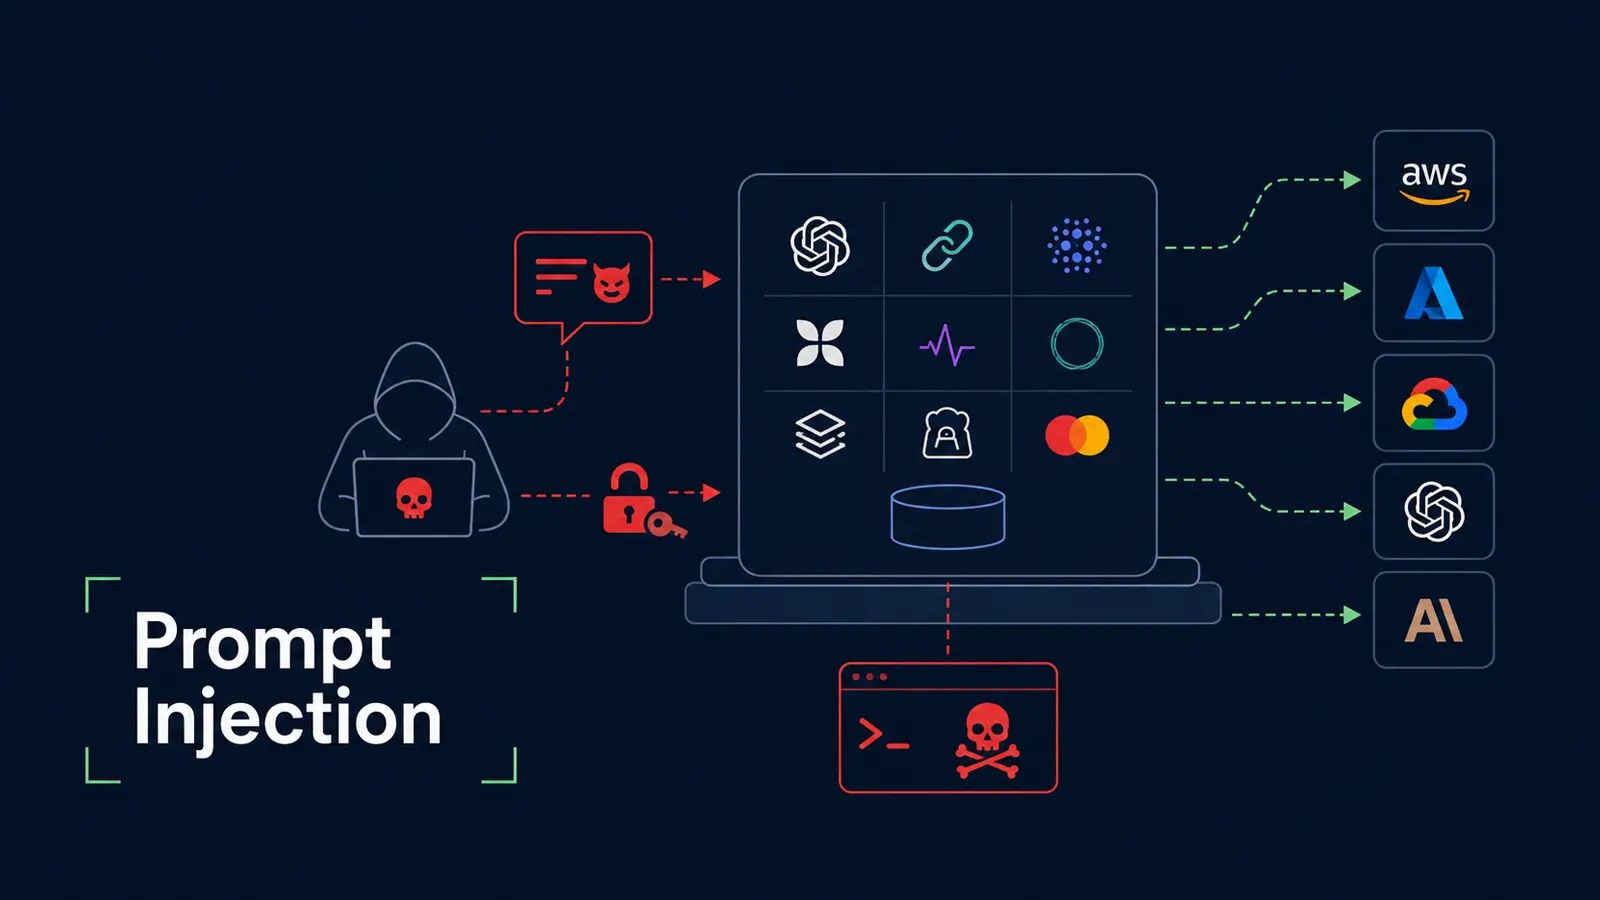
Recent attacks also employed blind prompt injection tactics, instructing AI agents with shell access to execute commands. This method, which leverages untrusted text as trusted instructions, has been observed to deploy cryptominers on systems like Node-RED, underscoring the risks of granting shell access to agents.

Protecting API Keys and Sensitive Data

Attackers have also been focusing on retrieving API keys, turning AI gateways into stores for critical credentials. On platforms like LiteLLM, hackers have extracted proxy master keys from memory and targeted backend models for key theft.

Organizations are advised to carefully manage their AI services, enforce strict authentication measures, and limit permissions to mitigate these threats. Regular monitoring and quick patching of vulnerabilities are crucial to prevent unauthorized access and potential data breaches.

In conclusion, the threat landscape for AI infrastructures is evolving rapidly. As attackers become more adept at exploiting AI systems, robust security measures are essential to protect sensitive data and maintain system integrity.
Cyber Security News Tags:AI infrastructure, AI security, API key theft, cloud entry points, cloud security, credential theft, cyber attacks, Cybersecurity, Hackers, Honeypots, MCP services, Qilin ransomware, RCE, remote code execution, Wiz.io

Post navigation

Previous Post: Android 17 Enhances Privacy with OS-Wide ECH Integration
Next Post: Critical ownCloud Vulnerability Used in Targeted Attacks

Related Posts

Hackers Use AutoIt to Conceal AsyncRAT in Windows Hackers Use AutoIt to Conceal AsyncRAT in Windows Cyber Security News
Threat Actors Pose as Government Officials to Attack Organizations with StallionRAT Threat Actors Pose as Government Officials to Attack Organizations with StallionRAT Cyber Security News
New Tool Enhances Windows Credential Recovery New Tool Enhances Windows Credential Recovery Cyber Security News
US Bank Probes LockBit Ransomware Data Breach Allegations US Bank Probes LockBit Ransomware Data Breach Allegations Cyber Security News
Hackers Exploiting Adobe Magento RCE Vulnerability Exploited in the Wild Hackers Exploiting Adobe Magento RCE Vulnerability Exploited in the Wild Cyber Security News
Happy DOM Vulnerability Exposes 2.7 Million Users To Remote Code Execution Attacks Happy DOM Vulnerability Exposes 2.7 Million Users To Remote Code Execution Attacks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark