Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
ASOS Investigates Unauthorized Notifications Breach

ASOS Investigates Unauthorized Notifications Breach

Posted on October 6, 2026 By CWS

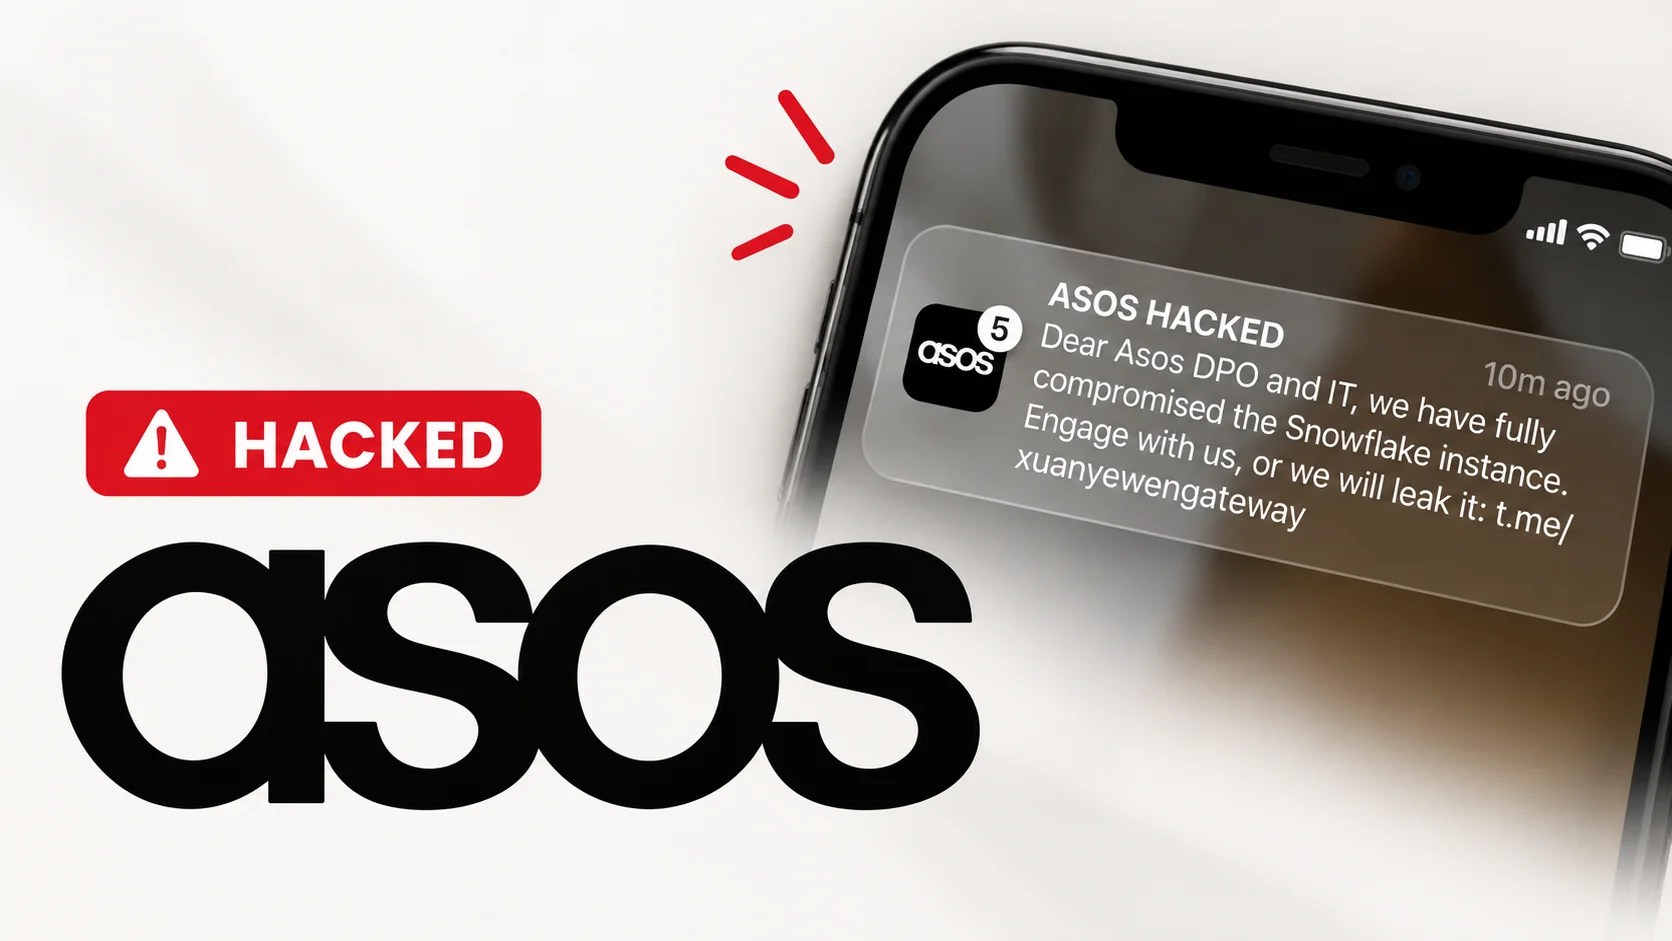
ASOS is currently investigating a cyber incident after customers were surprised by a rogue notification sent through its app. The notification, allegedly from hackers, claimed unauthorized access to ASOS’s Snowflake data platform. However, the retailer has yet to confirm any breach of its Snowflake instance.

Details of the Unauthorized Notification

On October 6, 2026, at approximately 10 am, customers received a notification titled “ASOS HACKED.” The message, directed at ASOS’s data protection officer and IT team, warned of a complete compromise of their Snowflake instance and included a link to a Telegram channel. Despite the alarming nature of the message, ASOS has not verified the breach of its Snowflake platform.

ASOS’s Response to the Incident

ASOS has acknowledged unauthorized activity involving third-party communication platforms used to contact customers. The company has already restricted access to these platforms and is collaborating with cybersecurity experts and authorities to investigate the matter. Initial assessments suggest that only basic personal information, such as names and contact details, might have been accessed, while payment information and passwords remain secure.

The retailer reassured customers that its website and app are functioning normally and that it holds a cybersecurity and business continuity insurance policy with a major global provider. The potential impact on trading is still under evaluation.

Understanding the Potential Threat

Snowflake serves as a cloud data platform for storing and analyzing information. Unauthorized access to notification platforms does not equate to a breach of cloud databases or payment systems. Experts suggest that the hackers’ message might be an attempt to embarrass ASOS publicly, rather than an indication of a successful hack.

Investigators are working to determine the method of entry, the systems involved, and whether any customer records were compromised. This incident follows a previous case reported on August 25, 2026, where ASOS customer accounts were accessed through compromised credentials obtained externally.

Advice for Customers

ASOS’s shares saw a decline of over 11% following the incident. Customers are advised to avoid engaging with the Telegram link and to stay informed through official ASOS updates. Be cautious of unsolicited emails or texts that might exploit the situation to request sensitive information. Those using the same password for different accounts should consider changing them immediately to enhance security.

ASOS continues to prioritize customer safety and data protection as the investigation unfolds. Further updates will be provided as the company works to resolve the situation and safeguard its systems from future threats.
Cyber Security News Tags:app security, ASOS, credential stuffing, customer data, customer notification, cyber incident, Cybersecurity, data breach, data protection, Hacking, IT security, online retail, retail security, Snowflake, technology news

Post navigation

Previous Post: Linux Backdoors Mimic Email Tools to Evade Detection

Related Posts

GOLD SALEM Compromise Networks and Bypass Security Solutions to Deploy Warlock Ransomware GOLD SALEM Compromise Networks and Bypass Security Solutions to Deploy Warlock Ransomware Cyber Security News
Google Chrome RCE Vulnerability Details Released Along with Exploit Code Google Chrome RCE Vulnerability Details Released Along with Exploit Code Cyber Security News
Top 5 WMIC Commands Used By Malware  Top 5 WMIC Commands Used By Malware  Cyber Security News
Anthropic’s Claude Code Source Leak via npm Registry Anthropic’s Claude Code Source Leak via npm Registry Cyber Security News
Next.js Enhances Security with Monthly Update Program Next.js Enhances Security with Monthly Update Program Cyber Security News
Chrome Extensions Vulnerability Exposes API Keys, Secrets, and Tokens Chrome Extensions Vulnerability Exposes API Keys, Secrets, and Tokens Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • ASOS Investigates Unauthorized Notifications Breach
  • Linux Backdoors Mimic Email Tools to Evade Detection
  • Enhancing Threat Monitoring with Intelligence-Led Approaches
  • Phishing Platforms Target AI Chatbot Users for Credentials
  • GitHub Copilot CLI Flaw Risks Developer Data Exposure

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • ASOS Investigates Unauthorized Notifications Breach
  • Linux Backdoors Mimic Email Tools to Evade Detection
  • Enhancing Threat Monitoring with Intelligence-Led Approaches
  • Phishing Platforms Target AI Chatbot Users for Credentials
  • GitHub Copilot CLI Flaw Risks Developer Data Exposure

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark