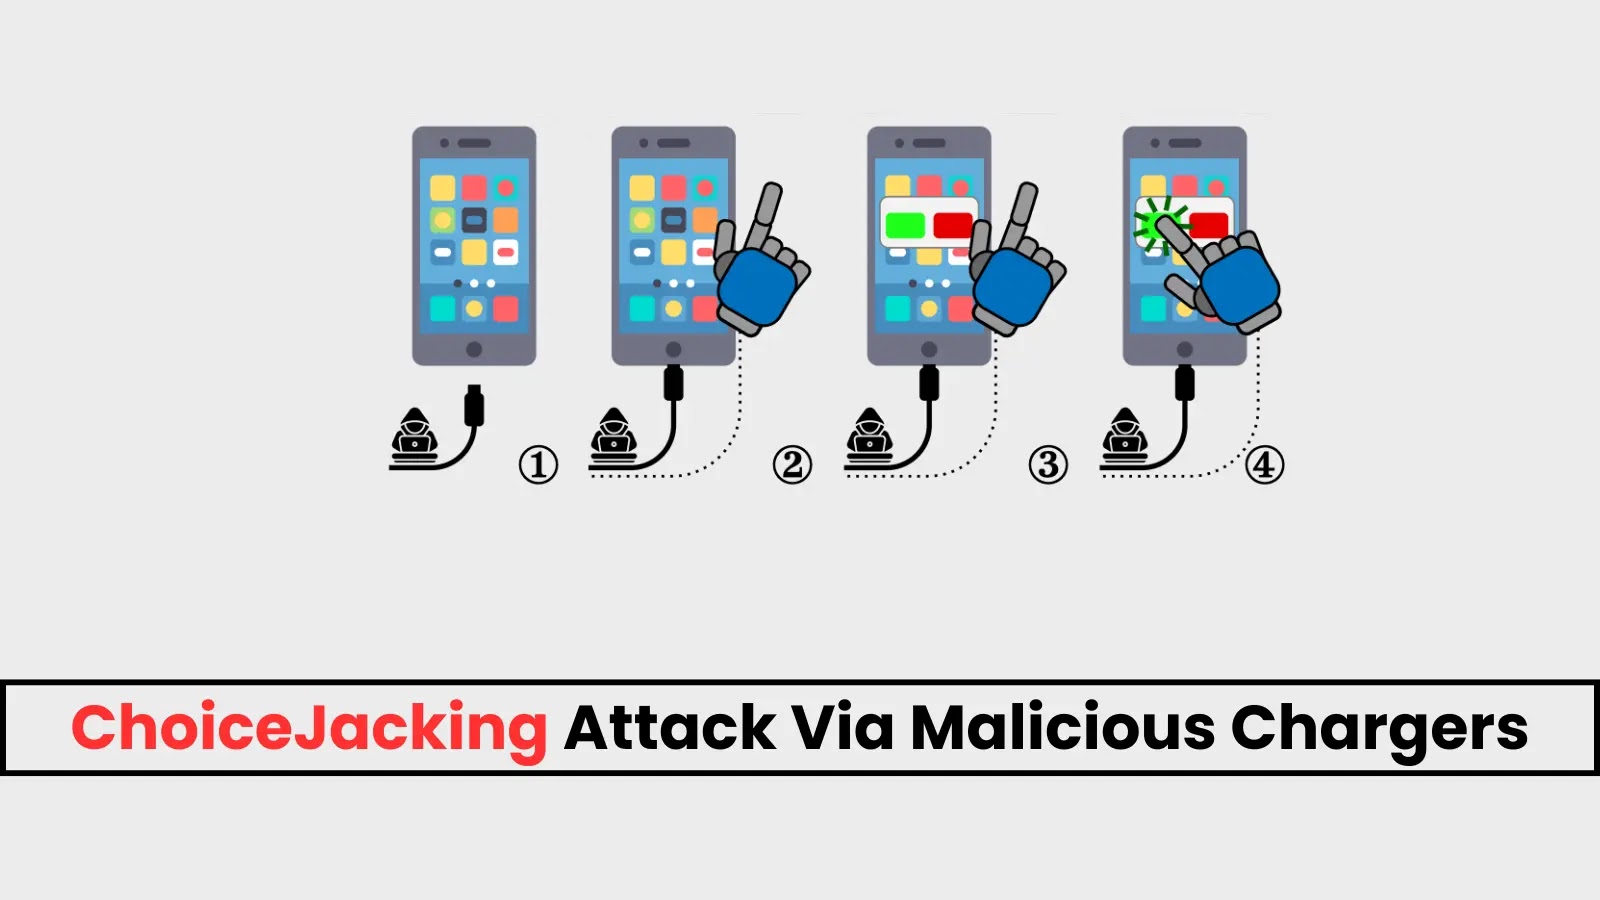
Cybersecurity researchers have uncovered a classy new assault technique referred to as “ChoiceJacking” that permits malicious charging stations to steal delicate information from smartphones and tablets, successfully bypassing safety measures which have protected cellular gadgets for over a decade.
The assault, found by researchers at Graz College of Know-how in Austria, represents a big evolution of the older “juice jacking” approach that prompted Apple and Google to implement person affirmation prompts when gadgets connect with USB hosts for information switch.
Nevertheless, ChoiceJacking exploits elementary flaws in these very protections, permitting attackers to ascertain their very own information connections autonomously with out the person’s information.
Assault precept
“Regardless of vendor customizations in USB stacks, ChoiceJacking assaults acquire entry to delicate person information (footage, paperwork, app information) on all examined gadgets from 8 distributors together with the highest 6 by market share,” the researchers said. The staff evaluated gadgets from main producers, together with Samsung, Apple, Google, Xiaomi, Oppo, Vivo, Huawei, and Honor.
How the ChoiceJacking Assault Works
ChoiceJacking operates via three distinct methods that mix facets of each malicious USB hosts and USB gadgets. The best technique exploits flaws in Android’s Open Accent Protocol (AOAP), permitting a charging station to register as an enter machine whereas concurrently working as a USB host.
In follow, a malicious charger can inject enter occasions to mechanically settle for safety prompts that seem on the sufferer’s display screen. The assault can full in as little as 133 milliseconds on some gadgets, sooner than a human blink, making it nearly undetectable to customers.
The second approach exploits a race situation in Android’s enter system by flooding the machine with keystrokes whereas switching USB roles. The third technique makes use of preliminary USB entry to ascertain a Bluetooth connection, making a secondary channel for enter injection.
The researchers demonstrated that ChoiceJacking assaults work on each locked and unlocked gadgets, relying on the producer. For 2 distributors, Honor and Oppo, the assaults can extract information even from locked gadgets. On Xiaomi gadgets, the assault can acquire improvement entry even on gadgets not beforehand enabled for debugging.
Assault Demo
Public charging infrastructure in airports, resorts, cafes, and transportation hubs represents the first assault vector. “Cell gadgets are generally hooked up to rented chargers whereas utilizing navigation apps, the place the person’s consideration is targeted on the environment reasonably than the display screen,” the researchers famous.
Main know-how firms have acknowledged the menace and are implementing fixes. Google assigned the vulnerability CVE-2024-43085 and launched patches within the November 2024 Android Safety Bulletin.
Samsung obtained CVE-2024-20900 for the assault precept and has begun rolling out enhancements. Apple has added person authentication prompts for USB connections in iOS 17.51.
Safety specialists advocate utilizing private charging cables with wall adapters as an alternative of public USB ports, carrying transportable battery packs, and maintaining machine software program updated with the most recent safety patches. USB information blockers, which forestall information switch whereas permitting for charging, present an extra layer of safety.
The invention highlights the evolving nature of cybersecurity threats and the significance of sustaining strong defenses as assault methods grow to be more and more refined.
Attempt in-depth sandbox malware evaluation for your SOC staff. Get ANY.RUN particular provide solely till Might 31 -> Attempt Right here