Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Vulnerabilities in Citrix Clients Pose Security Risks

Critical Vulnerabilities in Citrix Clients Pose Security Risks

Posted on July 18, 2026 By CWS

Cloud Software Group has recently identified two significant security vulnerabilities in Citrix software used on Windows systems. These vulnerabilities affect the Citrix Secure Access Client and the Citrix Endpoint Analysis Client, creating potential pathways for unauthorized users to gain elevated privileges.

Details of the Vulnerabilities

The most critical vulnerability, CVE-2026-53565, has been given a high CVSS v4.0 score of 8.5. This flaw arises from improper management of user privileges, allowing attackers with minimal access the opportunity to escalate their rights to the SYSTEM level. This flaw is present in both the Citrix Secure Access Client and the Endpoint Analysis Client for Windows.

The vulnerability is particularly concerning due to its ease of exploitation. According to its CVSS vector, the attack requires only local access and does not necessitate user interaction, yet it can compromise the system’s confidentiality, integrity, and availability.

Secondary Vulnerability Impact

The second vulnerability, CVE-2026-53566, involves an out-of-bounds memory read and is rated 6.8 on the CVSS scale. It specifically affects the Citrix Secure Access Client when the DNE (Deterministic Network Enhancer) driver is absent. While this flaw does not allow full system compromise, it still risks data confidentiality.

Both vulnerabilities can be exploited by a typical user without needing special interaction, highlighting the urgency for an update to mitigate these risks.

Recommendations for Mitigation

Organizations using these Citrix clients on their Windows endpoints are urged to prioritize these vulnerabilities. This is especially critical for environments with shared access, such as workstations and virtual desktop infrastructure setups.

To mitigate these threats, Cloud Software Group advises updating the Citrix Secure Access Client to version 26.6.1.20 or later, and the Endpoint Analysis Client to version 26.5.1.7 or later. For CVE-2026-53566, checking the DNE driver installation status is recommended to assess potential exposure.

Given the ease with which CVE-2026-53565 can be exploited, it is imperative that all deployments of the affected clients are considered at risk until appropriate patches are applied.

Significance and Future Considerations

The potential for privilege escalation in enterprise environments due to CVE-2026-53565 cannot be ignored, as it undermines core security principles. Attackers gaining SYSTEM privileges can take complete control of the system, necessitating immediate patching efforts.

The vulnerabilities were responsibly disclosed by Carlos Garrido of Pentraze Cybersecurity, allowing Cloud Software Group to coordinate a remediation strategy. Security teams should expedite patch deployments and verify endpoint configurations to ensure compliance and protection against these vulnerabilities.
Cyber Security News Tags:Citrix, Cloud Software Group, CVE-2026-53565, CVE-2026-53566, endpoint security, Patching, privilege escalation, Security, Vulnerabilities, Windows clients

Post navigation

Previous Post: Critical wp2shell RCE Vulnerability Threatens WordPress Sites
Next Post: Spirals Ransomware Quickly Hits IT Firm with Web Shell

Related Posts

English-Speaking Cybercriminal Ecosystem ‘The COM’ Drives a Wide Spectrum of Cyberattacks English-Speaking Cybercriminal Ecosystem ‘The COM’ Drives a Wide Spectrum of Cyberattacks Cyber Security News
Threat Actors Mimic as HR Departments to Steal Your Gmail Login Credentials Threat Actors Mimic as HR Departments to Steal Your Gmail Login Credentials Cyber Security News
Critical Vulnerability in Meta’s Muse AI Agent Exposed Critical Vulnerability in Meta’s Muse AI Agent Exposed Cyber Security News
Chinese ‘Salt Typhoon’ Hackers Hijacked US National Guard Network for Nearly a Year Chinese ‘Salt Typhoon’ Hackers Hijacked US National Guard Network for Nearly a Year Cyber Security News
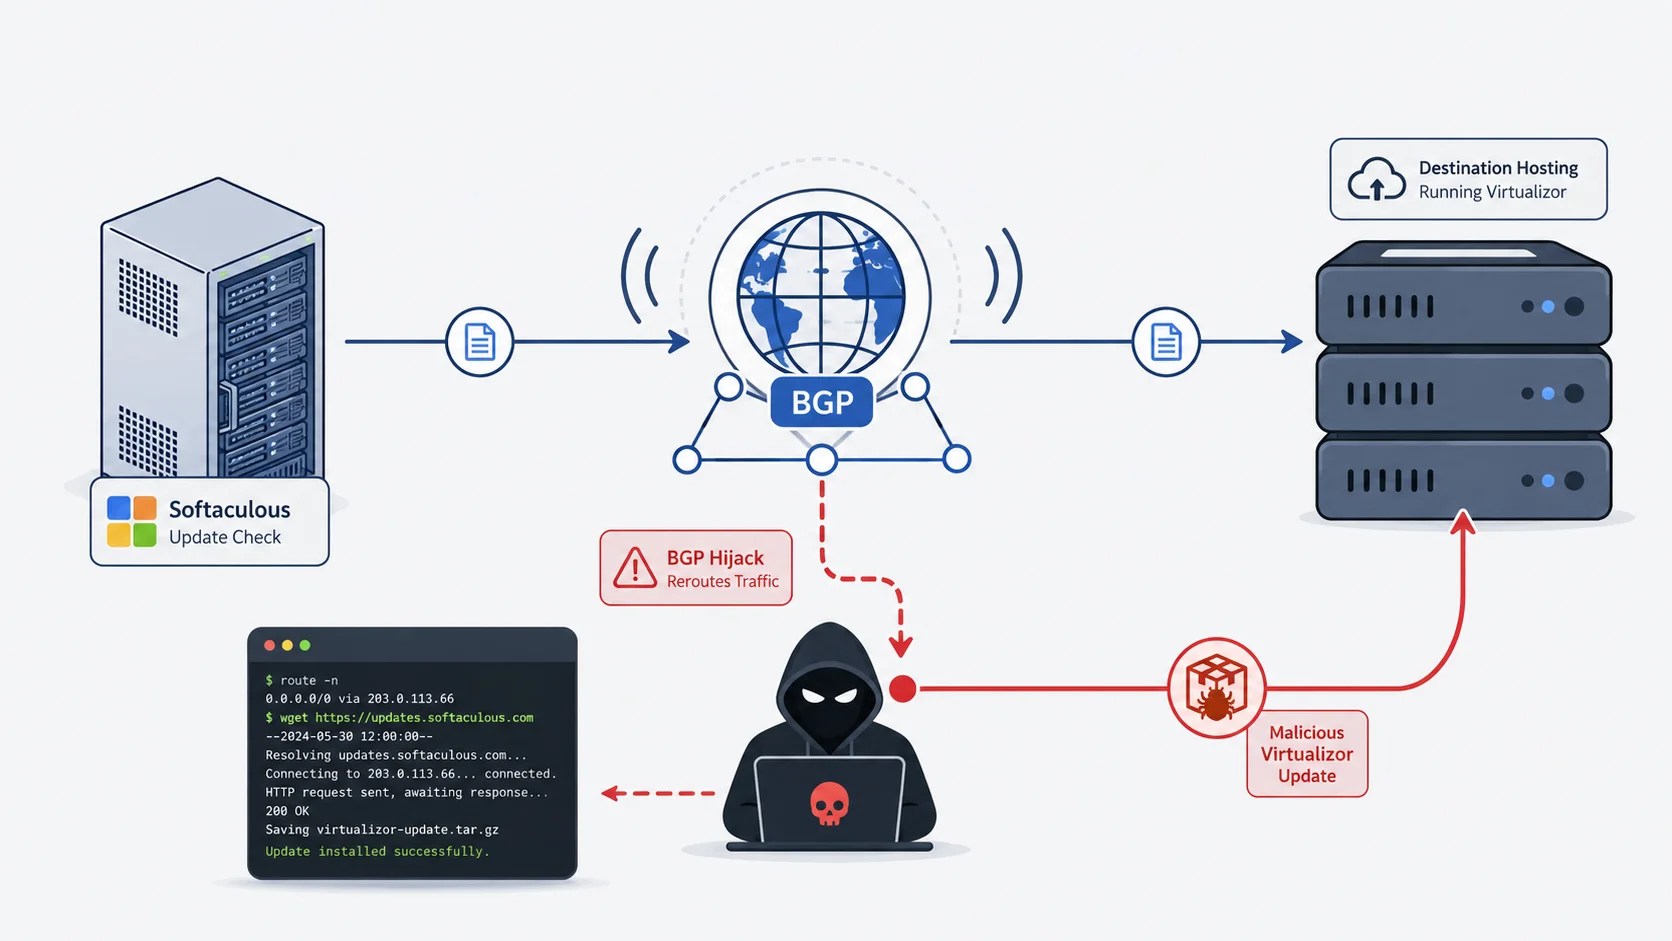
BGP Hijack Targets Softaculous, Delivers Malicious Update BGP Hijack Targets Softaculous, Delivers Malicious Update Cyber Security News
Critical RCE Vulnerability in Hugging Face’s LeRobot Critical RCE Vulnerability in Hugging Face’s LeRobot Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Claude AI Unravels 25-Year NSA Cryptography Enigma Swiftly
  • Hackers Breach Microsoft 365 Using ConnectWise Backup
  • Israeli Firm’s Role in Global Spyware Campaign Uncovered
  • Malicious npm Package ‘imgdecode’ Found in Supply Chain Attack
  • Critical Flaw in Collabora Online Jeopardizes Nextcloud Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Claude AI Unravels 25-Year NSA Cryptography Enigma Swiftly
  • Hackers Breach Microsoft 365 Using ConnectWise Backup
  • Israeli Firm’s Role in Global Spyware Campaign Uncovered
  • Malicious npm Package ‘imgdecode’ Found in Supply Chain Attack
  • Critical Flaw in Collabora Online Jeopardizes Nextcloud Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark