Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Cloudflare Security Gaps Exploited to Run Malicious Scripts

Cloudflare Security Gaps Exploited to Run Malicious Scripts

Posted on October 28, 2026 By CWS

Security researchers from Searchlight Cyber have discovered a method to execute JavaScript on websites using Cloudflare, despite restrictions meant to prevent such actions. Their findings highlight vulnerabilities in Cloudflare’s image processing features that allow for the exploitation of security protocols.

Revealing the Vulnerabilities

Published by Kevin Gervot and Adam Kues on October 28, 2026, the report titled ‘Cache Me If You Can’ unveils a working cross-site scripting (XSS) vulnerability through Cloudflare’s /cdn-cgi/image/ endpoint. The documentation does not specify a CVE or indicate whether a patch is available, urging users to consult Cloudflare for updates.

Cloudflare, a major player in website security, integrates a managed /cdn-cgi/ path into the domains of participating sites. This path handles various functions, including image transformations, but its presence also enables potential security breaches.

How the Exploit Works

The researchers identified that Cloudflare’s SVG image processing tool, svg-hush, built on the xml-rs library, mishandles certain attribute values. While it escapes standard attributes, namespace values are not properly sanitized, allowing for the insertion of malicious code.

By exploiting this oversight, attackers can bypass the Content Security Policy (CSP) and insert script tags, even though Cloudflare enforces a strict default-source policy that typically blocks scripts. The vulnerability capitalizes on cache-control headers that Chromium browsers handle in a specific manner, leading to a failure in maintaining CSP on subsequent loads.

Broader Implications and Precautions

This method of bypassing security measures is not restricted to Cloudflare alone. Researchers replicated similar tactics on platforms like Netlify Image CDN, Amazon S3, and Google Cloud Storage. These services can inadvertently override security protocols through misconfigured headers.

The research underscores the importance of not solely relying on file content for security validation. Instead, headers must be carefully managed to prevent unauthorized access. Measures such as setting X-Content-Type-Options to nosniff and securing open redirects are crucial defensive strategies.

In conclusion, this research serves as a reminder of the complexities involved in web security. As cyber threats grow more sophisticated, particularly with the aid of AI, organizations must ensure that their defenses are robust and capable of operating at the speed of potential attacks.
Cyber Security News Tags:Bypass, cache control, Chromium, Cloudflare, Content-Security-Policy, CVE, Cybersecurity, image transformation, JavaScript, open redirect, security flaws, SVG images, web security, XSS

Post navigation

Previous Post: Critical Vulnerabilities in Adobe and Google Exploited
Next Post: Modern Malware Tactics: Pre-Delivery Strategies Revealed

Related Posts

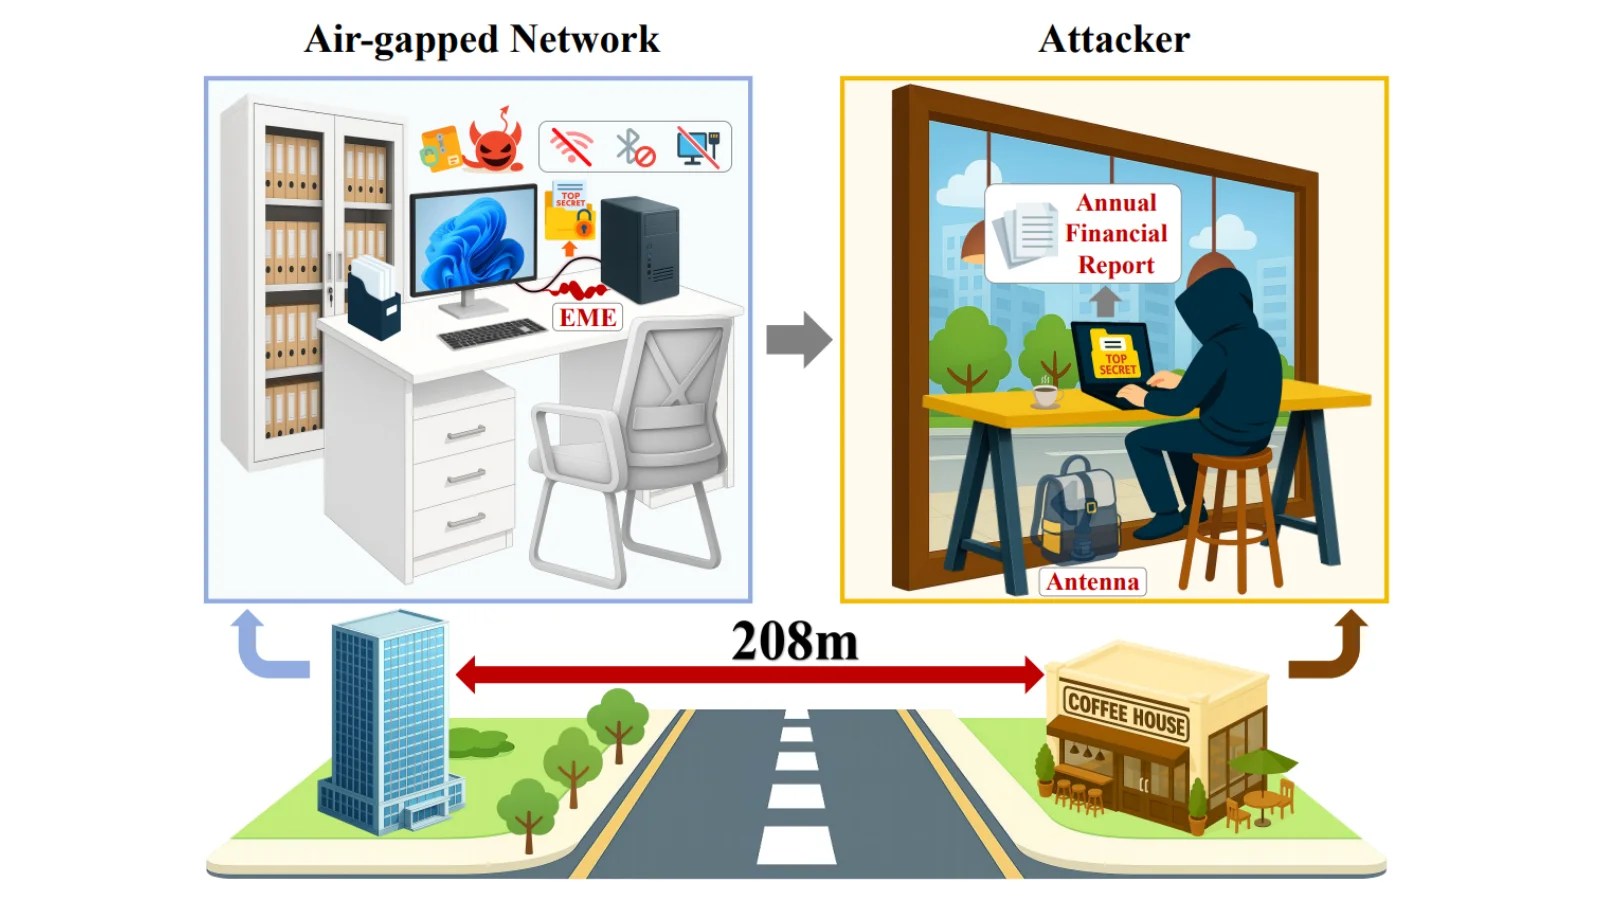
TrojPix Hack Threatens Air-Gapped Computers TrojPix Hack Threatens Air-Gapped Computers Cyber Security News
Storm-0900 Hackers Leveraging Parking Ticket and Medical Test Themes in Massive Phishing Attack Storm-0900 Hackers Leveraging Parking Ticket and Medical Test Themes in Massive Phishing Attack Cyber Security News
Critical Cisco SD-WAN Flaw Allows Root Command Execution Critical Cisco SD-WAN Flaw Allows Root Command Execution Cyber Security News
What Businesses Need to Know What Businesses Need to Know Cyber Security News
BADBOX 2.0 Infected Over 1 Million Android Devices Worldwide BADBOX 2.0 Infected Over 1 Million Android Devices Worldwide Cyber Security News
Critical Jenkins Flaw Enables Malicious Code Execution Critical Jenkins Flaw Enables Malicious Code Execution Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Modern Malware Tactics: Pre-Delivery Strategies Revealed
  • Cloudflare Security Gaps Exploited to Run Malicious Scripts
  • Critical Vulnerabilities in Adobe and Google Exploited
  • Critical TeamViewer Vulnerabilities Demand Immediate Update
  • Logic Flaws Alone Breach Microsoft Edge at Pwn2Own

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Modern Malware Tactics: Pre-Delivery Strategies Revealed
  • Cloudflare Security Gaps Exploited to Run Malicious Scripts
  • Critical Vulnerabilities in Adobe and Google Exploited
  • Critical TeamViewer Vulnerabilities Demand Immediate Update
  • Logic Flaws Alone Breach Microsoft Edge at Pwn2Own

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark