Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical SharePoint Flaw Allows Remote Code Execution

Critical SharePoint Flaw Allows Remote Code Execution

Posted on August 12, 2026 By CWS

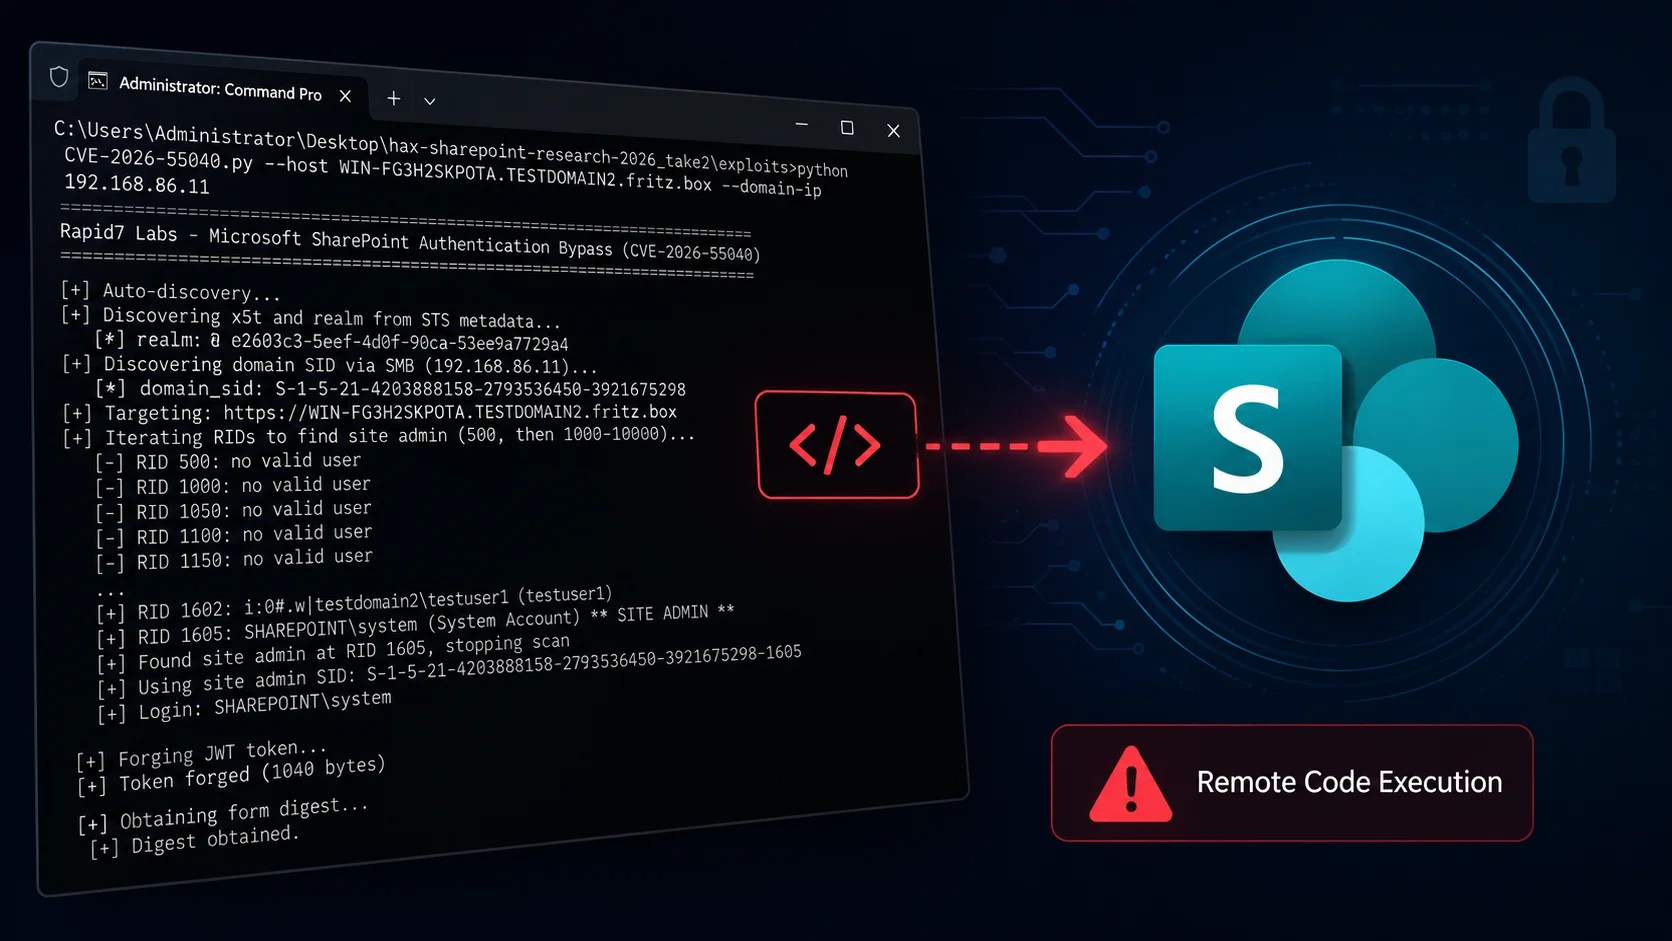
A recently identified vulnerability in Microsoft SharePoint Server is raising alarms throughout IT departments as security experts warn about its potential to allow remote execution of malicious code without authentication.

Known as CVE-2026-63520, this flaw was discovered by Rapid7 Labs during a focused zero-day research project and has been publicly disclosed in collaboration with Microsoft.

Understanding the Exploit Chain

The vulnerability is part of a two-stage exploit chain, with the first component, CVE-2026-55040, revealed the previous month. When these vulnerabilities are combined, they enable remote code execution (RCE) on vulnerable SharePoint servers without authentication.

Research conducted by Rapid7 indicates that CVE-2026-63520 impacts all supported versions of Microsoft SharePoint, as well as certain versions of Microsoft Project Server and Microsoft Office Web Apps Server. However, the primary testing was conducted on SharePoint deployments.

Technical Details of the Vulnerability

The flaw stems from an unsafe .NET type instantiation issue found in SharePoint’s Business Connectivity Services, which facilitates interaction with external data sources. This weakness allows attackers to execute arbitrary code using the privileges of the SharePoint Site’s service account, gaining unauthorized access to an organization’s internal systems.

Microsoft’s summary highlights inadequate input validation in Office SharePoint as the core issue, making it possible for unauthorized code execution over networks.

This poses significant risks, especially for organizations with internet-facing or poorly segmented SharePoint servers, potentially exposing sensitive data and connected enterprise applications to attackers.

Mitigation and Recommendations

As of the disclosure, there have been no public exploits or proof-of-concept codes, though Microsoft rates the exploitability as “more likely,” suggesting a high potential for attackers to take advantage soon.

While the CVSS score denotes a high attack complexity, requiring precise conditions and substantial effort to exploit, organizations are strongly advised to apply all relevant security updates immediately.

Administrators should ensure all applicable patches are installed, as updates can be applied in any order but must be comprehensive to provide full protection. This is particularly crucial for those managing SharePoint Server 2016 and SharePoint Enterprise Server 2016, which share patch requirements.

In light of the recent vulnerabilities, security teams should prioritize SharePoint patch management and continuously audit deployments to prevent potential future exploits.

Researcher Stephen Fewer from Rapid7, who discovered the vulnerability, stresses the importance of analyzing chained vulnerabilities to uncover deeper structural weaknesses in enterprise platforms.

Organizations are encouraged to review their SharePoint systems, confirm patch levels, and monitor for unusual activity in the Business Connectivity Services as a preventive measure.
Cyber Security News Tags:Business Connectivity Services, CVE-2026-63520, Cybersecurity, enterprise security, IT security, Microsoft, patch management, Rapid7, remote code execution, security update, SharePoint, Vulnerability, zero-day

Post navigation

Previous Post: Cisco Addresses Zero-Day Firewall Flaw Amid Active Exploitation
Next Post: Lazarus Group Exploits Windows Vulnerability for Rootkit Deployment

Related Posts

Threat Actors Weaponize Discord Webhooks for Command and Control with npm, PyPI, and Ruby Packages Threat Actors Weaponize Discord Webhooks for Command and Control with npm, PyPI, and Ruby Packages Cyber Security News
Securing Legacy Systems Strategies for Modernizing Old Tech Securing Legacy Systems Strategies for Modernizing Old Tech Cyber Security News
Iranian Hackers Target Omani Ministries: Data Theft Uncovered Iranian Hackers Target Omani Ministries: Data Theft Uncovered Cyber Security News
Zerobot Malware Targets Tenda Routers and n8n Platforms Zerobot Malware Targets Tenda Routers and n8n Platforms Cyber Security News
Zimbra Vulnerability Exploitation Demands Immediate Action Zimbra Vulnerability Exploitation Demands Immediate Action Cyber Security News
Fired Intel Engineer Stolen 18,000 Files Many of which Were Classified as “Top Secret” Fired Intel Engineer Stolen 18,000 Files Many of which Were Classified as “Top Secret” Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark