Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Target FortiGate VPN Vulnerability in Thai Broadband Attack

Hackers Target FortiGate VPN Vulnerability in Thai Broadband Attack

Posted on September 14, 2026 By CWS

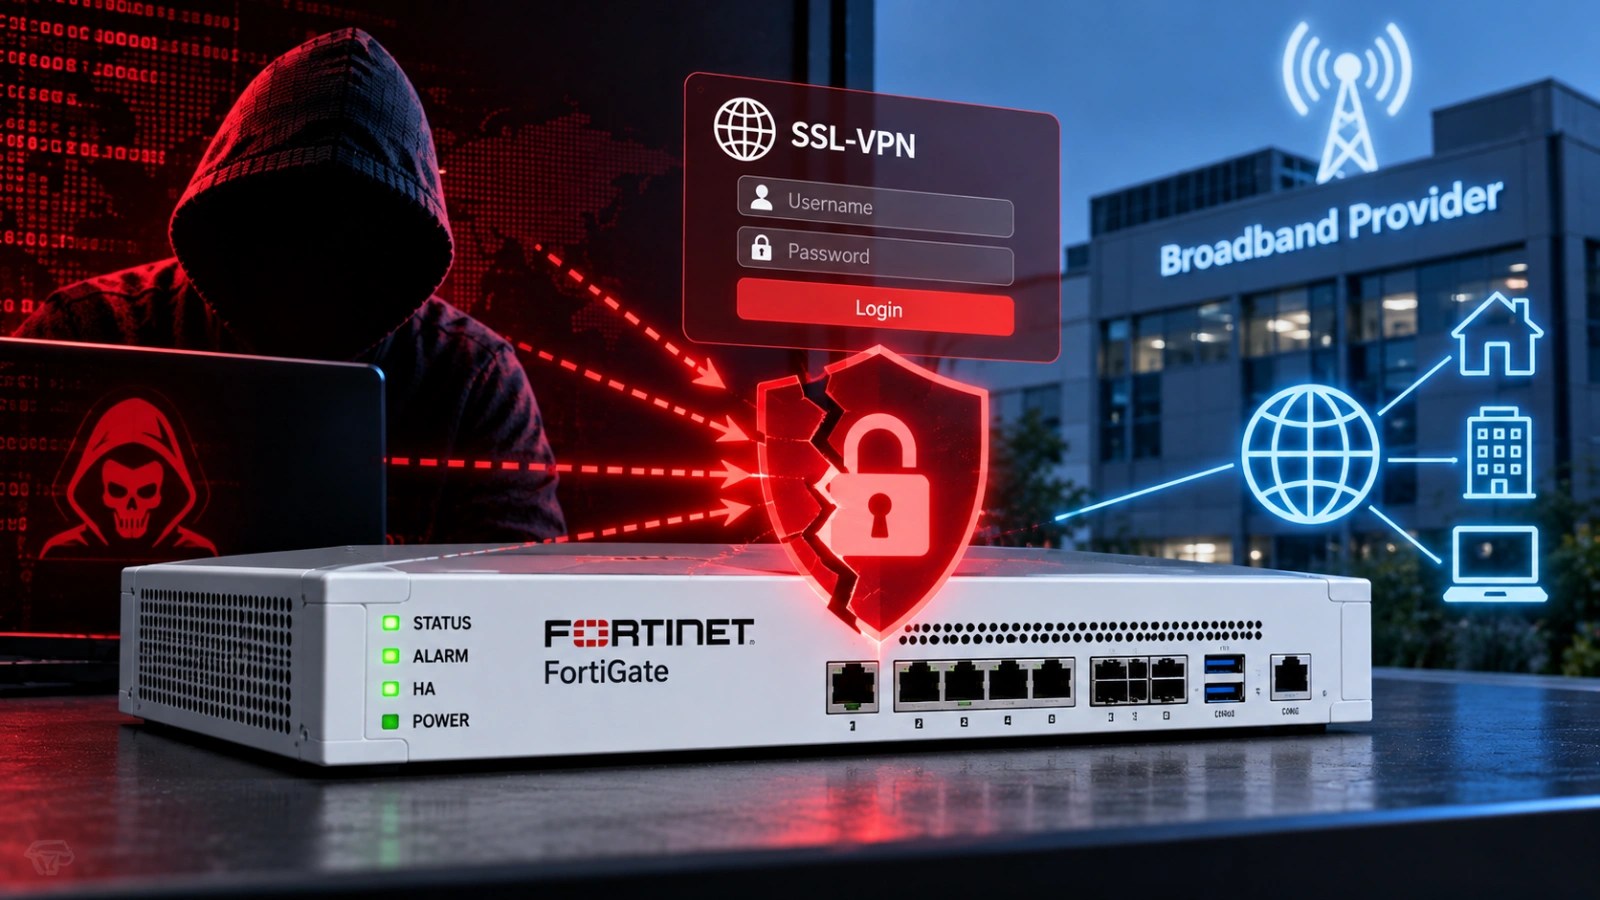
Security researchers have discovered a sophisticated cyber attack targeting Thailand’s Triple T Broadband, which operates under the consumer brand 3BB. The breach was linked to a critical SSL-VPN vulnerability in FortiGate devices, allowing attackers to escalate privileges, steal credentials, and gain persistent access to the network.

Uncovering the Attack Methodology

Hunt.io researchers first identified an open directory linked to the attack on June 3, 2026. Located at 92.63.180[.]133:8888 and hosted on Bangmod Enterprise infrastructure, the server contained an array of tools and scripts. These included FortiGate exploitation scripts, SSH brute-force utilities, and database credential harvesters, providing a comprehensive view of the hacker’s operations.

Evidence pointed to the attackers exploiting a FortiGate 60F SSL-VPN vulnerability, specifically CVE-2024-21762, which was added to CISA’s Known Exploited Vulnerabilities catalog earlier in the year. This vulnerability, with a CVSS score of 9.8, allows unauthenticated attackers to execute arbitrary commands through crafted HTTP requests.

Detailed Analysis of the Exploitation

The attackers used controlled crashes and malformed HTTP requests to determine the vulnerability of the FortiGate appliance. The final exploit involved advanced techniques, such as heap spraying and return-oriented programming, to establish a reverse shell to their server.

Further analysis revealed the use of MeshCentral as a remote management tool, installed to maintain persistent access within the network. The MeshCentral configuration directed infected machines to connect over port 443, with several systems reportedly under active administrative control during the attack.

Implications and Recommendations

The attackers demonstrated extensive knowledge of the 3BB network, employing various scripts to probe for vulnerabilities and escalate privileges on compromised Linux servers. They also targeted other systems, including a CodeIgniter-based sales portal and a Pentaho server, using known vulnerabilities like Dirty COW and Ghostcat.

Organizations potentially affected by similar threats should investigate unusual MeshCentral agent activity, connections to suspicious domains, and unexplained gaps in security logs. Immediate actions include rotating sensitive credentials and preserving forensic evidence to counteract the attack’s anti-forensic measures.

Fortinet has identified several FortiOS versions vulnerable to this exploit and recommends upgrading to a supported fixed release. Disabling SSL-VPN entirely can serve as a temporary measure if patching is not immediately possible.

The breach highlights the critical importance of promptly addressing known vulnerabilities and implementing comprehensive security measures to safeguard network infrastructure.
Cyber Security News Tags:3BB, broadband provider, CVE-2024-21762, cyber attack, Cybersecurity, data breach, Fortigate, Fortinet, MeshCentral, network security, SSL-VPN, Thailand, Triple T Broadband, VPN vulnerability, vulnerability exploitation

Post navigation

Previous Post: New DDRop Attack Targets Intel and AMD Confidential Computing
Next Post: Red Heron Uses Gitea Exploit to Breach Global Firms

Related Posts

5 Immediate Steps to be Followed After Clicking on a Malicious Link 5 Immediate Steps to be Followed After Clicking on a Malicious Link Cyber Security News
PipeMagic Malware Mimic as ChatGPT App Exploits Windows Vulnerability to Deploy Ransomware PipeMagic Malware Mimic as ChatGPT App Exploits Windows Vulnerability to Deploy Ransomware Cyber Security News
Microsoft to End Copilot Podcasts in 2026 Microsoft to End Copilot Podcasts in 2026 Cyber Security News
Top Ransomware Protection Tools for 2026 Top Ransomware Protection Tools for 2026 Cyber Security News
WhatsApp Malware Targets Windows Users Globally WhatsApp Malware Targets Windows Users Globally Cyber Security News
APT36 Hackers Attacking Indian Defense Personnel in Sophisticated Phishing Attack APT36 Hackers Attacking Indian Defense Personnel in Sophisticated Phishing Attack Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • MATCHBOIL Deploys Backdoor via Hidden Servers
  • AhsayCBS Flaws Actively Exploited, Urgent Action Needed
  • Hackers Break Into Google Pixel 10 at Pwn2Own Contest
  • Critical Flaw in React Server Components Puts Next.js Servers at Risk
  • Android Devices with Preinstalled Malware Threaten Users Globally

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • MATCHBOIL Deploys Backdoor via Hidden Servers
  • AhsayCBS Flaws Actively Exploited, Urgent Action Needed
  • Hackers Break Into Google Pixel 10 at Pwn2Own Contest
  • Critical Flaw in React Server Components Puts Next.js Servers at Risk
  • Android Devices with Preinstalled Malware Threaten Users Globally

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark