Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
LLMjacking: Exploiting AWS Keys for AI Model Access

LLMjacking: Exploiting AWS Keys for AI Model Access

Posted on September 3, 2026 By CWS

Cybersecurity experts have uncovered a new vector of attack known as LLMjacking, which involves exploiting leaked AWS credentials to gain unauthorized access to high-value AI models. This method allows attackers to rapidly convert a compromised identity management key into a profitable tool by subscribing to premium AI services.

Understanding the LLMjacking Technique

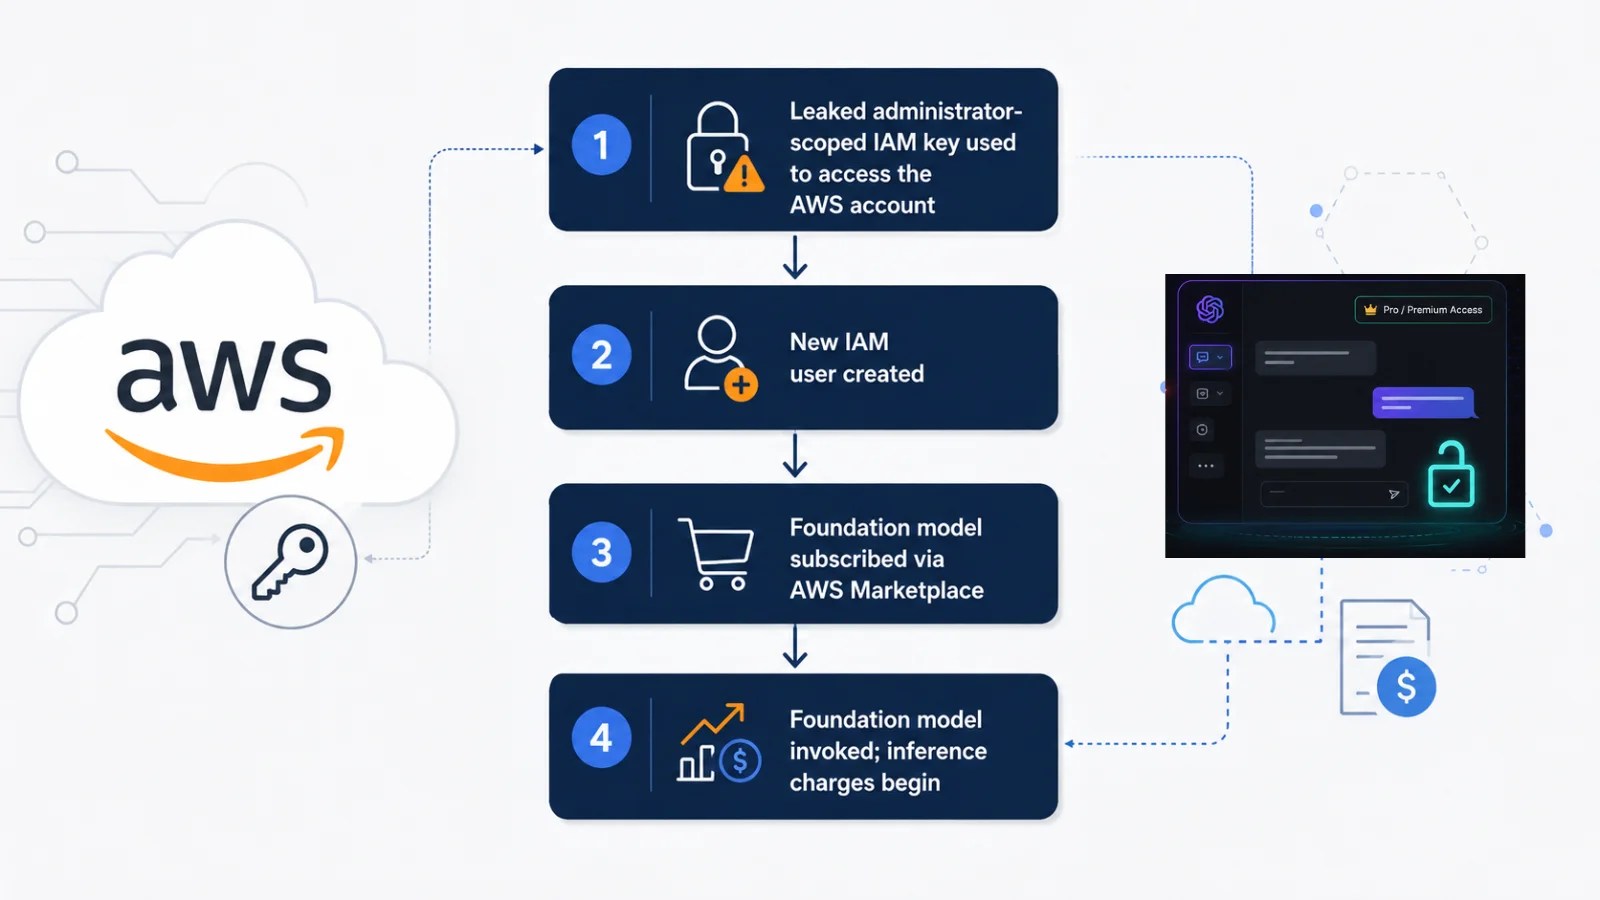
Researchers at FortiGuard Labs identified this breach as originating from an AWS Identity and Access Management (IAM) key with AdministratorAccess privileges. Once attackers acquired this key, they quickly established a new IAM user within the victim’s account to access AI models available on the AWS Marketplace. By executing CreateAgreementRequest and AcceptAgreementRequest, they secured subscriptions to these models.

This unauthorized access enabled the attackers to initiate model inference operations, subsequently billing the legitimate account holder. Additionally, they generated API keys specific to the AWS Bedrock service, providing an alternative method to exploit the system, thus evading detection.

Economic Implications of LLMjacking

The LLMjacking approach differs from traditional cloud abuses like cryptomining. Instead of extracting data, attackers monetize the victim’s billing relationship with the cloud provider. Premium AI models, such as Claude 2.x, can cost victims upwards of $46,000 daily, and this number can exceed $100,000 when escalating to even more advanced models like Claude 3 Opus.

FortiGuard Labs reported that illicit access is often resold as discounted AI chatbot subscriptions on platforms like Telegram and Discord. One operation, termed Operation Bizarre Bazaar, was linked to over 35,000 attack sessions across more than 30 AI model providers.

Detecting and Preventing LLMjacking

Detecting LLMjacking can be challenging due to its use of valid credential permissions, making it appear as legitimate usage. Conventional monitoring methods struggle to identify this type of abuse since the activity does not inherently appear malicious.

To combat such threats, FortiGuard Labs advises enabling AWS CloudTrail across all accounts to trace the complete sequence of identity creation and marketplace activities. Activating Bedrock invocation logging is also crucial, as it provides detailed request-level insights absent in CloudTrail logs. Organizations should prioritize using short-lived, role-assumed credentials over long-lived IAM keys to mitigate risks.

Furthermore, first-time usage of Bedrock services should not be presumed safe solely; it becomes noteworthy when combined with unusual signals like new identities, unexpected IP addresses, or unusual patterns in access-denied errors.

Adopting these strategies can significantly enhance an organization’s defense against sophisticated attacks such as LLMjacking, safeguarding their resources and financial assets.
Cyber Security News Tags:AI chatbot, AI models, AWS Marketplace, AWS security, Bedrock service, Claude models, cloud computing, cloud intrusion, CloudTrail, Cybersecurity, FortiGuard Labs, IAM keys, LLMjacking, Operation Bizarre Bazaar

Post navigation

Previous Post: Capsule Security Unveils AI Circuit Breaker for Rogue Agents
Next Post: BraZetsu Malware Transforms Windows Systems into Crime Network

Related Posts

Critical SolarWinds Serv-U Vulnerabilities Let Attackers Execute Malicious Code Remotely as Admin Critical SolarWinds Serv-U Vulnerabilities Let Attackers Execute Malicious Code Remotely as Admin Cyber Security News
Hackers Compromised Official Gaming Mouse Software to Deliver Windows-based Xred Malware Hackers Compromised Official Gaming Mouse Software to Deliver Windows-based Xred Malware Cyber Security News
Critical HP Linux Printing Software Flaw Threatens Security Critical HP Linux Printing Software Flaw Threatens Security Cyber Security News
AI-Powered Ransomware Is the Emerging Threat That Could Bring Down Your Organization AI-Powered Ransomware Is the Emerging Threat That Could Bring Down Your Organization Cyber Security News
Tenda N300 Vulnerabilities Let Attacker to Execute Arbitrary Commands as Root User Tenda N300 Vulnerabilities Let Attacker to Execute Arbitrary Commands as Root User Cyber Security News
Cybercriminals Exploit Microsoft Tools in New Phishing Scheme Cybercriminals Exploit Microsoft Tools in New Phishing Scheme Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark