Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Malware Targets Argentine Courts with Fake Documents

Malware Targets Argentine Courts with Fake Documents

Posted on March 18, 2026 By CWS

A recent cyber attack is exploiting Argentina’s judicial sector by using counterfeit court documents to distribute a dangerous malware. Legal professionals are being deceived into installing this harmful software, which is part of a campaign known as Operation Covert Access.

The attackers are utilizing spear-phishing emails that closely resemble authentic court communications. These emails distribute a Rust-based Remote Access Trojan, COVERT RAT, which grants attackers persistent access to compromised systems.

Targeting the Legal Landscape

The campaign specifically targets Argentina’s legal framework, impacting federal courts, law firms, government justice departments, academic bodies, and advocacy groups. By focusing on genuine court rulings related to preventive detention, the attackers exploit the inherent trust in legal documents, making the campaign exceptionally effective.

Point Wild analysts, expanding on research by Seqrite, have examined the operation in detail. They outlined the PowerShell execution flow and payload retrieval methods, highlighting the sophisticated, multi-layered approach aimed at remaining undetected within institutional networks.

Advanced Threat Capabilities

Beyond simple data surveillance, COVERT RAT connects to a command-and-control server at 181.231.253.69:4444. This connectivity allows attackers to execute various malicious activities, such as file theft and ransomware deployment.

The malware’s modular structure facilitates credential harvesting, privilege escalation, and encrypted file operations. Its ability to erase all traces post-operation complicates forensic investigations, adding to the threat’s severity.

Complex Delivery and Execution

Attackers employ a layered delivery system, starting with a phishing email that includes a ZIP file with a Windows shortcut, a batch loader script, and a fake judicial PDF. When executed, the malicious script operates in the background while the decoy PDF appears genuine.

Upon opening the shortcut, PowerShell is triggered in a concealed mode, launching a batch script that downloads the RAT from a GitHub repository. This use of GitHub enhances the attack’s perceived legitimacy, as traffic to the platform often bypasses security alerts.

Security measures are essential for legal and judicial professionals. Keeping antivirus software updated, avoiding suspicious email attachments, and monitoring system processes are critical steps to mitigate such threats.

Stay informed by following us on social media platforms like Google News, LinkedIn, and X for more updates.
Cyber Security News Tags:Argentina, COVERT RAT, cyber attack, Cybersecurity, fake documents, judicial system, legal sector, Malware, Phishing, remote access trojan

Post navigation

Previous Post: Boggy Serpens Intensifies Cyberattacks on Global Targets
Next Post: WhatsApp View Once Bypass Found, Meta Won’t Fix

Related Posts

Aembit Expands Workload IAM to Microsoft Ecosystem, Enhancing Hybrid Security for Non-Human Identities Aembit Expands Workload IAM to Microsoft Ecosystem, Enhancing Hybrid Security for Non-Human Identities Cyber Security News
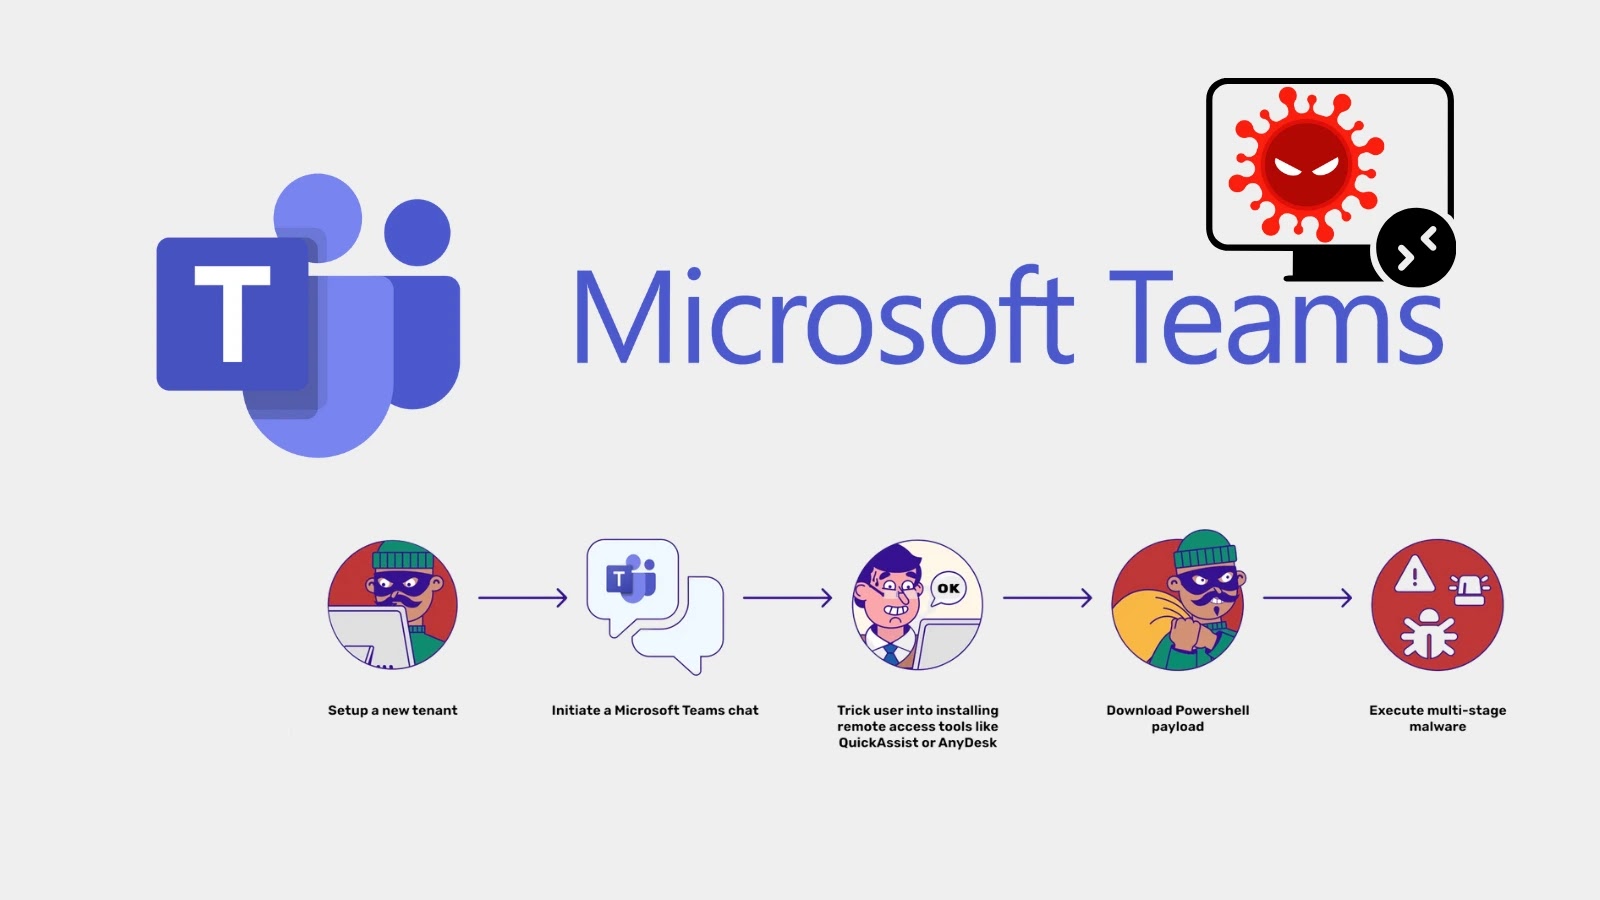
Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Cyber Security News
Palo Alto Networks, Zscaler, Jaguar Land Rover, and Cyber Attacks Palo Alto Networks, Zscaler, Jaguar Land Rover, and Cyber Attacks Cyber Security News
First Large-scale Cyberattack Using AI With Minimal Human Input First Large-scale Cyberattack Using AI With Minimal Human Input Cyber Security News
Threat Actors Weaponizing Facebook and Google Ads as Financial Platforms to Steal Sensitive Data Threat Actors Weaponizing Facebook and Google Ads as Financial Platforms to Steal Sensitive Data Cyber Security News
Cisco and Android Zero-Day Threats Highlight Cybersecurity Week Cisco and Android Zero-Day Threats Highlight Cybersecurity Week Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical Flaw in Drupal Commerce Threatens Online Stores
  • Scammers Mimic Polymarket to Defraud Cryptocurrency Users
  • Aur0ra Hackers Leverage AI for Domain Admin Access
  • NetamLoader Malware Targets Asian Government Windows 10 Systems
  • Enhancing Security in a Rapidly Evolving Threat Landscape

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical Flaw in Drupal Commerce Threatens Online Stores
  • Scammers Mimic Polymarket to Defraud Cryptocurrency Users
  • Aur0ra Hackers Leverage AI for Domain Admin Access
  • NetamLoader Malware Targets Asian Government Windows 10 Systems
  • Enhancing Security in a Rapidly Evolving Threat Landscape

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark