Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft’s Update Health Tools Configuration Vulnerability Let Attackers Execute Arbitrary Code Remotely

Microsoft’s Update Health Tools Configuration Vulnerability Let Attackers Execute Arbitrary Code Remotely

Posted on November 25, 2025November 25, 2025 By CWS

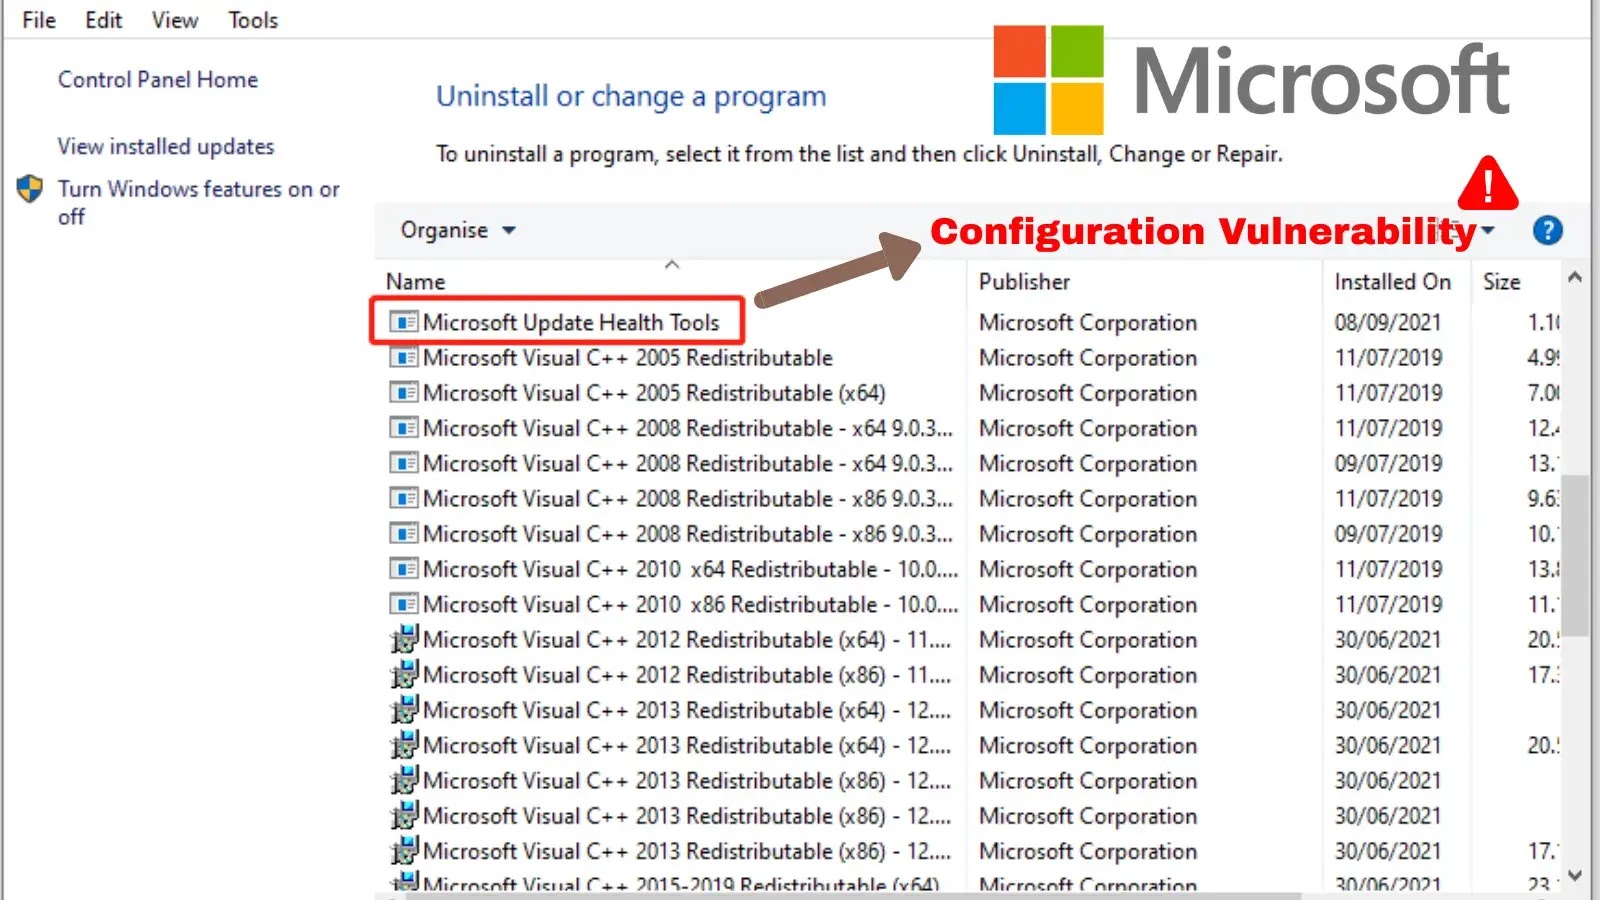
A vital distant code execution (RCE) vulnerability in Microsoft’s Replace Well being Instruments (KB4023057). A broadly deployed Home windows element designed to expedite safety updates by Intune.

The flaw stems from the device connecting to dropped Azure Blob storage accounts that attackers may register and management.​

How the Vulnerability Works

The vulnerability exists in model 1.0 of the Replace Well being Instruments, which makes use of Azure Blob storage accounts following a predictable naming sample (payloadprod0 by payloadprod15.blob.core.home windows.web) to fetch configuration information and instructions.

Eye Safety researchers discovered that Microsoft had left 10 of the 15 storage accounts unregistered and unused.

After registering these deserted endpoints, the researchers noticed over 544,000 HTTP requests inside seven days from almost 10,000 distinctive Azure tenants worldwide.

The device’s uhssvc.exe service, positioned at C:Program FilesMicrosoft Replace Well being Instruments, was actively resolving these domains throughout a number of enterprise environments.​

uhssvc.exe file

The vital subject lies within the device’s “ExecuteTool” motion, which permits execution of Microsoft-signed binaries.

By crafting malicious JSON payloads that time to respectable Home windows executables corresponding to explorer.exe, attackers can obtain arbitrary code execution on susceptible techniques.​

The newer model 1.1 implements a correct net service at devicelistenerprod.microsoft.com, although backward-compatibility choices may nonetheless expose techniques.​

Eye Safety reported the vulnerability to Microsoft on July 7, 2025, and Microsoft confirmed the habits on July 17.

Hashicorp researchers transferred possession of all compromised storage accounts again to Microsoft on July 18, 2025, successfully closing the assault vector.​

Organizations ought to guarantee they’re operating the newest model of Replace Well being Instruments and confirm no legacy configurations stay enabled.

Safety groups ought to monitor for uncommon community site visitors to Azure Blob storage endpoints from replace providers.​

Comply with us on Google Information, LinkedIn, and X for every day cybersecurity updates. Contact us to characteristic your tales.
Cyber Security News Tags:Arbitrary, Attackers, Code, Configuration, Execute, Health, Microsofts, Remotely, Tools, Update, Vulnerability

Post navigation

Previous Post: Canon Says Subsidiary Impacted by Oracle EBS Hack 
Next Post: HashiCorp Vault Vulnerability Allow Attackers to Authenticate to Vault Without Valid Credentials

Related Posts

Shai Hulud 2.0 Compromises 1,200+ Organizations, Exposing Critical Runtime Secrets Shai Hulud 2.0 Compromises 1,200+ Organizations, Exposing Critical Runtime Secrets Cyber Security News
Education-Themed Malicious Domains Linked to Bulletproof Hosting Infrastructure Exposed Education-Themed Malicious Domains Linked to Bulletproof Hosting Infrastructure Exposed Cyber Security News
TA829 Hackers Employs New TTPs and Upgraded RomCom Backdoor to Evade Detections TA829 Hackers Employs New TTPs and Upgraded RomCom Backdoor to Evade Detections Cyber Security News
175 Malicious npm Packages With 26,000 Downloads Attacking Technology, and Energy Companies Worldwide 175 Malicious npm Packages With 26,000 Downloads Attacking Technology, and Energy Companies Worldwide Cyber Security News
ThreatBook Peer-Recognized as a Strong Performer in the 2025 Gartner® Peer Insights™ Voice of the Customer for Network Detection and Response — for the Third Consecutive Year ThreatBook Peer-Recognized as a Strong Performer in the 2025 Gartner® Peer Insights™ Voice of the Customer for Network Detection and Response — for the Third Consecutive Year Cyber Security News
Ransomware Attack 2025 Recap – From Critical Data Extortion to Operational Disruption Ransomware Attack 2025 Recap – From Critical Data Extortion to Operational Disruption Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles
  • Critical Vulnerability in Oracle PeopleSoft Exploited Globally
  • Kiteworks Recommends Nine-Hour System Shutdown Amid Cyber Threat
  • New Botnet x47.c Leverages AI for Advanced Cyber Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles
  • Critical Vulnerability in Oracle PeopleSoft Exploited Globally
  • Kiteworks Recommends Nine-Hour System Shutdown Amid Cyber Threat
  • New Botnet x47.c Leverages AI for Advanced Cyber Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark